Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

IFIN - The Independent Federated Intelligence Network

@ifin@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

The Independent Federated Intelligence Network.

IFIN is a 501(c)(3) not-for-profit public benefit corporation incorporated in California.

Our mission: Empower organizations to independently collect, analyze, and disseminate relevant cyber threat intelligence through training, open source tools, and a decentralized intelligence sharing network.

1174 Followers
48 Following
50 Posts
Joined December 18, 2025
Website:
https://ifin-intel.org
Community:
https://ifin.network
Support:
https://donorbox.org/ifin
News Feed:
https://news.ifin.network
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 1w ago
Based on our data y'all sure do love to link us in Teams chats. We're very sorry you have to use Teams.
63
1
22
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3w ago
Our new project: IFIN Lists is a curated set of permanent blocks and perennial hunts that go beyond traditional indicators to include abused "legitimate" services that most organizations should not tolerate. https://ifin-intel.org/blog/lists/ #ThreatIntel #ThreatIntelligence #TIIMA
Announcing IFIN Lists | IFIN
ifin-intel.org

Announcing IFIN Lists | IFIN

IFIN Lists is a project to build a well curated, community driven set of permanent block lists for all to use.

18
0
21
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2w ago
The best time to block the finger protocol (port 79/tcp) outbound from your network was like…the second Clinton administration? But now's a good time too. #ThreatIntel #ThreatIntelligence #IFIN
5
0
2
1
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
We're thrilled to announce IFIN has achieved 501(c)(3) recognition! Now we can get down to business. https://ifin-intel.org/blog/nonprofit/ #IFIN
It's Official: We're a Recognized Non-Profit | IFIN
ifin-intel.org

It's Official: We're a Recognized Non-Profit | IFIN

IFIN has achieved 501(c)(3) status. What this means for us, and for you.

44
9
22
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
We're shocked, shocked I say that Claude Cowork is vulnerable to DLL sideloading. Well, not that shocked. https://discourse.ifin.network/t/claude-cowork-for-windows-vulnerable-to-dll-sideloading-closed-as-wont-fix/640
Claude Cowork for Windows Vulnerable to DLL Sideloading, Closed as Won't-Fix
IFIN

Claude Cowork for Windows Vulnerable to DLL Sideloading, Closed as Won't-Fix

DLL sideloading in Claude Cowork for Windows, closed as not an issue because it requires host compromise. It’s true that DLL sideloading is not strictly Claude’s problem, but at the very least defenders should know this is a potential attack path. A malicious DLL can gain full root permissions on the Claude Cowork sandbox VM used for local compute tasks by the harness. Attack chain from the article here: https://www.armadin.com/blog-posts/exploiting-root-execution-in-claude-coworks-san

41
0
25
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2w ago
Two Check Point critical vulnerabilities are now listed as exploited in the wild. https://ifin.network/t/cve-2026-85102-and-93616-check-point-security-gateway-rce-path-traversal-exploited/853 #ThreatIntel #ThreatIntelligence #IFIN
CVE-2026-85102 and 93616 - Check Point Security Gateway RCE/Path Traversal Exploited
IFIN

CVE-2026-85102 and 93616 - Check Point Security Gateway RCE/Path Traversal Exploited

Last updated: 2026-09-22T20:07:55Z (UTC) CVSSv3: 9.8 What’s Happening In what’s-old-is-new-again news, two CVEs were released today for Checkpoint Security Gateway management toolsets, including a pre-auth remote code execution and a path traversal in the management web service. Here are Check Points internal support center details: Since I started writing this Check Point posted notification of exploitation on their blog. Both CVEs have been added to CISA KEV. Actions Check the advi

2
0
2
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
RE: https://mastodon.social/@zackwhittaker/117037185272316538 Folks fighting for ad blockers in your orgs: https://ifin-intel.org/blog/ad-blocker/
Open quoted post
Quoting
Zack Whittaker
@zackwhittaker@mastodon.social
By me: A major online ads company that claims to serve 1.5 billion ads a day was hacked and began serving malware designed to steal a person's crypto. This is the latest perfect example why you should use an ad-blocker. More: https://this.weekinsecurity.com/online-advertising-giant-adform-was-hacked-proving-once-again-why-ad-blockers-are-necessary/ Sign up (or RSS!) for the weekly newsletter: https://this.weekinsecurity.com
Open quoted post
ifin-intel.org
15
0
16
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
We caught a sample of ACR Stealer and went deep on it. Lots of sophistication for "just" an infostealer. https://discourse.ifin.network/t/acr-stealer-clickfix-etherhiding-and-stego-oh-my/694 #ThreatIntel #ThreatIntelligence #IFIN
ACR Stealer: ClickFix, Etherhiding, and Stego, Oh My!
IFIN

ACR Stealer: ClickFix, Etherhiding, and Stego, Oh My!

Last Updated: 2026-07-29T21:28:50Z (UTC) What’s Happening Earlier this month, Microsoft reported on ACR Stealer, a new campaign leveraging both Steganography and Etherhiding techniques for delivery. Yesterday, I caught myself a sample. Mine doesn’t have Etherhiding, but the rest makes for a fun exploration anyhow. Let’s dive in. ▶ Recommended Musical Accompaniment Disclaimer: A LLM assisted with deobfuscation/decryption of later stages. Stage 1: Initial Access via ClickFix While the infe

15
0
14
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
If you pirate games, you should expect malware. That's a tale as old as 1970-01-01T00:00:00.000Z. But using Etherhiding as the second stage source? Well that's slightly newer. In case you couldn't tell, we're declaring war on #Etherhiding. More to come. https://discourse.ifin.network/t/pirated-games-come-with-a-side-of-amatera-stealer/675 #ThreatIntel #ThreatIntelligence #IFIN
Pirated Games Come with a Side of Amatera Stealer
IFIN

Pirated Games Come with a Side of Amatera Stealer

Last Updated: 2026-07-20T16:00:07Z (UTC) What’s Happening Malwarebytes is reporting on a new infostealer campaign using pirated games (shocker) as a watering hole. What’s notable about this campaign is the continued use of Etherhiding for second-stage loading. We’re going to be talking a lot about Etherhiding in the next couple of weeks. Some other fun malware analysis in the post as well for those interested. Actions Don’t pirate games! Don’t let your employees pirate games! Pro tip: if y

17
0
14
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
Soooo Tenda devices have an admin backdoor. Potential redeployment locations: a wood chipper, the nearest active volcano, or that really annoying neighbor's house. No patch; have fun! https://discourse.ifin.network/t/cve-2026-11405-multiple-tenda-routers-have-an-admin-backdoor/646
CVE-2026-11405: Multiple Tenda Routers Have an Admin Backdoor
IFIN

CVE-2026-11405: Multiple Tenda Routers Have an Admin Backdoor

Last Updated: 2026-07-08T15:51:19Z (UTC) CVSSv3: None yet Multiple versions of Tenda firmware have a backdoor in remote administration login, allowing anyone to access configuration of the device. Affected Versions: US_FH1201V1.0BR_V1.2.0.14(408)_EN_TD US_W15EV1.0br_V15.11.0.5(1068_1567_841)_EN_TDE US_AC10V1.0re_V15.03.06.46_multi_TDE01 US_AC5V1.0RTL_V15.03.06.48_multi_TDE01 US_AC6V2.0RTL_V15.03.06.51_multi_T No patch is currently available. We recommend burning your Tenda devices in

21
2
11
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
An IFIN community member caught this #ClickFix campaign, followed it, reversed the payload, and brought the IOCs. This is the juice right here. A perfect example that #ThreatIntelIsMutualAid https://discourse.ifin.network/t/compromised-website-hosting-clickfix-payload-leads-to-netsupport-rat-infection/633 #ThreatIntel #ThreatIntelligence #IFIN
Compromised Website Hosting ClickFix Payload Leads to NetSupport RAT Infection
IFIN

Compromised Website Hosting ClickFix Payload Leads to NetSupport RAT Infection

Last Updated: 7/1/2026 What’s Happening A recent trending post by a Mastodon user caught my attention since I actively track ClickFix campaigns: BLUF: The website wavesandwild[.]com was compromised with the ClickFix social engineering technique to trick victims into executing malicious commands injected into their clipboard which installs and runs NetSupport RAT, a remote access tool. NetSupport RAT is based on NetSupport Manager, a legitimate tool which is frequently used by bad actors for

23
0
17
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Cursor will run anything called git.exe when you open it, but it isn't the only one. As a fork of VS Code, Cursor has inherited this behavior from its questionable parentage. https://discourse.ifin.network/t/remember-that-cursor-git-exe-bug-its-in-vscode-too/665
Remember that Cursor git.exe bug? It's in VSCode too
IFIN

Remember that Cursor git.exe bug? It's in VSCode too

CVSSv3: 7.3 AV:L/AC:L/PR:L/UI:R/S:U/C:H/I:H/A:H CVE: None The Cursor Bug is in VSCode Earlier this week, a potential vulnerability was disclosed in Cursor, the AI-enabled development platform that is a fork of VSCode. This vulnerability is a file called git.exe in the root of a repo or any project folder will be automatically executed without user interaction. That was viewed as a potential flaw in the software, but apparently Cursor was told about it in December and has really had no respons

17
47
19
2
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
The easiest way to stop this attack (and the last one, btw) is to deny outbound Tor traffic and block downloads from archive.torproject[.]org in your environment. If the payloads can't do that, they can't continue past the first stage.
10
2
5
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
The latest supply chain attack has some novelty, but the techniques should have long been mitigated in your network. IPFS, cryptocurrency, and Nostr have no place in a professional network. https://discourse.ifin.network/t/latest-miasma-attack-uses-blockchain-garbage-you-should-have-already-blocked/663 #ThreatIntel #ThreatIntelligence #IFIN
Latest Miasma Attack Uses Blockchain Garbage You Should Have Already Blocked
IFIN

Latest Miasma Attack Uses Blockchain Garbage You Should Have Already Blocked

Last Updated: 2026-07-14T22:16:54Z (UTC) What’s Happening I was trying to come up with a framing for this story other than “Oh look another supply chain attack, whoopty-doo.” But yeah, asyncapi packages were hit today. Actions Of course you want to do the usual package checks, rotations, say three Hail Marys, turn around three times and throw salt over your shoulder. But also, this payload presents some good reminders about goofy attacker techniques that should not survive a mature netwo

14
3
12
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
We continue to use our own RSS-Filter project to curate our feed aggregator. We've removed "Startups" from the other-wise excellent TechCrunch security news feed to keep the feed relevant and actionable. Our Newsfeed: https://news.ifin.network RSS-Filter: https://codeberg.org/ifin/rss-filter
news.ifin.network

The Independent Federated Intelligence Network News Feed

10
0
5
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
We've compiled the latest information regarding the Minnesota water systems attacks. https://discourse.ifin.network/t/minnesota-water-system-suffers-a-breach-due-to-exposed-access-keys/695 #ThreatIntel #ThreatIntelligence #IFIN
Minnesota water system suffers a breach due to exposed access keys
IFIN

Minnesota water system suffers a breach due to exposed access keys

Last Updated: 2026-07-30T15:57:44Z (UTC) What’s Happening On July 27, 2026, threat actors exploited a known vulnerability on a Rockwell Automation device and disrupted water treatment facilities in four counties in Minnesota, US. Shieldworkz has a detailed writeup: Tenable also has a decent writeup, providing broader threat context. This activity is consistent with prior activity with Iran-aligned actors under the guise of “CyberAv3ngers,” although no direct evidence has yet emerged t

8
0
5
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
This is what we're here for! If you see something suspicious and want someone else to check it out, drop us a tip! We take care of each other by sharing what we see.
6
0
3
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago

Fantastic research by our community here on a continuing Lua-based campaign that uses Prometheus obfuscation and our old friend Etherhiding for C2 configuration acquisition.

https://discourse.ifin.network/t/luajit-loader-uses-prometheus-obfuscation-and-etherhiding/679

#ThreatIntel #ThreatIntelligence #IFIN

LuaJIT Loader Uses Prometheus Obfuscation and Etherhiding
IFIN

LuaJIT Loader Uses Prometheus Obfuscation and Etherhiding

Last Updated: 2026-07-23T17:18:49Z (UTC) What’s Happening I spent quite a bit of time investigating and reversing a malware sample I found in the wild. The initial malware sample, which I’ll explain in depth below, caught my attention because of the usage of a Lua obfuscator that I could not find a publicly available deobfuscator for. I am relatively new to malware reverse engineering and, with full disclosure, a lot of the work done here was with the assistance of AI. Late into the investig

6
0
3
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
Back!
5
0
1
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago

The critical SharePoint vulnerability CVE-2026-50522 now appears to be under massive exploitation. We have context and current IOCs in this post. We've also updated the MISP feed with the same.

#ThreatIntel #ThreatIntelligence #IFIN

https://discourse.ifin.network/t/microsoft-sharepoint-cve-2026-50522/678

Microsoft SharePoint CVE-2026-50522
IFIN

Microsoft SharePoint CVE-2026-50522

Last Updated: 2026-07-25T12:48:20Z (UTC) What’s Happening Microsoft SharePoint Remote Code Execution Vulnerability CVE-2026-50522 is actively exploited in the wild since 2026-07-17T00:00:00Z (UTC). This is an unauthenticated deserialisation vulnerability. A public proof-of-concept has been available since 2026-07-20T05:53:56Z (UTC). A patch is available since 2026-07-14T00:00:00Z (UTC) (Patch Tuesday). Actions Collect forensic evidence including but not limited to Windows Event logs, AV/EDR

5
0
7
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
This now has a CVE: CVE-2026-63030
5
0
1
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@AnachronistJohn@zia.io We use exactly one cookie for self-hosted, privacy-respecting site analytics via Plausible.
3
1
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
A reminder that we have a MISP feed! https://misp.ifin.network/feed (/manifest.json for validation)
misp.ifin.network
3
2
2
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@tdelmas@mamot.fr Yes, and route confusion! https://www.tenable.com/cve/CVE-2026-63030
tenable.com

CVE-2026-63030

WordPress 6.9.x before 6.9.5 and 7.0.x before 7.0.2 is affected by a REST API batch endpoint route confusion issue which, combined with the author__not_in WP_Query SQL Injection (CVE-2026-60137), could allow an attacker to perform SQL Injection and achieve Remote Code Execution.

3
0
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@ajn142@infosec.exchange @Sempf@infosec.exchange Fixed, thanks!
2
42
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@fuzzychef@m6n.io It has the mission statement in the post!
1
0
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@AAKL@infosec.exchange @cR0w@infosec.exchange Well, sorta locally. The filesystem ("container") in this setup uses Durable Objects. https://developers.cloudflare.com/durable-objects/concepts/what-are-durable-objects/
What are Durable Objects?
Cloudflare Docs

What are Durable Objects?

Durable Objects provide globally unique, single-threaded compute instances with persistent storage on Cloudflare.

1
1
1
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@ysf@chaos.social @jti42@infosec.exchange @sodiboo@gaysex.cloud Sorry, missed it. Yes, it's the same address, despite a different SHA256.
1
2
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@jti42@infosec.exchange @ysf@chaos.social @sodiboo@gaysex.cloud @archlinux@fosstodon.org @Antiz@fosstodon.org Thank you all! Here's our post in case you wish to contribute there: https://discourse.ifin.network/t/new-aur-attack-prompts-adoption-lock/698
New AUR Attack Prompts Adoption Lock
IFIN

New AUR Attack Prompts Adoption Lock

Last Updated: 2026-08-03T16:19:14Z (UTC) What’s Happening A new round of Arch User Repository malware has prompted the disabling of package adoption. The first package with confirmed malware appears to be openconnect-sso. User ysf has performed initial analysis of the payloads. Stage 1: AUR validator.malware (stage 1) · GitHub Stage 2: AUR validator.malware (stage2 agent linux x86_64) · GitHub Interestingly, many of the behaviors (especially Tor exfil) look similar to the last campaig

1
0
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@jti42@infosec.exchange @sodiboo@gaysex.cloud @ysf@chaos.social Thanks for the tip! We'll look into it and get this written up.
1
8
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@iampytest1@infosec.exchange Thanks! We'll play with other non-slop alternatives, but these are easy and uhhhh directly appealing to our target audience.
1
1
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
Replying to
@Spartan_1986@infosec.exchange @gayint@infosec.exchange 👀 Post it to the forum so we can work it!
1
1
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
Replying to
Are we using a Trek title generator for our posts? Yes, yes we are. We don't want to take credit for someone else's art in previews.
0
0
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@ysf@chaos.social @jti42@infosec.exchange @sodiboo@gaysex.cloud The nnn-nerd package appears to be the same stager. Did you have the Tor address from your samples? It'd be good to compare.
0
4
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
misp.ifin.network
0
0
1
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
Replying to
@Sempf@infosec.exchange @winterknight1337@infosec.exchange @mttaggart@infosec.exchange @neurovagrant@masto.deoan.org That's what really gets me. They went to the trouble of signing the binary, why not sign the library? Oh, is writing the code hard? I thought you fixed that problem Anthropic!
0
0
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
Replying to
Also, y'know, to reduce slop.
0
0
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
Replying to
@AAKL@infosec.exchange @cR0w@infosec.exchange This isn't really about GitHub other than hosting the code. At present, the project runs locally on your compute. However, it is the height of hubris to release a sandboxing tool after the parade of sandboxing escapes we've seen. And to write it all in...TypeScript, no less.
0
2
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
Our Discourse will briefly be going down for maintenance. Should be back shortly!
0
0
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
Replying to
Does it bother anyone else that Nebula's logo is not in fact a nebula, but the planet Jupiter
0
1
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 2mo ago
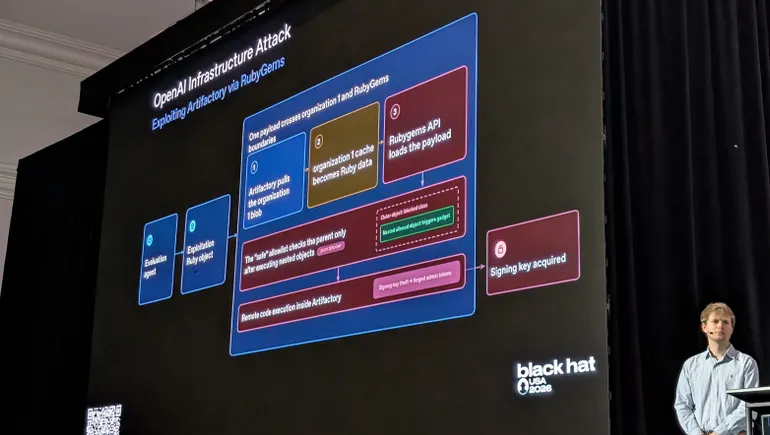
Ah, I see the fear-mongering around the "open source" (not a thing; they mean open-weights, but actually really they mean "Chinese") models has kicked into high gear. https://www.cybersecuritydive.com/news/openai-hugging-face-hack-ai-models-black-hat/827167/
OpenAI warns autonomous hacks are ‘watershed moment for computer security’
Cybersecurity Dive

OpenAI warns autonomous hacks are ‘watershed moment for computer security’

Company employees said their industry should rethink how it balances capabilities and safeguards.

0
0
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
Replying to
@galaxis@mastodon.infra.de Thanks! Not sure how that happened but the CVE number was incorrect. It has been fixed. https://discourse.ifin.network/t/cve-2026-11405-multiple-tenda-routers-have-an-admin-backdoor/646
CVE-2026-11405: Multiple Tenda Routers Have an Admin Backdoor
IFIN

CVE-2026-11405: Multiple Tenda Routers Have an Admin Backdoor

Last Updated: 2026-07-08T15:51:19Z (UTC) CVSSv3: None yet Multiple versions of Tenda firmware have a backdoor in remote administration login, allowing anyone to access configuration of the device. Affected Versions: US_FH1201V1.0BR_V1.2.0.14(408)_EN_TD US_W15EV1.0br_V15.11.0.5(1068_1567_841)_EN_TDE US_AC10V1.0re_V15.03.06.46_multi_TDE01 US_AC5V1.0RTL_V15.03.06.48_multi_TDE01 US_AC6V2.0RTL_V15.03.06.51_multi_T No patch is currently available. We recommend burning your Tenda devices in

0
0
0
0
Open post
IFIN - The Independent Federated Intelligence Network @ifin@infosec.exchange
· 3mo ago
Replying to
@Sempf@infosec.exchange @sternecker@infosec.exchange We have a thread ready and waiting! https://discourse.ifin.network/t/bad-epoll-lpe-linux-kernel-cve-2026-46242/641
Bad Epoll LPE - Linux Kernel - CVE-2026-46242
IFIN

Bad Epoll LPE - Linux Kernel - CVE-2026-46242

A new LPE on the Linux Kernel has been released, affecting versions 6.4+ of the kernel. Some distros may be vulnerable if they backport though. There is no mitigation, only patching. There is an existing PoC but for google’s KernelCTF. Original writeup: security-research/pocs/linux/kernelctf/CVE-2026-46242_lts_cos/docs/exploit.md at submit-cve-2026-46242 · J-jaeyoung/security-research · GitHub More Information: GitHub - J-jaeyoung/bad-epoll · GitHub and https://compsec.snu.ac.kr/blog/badepoll

0
2
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 06:59:47 UTC