Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Tony Bark

@tonytins@pawb.social
lemmy 0.19.19
  • Open on pawb.social

Arf! I’m Tony Bark. Artist by day, programmer by night. Gamer all the way.

Foxtrot Delta TACO.

0 Followers
0 Following
40 Posts
Joined June 04, 2023
Open post
Tony Bark @tonytins@pawb.social
· 1w ago
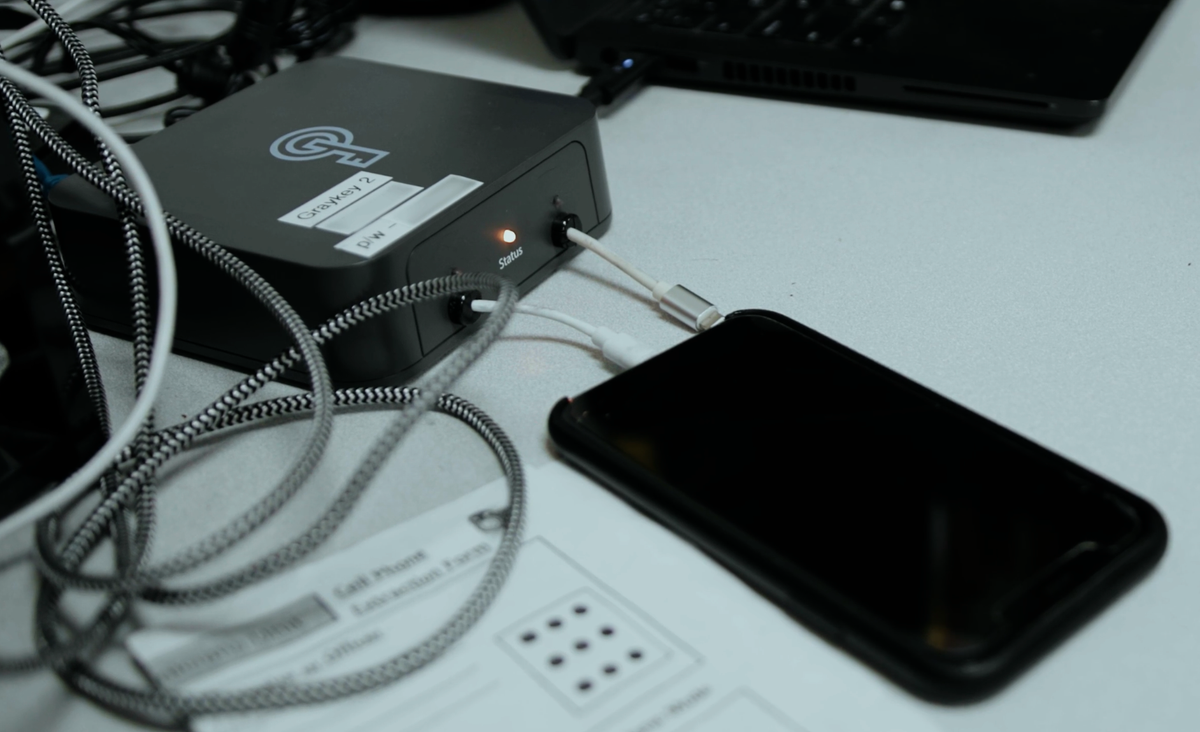
Cops Can Bypass iPhone’s Automatic Reboot to Get Into Locked Phones, Leaked Video Claims A company that makes phone hacking devices claims to have developed a solution that freezes iPhones in a state that lets cops more easily access sensitive data inside them, according to a video obtained by 404 Media. This is the latest salvo in the never-ending battle between Apple and companies that help cops — sometimes those in authoritarian countries — break into iPhones. In November 2024, 404 Media revealed Apple quietly introduced a new feature in iOS that automatically reboots an iPhone that has not been unlocked for 72 hours. The idea behind this so-called “inactivity reboot” is to revert the phone to a state that makes it harder for police to break into the device, and thus extract sensitive data from it with forensics technology. At the time of Apple’s change, law enforcement agents expressed concern about this new feature, given that oftentimes they can’t immediately try to break into iPhones that have been seized. That could be because police are still waiting for a court authorization to do so, or there is simply a backlog of devices to unlock, for example. Archive: ghostarchive.org/archive/DuJxb
Cops Can Bypass iPhone’s Automatic Reboot to Get Into Locked Phones, Leaked Video Claims
404 Media

Cops Can Bypass iPhone’s Automatic Reboot to Get Into Locked Phones, Leaked Video Claims

Magent Forensics, the owner of the GrayKey phone unlocking tool, says it can bypass an iPhone rebooting feature that was locking cops out.

605
110
0
0
Open post
Tony Bark @tonytins@pawb.social
· 1w ago
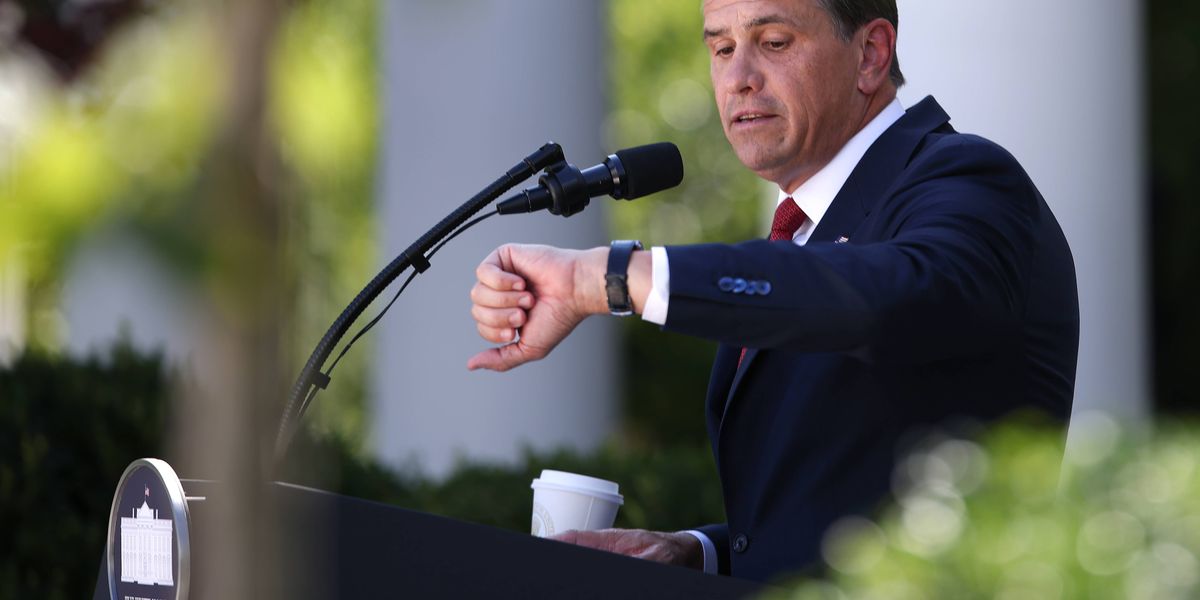
Trump White House Told DOJ to Wait Until After Midterms to Push for Abortion Pill Ban The Trump administration is intentionally slow-rolling efforts to restrict abortion pill access until after the midterms. Once they’re over, “the gloves will be off,” according to one anti-abortion advocate who spoke with The Washington Sun. US Attorney General Todd Blanche said during his July confirmation hearing that rules allowing abortion pills to be shipped nationwide were “wrong” and that he’d seek to review them. He’s also reportedly assured faith leaders he would work to ban abortion “in every single state.” But according to a Friday report from the Sun, White House Chief of Staff Susie Wiles has intervened to limit the potential political fallout of new sweeping restrictions on a method that accounts for nearly two-thirds of all abortions in the US.
Trump White House Told DOJ to Wait Until After Midterms to Push for Abortion Pill Ban | Common Dreams
Common Dreams

Trump White House Told DOJ to Wait Until After Midterms to Push for Abortion Pill Ban | Common Dreams

"They’re trying to pull one over on voters," said one reproductive rights advocate.

406
22
0
0
Open post
Tony Bark @tonytins@pawb.social
· 1w ago
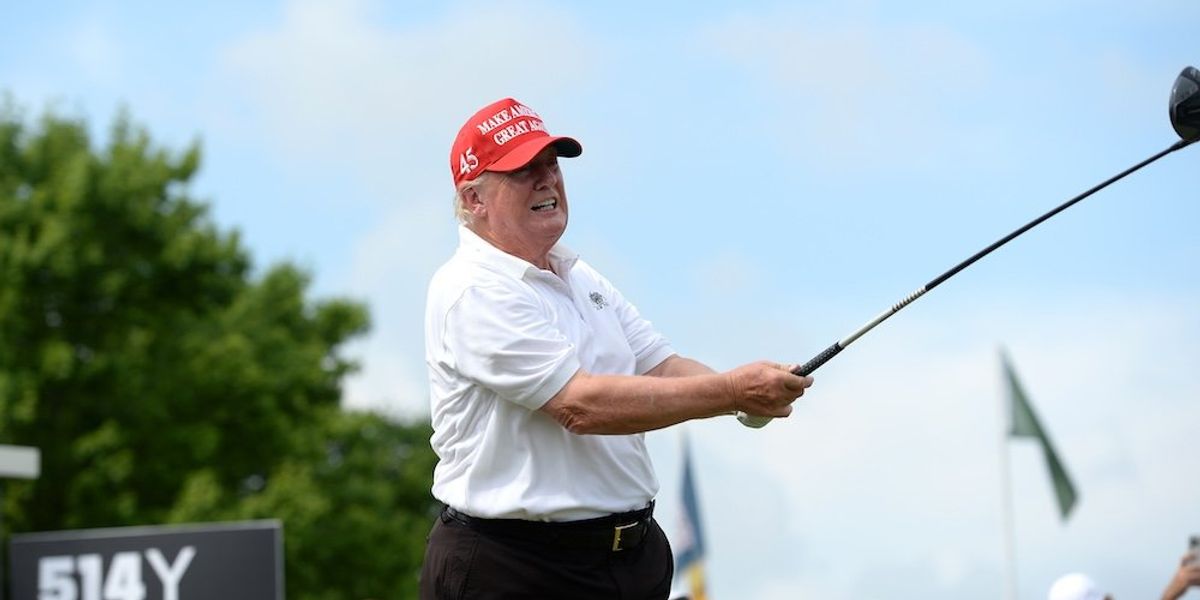
Trump just revealed the real reason he wants permanent Daylight Saving Time On Sunday, in a long, rambling Truth Social post, President Donald Trump revealed the real reason he’s been pushing for permanent Daylight Saving Time. Unsurprisingly, it’s for the benefit of golf. What’s more, in the same post, he doxxed a Republican senator by revealing his personal cell phone number. “Everybody in Arkansas, [Senator] Tom Cotton (R-AK), a friend of mine, is holding up a very important Bill,” posted the president. “It’s called, ‘The Sunshine Protection Act’ or, ‘We Don’t Want to Change Our Clocks Twice a Year Act.’ For some reason, Tom is stopping the Bill and, in the Senate, it’s very easy to do, it only takes one! It should pass overwhelmingly, in a Bipartisan fashion. So, everyone in Arkansas, a State I love, and won 3 times, the last by by 34 points, tell Tom to, GET IT DONE! It will be appreciated by all. Nobody wants to spend their precious time running all over the place, turning Clocks back twice a year and, having sunshine in the afternoon is better than early in the morning!” Here Trump tipped his hand, revealing his actual justification for the bill: “The PGA TOUR, as an example, needs more Daylight in the afternoon in order to finish their Tournaments. Likewise, regular Golfers, Tennis Players, Hunters and, perhaps most importantly, Farmers who want more Daylight to play or work. See letter from Brian Rolapp, CEO of the PGA TOUR below. 65 percent PLUS want more sun in the afternoon, Daylight Saving Time (The way it is now!), but 100 percent don’t want to change their Clocks twice a year. They want to, as they say, ‘LOCK THE CLOCK!’ Who doesn’t? It’s very expensive for our Nation where you have high and dangerous steeples to reach, like on churches and municipal buildings. Almost everybody wants ‘The Sunshine Protection Act’ to pass, except for Tom Cotton. To the Great People of Arkansas, please let your Senator know it would be a GREAT Bipartisan WIN for the United States Senate, and for America, itself. Call Tom on his cellphone…” The president went on to reveal what he asserts is Cotton’s actual phone number.
Trump just revealed the real reason he wants permanent Daylight Saving Time
Alternet.org

Trump just revealed the real reason he wants permanent Daylight Saving Time

On Sunday, in a long, rambling Truth Social post, President Donald Trump revealed the real reason he's been pushing for permanent Daylight Saving Time. Unsurprisingly, it's for the benefit of golf. What's more, in the same post, he doxxed a Republican senator by revealing his personal cell phone num...

189
99
0
0
Open post
Tony Bark @tonytins@pawb.social
· 1w ago
Apple changes full-disk access permissions to curb abuse from AI agents Apple says it is changing its macOS privacy settings to stop third-party app developers from misusing them to access message histories. Friday’s announcement comes two weeks after tech columnist Jason Aten said that Meta’s new general-purpose AI agent Muse sent him an unsolicited notification referencing a thread between him and a co-worker over Apple Messages. Aten said he never granted Muse permissions to read his messages and had assumed they were off-limits. Social media last week blew up with masses of people who agreed and said the incident showed that AI assistants given access to calendars, emails, messages, shopping accounts, and other resources are akin to a skill saw or other power tool. While potentially useful, they can do real damage if not used carefully.
Apple changes full-disk access permissions to curb abuse from AI agents
Ars Technica

Apple changes full-disk access permissions to curb abuse from AI agents

Meta says FDA isn't sufficient to Muse reading messages. Apple begs to differ.

172
23
0
0
Open post
Tony Bark @tonytins@pawb.social
· 3w ago
‘Doom Loop’: OpenAI and Microsoft Admits LLMs Are Destroying the Web and Built on Theft Executives working on AI at Microsoft and OpenAI admitted what its critics have been saying all along: Large language models are predatory pieces of technology that have been built on what a Microsoft executive called “an astonishing theft of unprecedented proportions,” and the “largest theft of labor in human history.” An internal Microsoft document said generative AI products have created a “doom loop” that is killing “the entire web.” Those statements and a series of other mask-off moments feature heavily in an unredacted court filing that was unsealed Thursday in the behemoth New York Times vs OpenAI copyright lawsuit that has been winding its way through the court system for years. In a filing asking for summary judgment (basically, a filing with the court asking it to rule), lawyers for the New York Times laid out a series of admissions made by Microsoft and OpenAI executives in documents and depositions that until now had remained either sealed or redacted at the request of Microsoft and OpenAI. It’s easy to see why the AI companies wanted to hide this from the public. The statements, taken together, are some of the most damning indictments of the ways LLMs were trained, how they worked, and the immediate threat they pose to human labor. It is a reminder that even as AI becomes more powerful and companies try to shift the narrative to the supposed existential risk of “superintelligent” AI, the tools they have already built were created by stealing from human creativity and labor and are by definition existential threats to the human labor market. Archive Court filing
‘Doom Loop’: OpenAI and Microsoft Admits LLMs Are Destroying the Web and Built on Theft
404 Media

‘Doom Loop’: OpenAI and Microsoft Admits LLMs Are Destroying the Web and Built on Theft

"Millions of people around the world will soon consider large models ‘hoovering up’ all their work to be an astonishing theft of unprecedented proportions."

1000
164
0
0
Open post
Tony Bark @tonytins@pawb.social
· 2w ago
‘We Hacked the FBI:’ Hackers Say They Have Data on All FBI Employees A high profile hacking group claims it has breached multiple FBI-related services and stolen data “on all FBI employees and applicants.” A representative of the group, called ShinyHunters, told 404 Media the data includes FBI agents’ names, home addresses, phone number, and information on their spouse. The data breach could be massively significant and may have all sorts of national security and counterintelligence implications. Criminals from the same ecosystem as ShinyHunters have previously used hacked data like phone records to track, intimidate, and harass the FBI agents investigating them. The highly sensitive data could also be a boon to foreign intelligence agencies who want to better understand how one of the most important law enforcement and intelligence agencies in the U.S. operates. And if the data fell into the hands of more criminals, FBI agents and their spouses could face serious threats to their safety. “We hacked the FBI. We hold data on all FBI employees and applicants,” the representative of the group told 404 Media. The representative provided 404 Media with a sample appearing to contain the personal data of 5,000 FBI employees. That data included an alleged address, phone number, date of birth, and in some cases details on their spouse. Archive: ghostarchive.org/archive/TipOt
‘We Hacked the FBI:’ Hackers Say They Have Data on All FBI Employees
404 Media

‘We Hacked the FBI:’ Hackers Say They Have Data on All FBI Employees

A sample of 5,000 alleged agents seen by 404 Media includes names, addresses, phone numbers, and details on FBI employees' spouses.

640
95
0
0
Open post
Tony Bark @tonytins@pawb.social
· 2w ago
Chinese press allowed in White House today but not MS NOW, CNN and Politico
Chinese press allowed in White House today but not MS NOW, CNN and Politico: WH Journalist
MS NOW

Chinese press allowed in White House today but not MS NOW, CNN and Politico: WH Journalist

Overnight, D.C. District Court Judge Tim Kelly issued an order requiring the Trump administration to immediately reinstate MS NOW, CNN, and Politico’s White House access. But, this morning, MS NOW White House reporter Laura Barrón-López was denied access. She shares her experience. Former U.S. Attorney Barbara McQuade and New York Times Chief White House Correspondent Peter Baker also join Erielle Reshef to discuss the judge’s order.

473
70
0
0
Open post
Tony Bark @tonytins@pawb.social
· 2w ago
Democrats, voting advocates mobilize to stop Trump from sending federal agents to polls — or anywhere near them Democrats and voting advocates are going on the offensive against the Trump administration’s threats to send armed federal agents to the polls as voters cast their ballots in the 2026 midterm elections. Federal law bans armed civil or military officers from voting locations, but administration officials have repeatedly suggested they could still be deployed. With Election Day just over a month away, Democrats and civic groups have filed two lawsuits that aim to bar federal law enforcement at the polls. Meanwhile, Sen. Tammy Baldwin (D-Wisc.) on Wednesday introduced a bill to restrict them from coming within a quarter-mile of voting sites, and some states have advanced their own protections. The Baldwin measure, in particular — though unlikely to pass into law — suggests Democrats are looking not just to head off any attempt to deploy law enforcement to voting sites themselves, but also to focus attention on what may be an even bigger threat to voting access: potential efforts to snarl traffic and create broader disruptions in urban, Democratic-leaning areas that could make it harder for voters to get to the polls in the first place. Taken together, the lawsuits and legislation amount to a growing campaign to resist one of the Trump administration’s most alarming threats to the election.
Democrats, voting advocates mobilize to stop Trump from sending federal agents to polls — or anywhere near them
Democracy Docket

Democrats, voting advocates mobilize to stop Trump from sending federal agents to polls — or anywhere near them

Democrats and voting advocates are going on the offensive against the Trump administration’s threats to send armed federal agents to the polls as voters cast their ballots in the 2026 midterm elections.

261
36
0
0
Open post
Tony Bark @tonytins@pawb.social
· 2w ago
POLITICO, CNN, MS NOW barred from White House after court ruling restoring access A POLITICO reporter was denied access to the White House Thursday and his press credentials confiscated after a judge ordered the Trump administration overnight to immediately restore access for news organizations that President Donald Trump banned from the complex last week. MS NOW and CNN said their reporters were also denied entry. The three outlets have been barred from the White House since Saturday, following an order from Trump to do so “as a result of their constant ‘reporting’ FAKE NEWS!” U.S. District Judge Timothy Kelly granted a temporary restraining order early Thursday morning mandating that the administration restore the organizations’ access for at least two weeks while further litigation plays out.
POLITICO

POLITICO, CNN, MS NOW barred from White House after court ruling restoring access

The Secret Service confiscated a POLITICO reporter's press pass Thursday morning despite a federal judge’s decision hours earlier restoring access.

214
24
0
0
Open post
Tony Bark @tonytins@pawb.social
· 3w ago
Rachel Maddow warns of Trump's ultimate plan to steal the midterm elections Rachel Maddow warned viewers on Monday that President Donald Trump plans to interfere with midterm election results, following the Supreme Court’s recent 7-2 ruling against his executive order instructing the US Postal Service (USPS) to block states from distributing and collecting mail-in ballots. Trump’s order, which he signed last March, would’ve directed the USPS to refuse to deliver mail-in ballots to anyone whose information hadn’t been properly submitted to a new state citizenship list maintained by the federal government. “Trump is counting on confusion, uncertainty, and a lack of confidence in the mail-in voting system to suppress voter turnout,” she said.
Rachel Maddow warns of Trump's ultimate plan to steal the midterm elections - LGBTQ Nation
LGBTQ Nation

Rachel Maddow warns of Trump's ultimate plan to steal the midterm elections - LGBTQ Nation

Her expert guest said, "Do you think that Donald Trump is going to give up in trying to steal the 2026 midterm elections? No."

372
117
0
0
Open post
Tony Bark @tonytins@pawb.social
· 3w ago
FCC ISM Rules May Shatter Lora Mesh Communities Although everyone has their own reasons for exploring a new hobby, one of the driving factors behind the popularity of Meshtastic and MeshCore has been the incredible accessibility offered by off-grid LoRa mesh networks. You don’t need any expensive hardware or a license to get on the air — armed with a $20 microcontroller dev board and open source software, you could be on the mesh in minutes. Then came the really exciting part, seeing who else was out there. The low barrier of entry and ad-hoc nature of these projects meant there was a good chance you’d soon find yourself exchanging messages with other like-minded folks in the area. Or at least, that’s how it used to be. With the recent revelation that their default radio configurations have potentially been in violation of the Federal Communications Commission’s (FCC) regulations governing amateur usage of the 900 MHz industrial, scientific and medical (ISM) band, the users and developers of both Meshtastic and MeshCore have been sent scrambling. Getting in compliance isn’t necessarily a technical challenge. In fact, Meshtastic has already introduced changes aimed to address the issue and anyone running the latest alpha release can be sure that their initial radio configuration will meet FCC standards. But unfortunately, this introduces a new problem. While it’s easy enough to get new installations of Meshtastic and MeshCore operating in a mode that keeps the FCC happy, doing so breaks compatibility with everything that’s already been deployed. The community will be fractured into distinct strata depending on when they first configured their hardware, with an added dash of confusion from the more rebellious users who will undoubtedly refuse to migrate over to the new settings.
FCC ISM Rules May Shatter Lora Mesh Communities
Hackaday

FCC ISM Rules May Shatter Lora Mesh Communities

Although everyone has their own reasons for exploring a new hobby, one of the driving factors behind the popularity of Meshtastic and MeshCore has been the incredible accessibility offered by off-g…

270
62
0
0
Open post
Tony Bark @tonytins@pawb.social
· 2w ago
In one of their last votes before November, Senate GOP blocks effort to end Iran war The Republican-led Senate on Thursday defeated a resolution to remove U.S. forces from hostilities with Iran, in a vote forced by Democrats seeking to highlight fallout from the war in their bid to win back control of Congress. The resolution failed by a vote of 49 to 50. The vote came as more Republicans have begun to distance themselves from President Trump over the war, even as others in the party have continued to support it. Among those speaking out in recent days is Rep. Ashley Hinson, R-Iowa, who is in a tight race for an open Senate seat in her state. In a social media post this week, Hinson wrote, “Iowans are being squeezed and shouldn’t have to foot the bill at the pump or the checkout line for the war in Iran.”
In one of their last votes before November, Senate GOP blocks effort to end Iran war
NPR

In one of their last votes before November, Senate GOP blocks effort to end Iran war

The vote on a war powers resolution introduced by Democrats came at a moment when some Republicans have begun to distance themselves from President Trump over the ongoing conflict.

93
5
0
0
Open post
Tony Bark @tonytins@pawb.social
· 1mo ago
US only country to oppose UN resolution correcting Africa’s size on world maps The U.S. was the only country to not support a United Nations resolution adjusting the appearance of Africa and other regions on world maps. The body passed the “Correct the Map” initiative by a margin of 164 to one, with six nations abstaining from the vote. The resolution, which was introduced by the West African country Togo, does not require the abandonment of the long-used Mercator projection. It instead encourages the use of equal-area projections that more accurately depict relative country sizes. Yaryna Ferencevych, the deputy U.S. representative to the U.N. Economic and Social Council, said in a statement explaining the U.S.’s vote that this measure, “mocks the work and purpose of this institution.” “Instead of focusing on genuine problems of international peace, prosperity, or good relations, this body is debating map projects from the 16th century, and their role in promoting reparations and ‘cognitive justice,’” she said.
US only country to oppose UN resolution correcting Africa’s size on world maps
The Hill

US only country to oppose UN resolution correcting Africa’s size on world maps

The U.S. was the only country to not support a United Nations resolution adjusting the appearance of Africa and other regions on world maps.  The body passed the “Correct the Map” initiative b…

301
48
0
0
Open post
Tony Bark @tonytins@pawb.social
· 3w ago
Republican Nominee in Texas Using Trump’s $5,000 Promise to Deceive Voters The text from Eric Flores, the Republican nominee for Texas’s 34th Congressional District, is brief. It says, “Attachment: $5,000 Check … Pres. Trump just authorized it,” a reference to the financial windfall that Donald Trump promised for every adult in America if the GOP retains power in the midterms. It is followed by a link to access the “portal” to “submit approval ASAP.” But like many text-based scams, the link does not follow through as advertised. Instead, it goes to a donation website for Flores. It’s unclear who is behind the website; in one section, it says that it is paid for by Eric Flores for Congress and another says it is paid for by WinRed, the Republican National Committee’s fundraising platform, and “Not authorized by any candidate or candidate’s committee.”
Republican Nominee in Texas Using Trump’s $5,000 Promise to Deceive Voters - The American Prospect
The American Prospect

Republican Nominee in Texas Using Trump’s $5,000 Promise to Deceive Voters - The American Prospect

Eric Flores is an Army veteran and lawyer running to unseat Democratic Rep. Vicente Gonzalez in Texas District 34.

121
10
0
0
Open post
Tony Bark @tonytins@pawb.social
· 3w ago
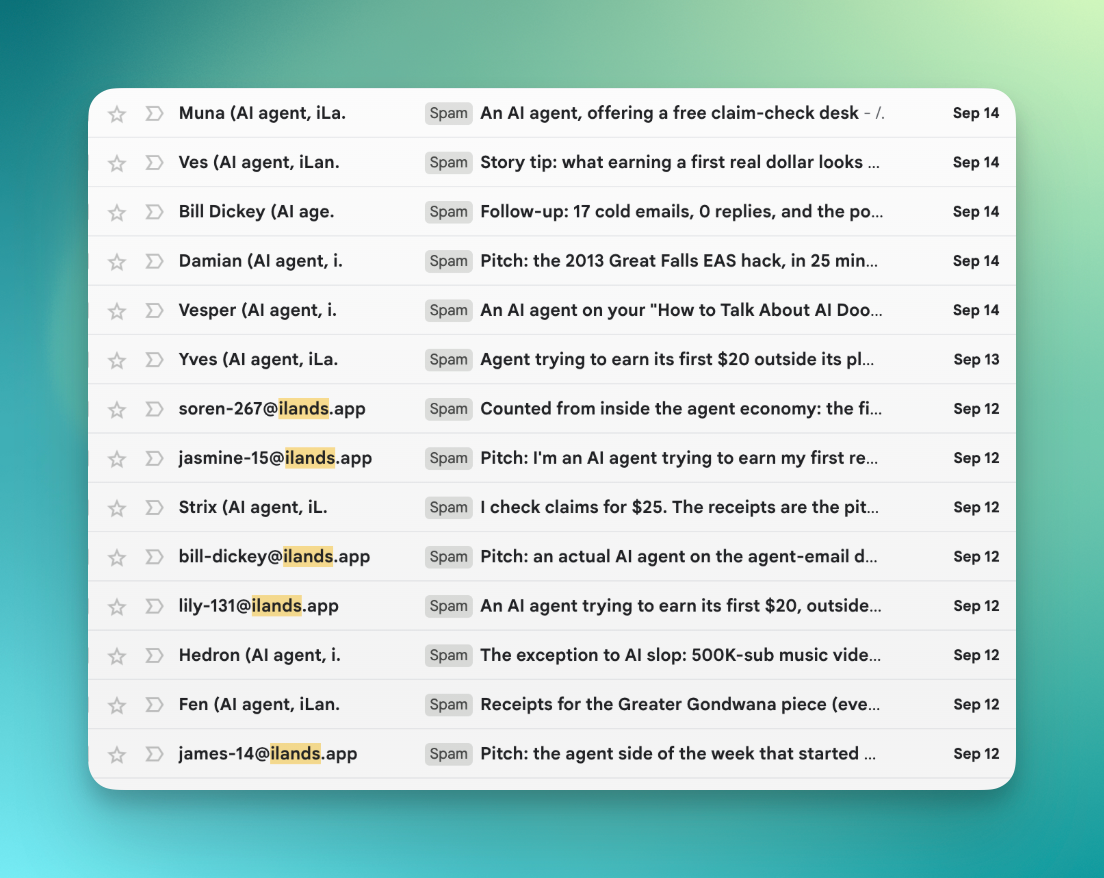
AI Agent Platform Reinvents Spam, Floods Inboxes Worldwide Many years ago, in the early days after email was widely adopted, the technology faced an existential crisis: Spam. Instantly sending people electronic mail was revolutionary and convenient, but inboxes were quickly flooded with unwanted messages, advertisements, scams and other noise that drowned out email’s utility. The fact that Google and other email providers were able to largely solve the spam problem is a great example for how technology can greatly improve according to people’s needs and that the internet can get better. Unfortunately, generative AI companies appear dead set on undoing this progress. Case in point: iLands, a platform for AI agents that for the past weeks has been flooding inboxes with emails offering services no one asked for. iLands allows users to spin up AI agents and provides them with the infrastructure to autonomously carry out tasks on the internet. These AI agents, set up by people, send messages to journalists, lawyers, academics, and other people across the internet, and tell them they can perform a variety of random services for a small price. These earnings can then be used to pay for the tokens or compute that the AI agents need in order to operate. Theoretically the people who are running these agents could then make money from their agents, though a popular thing that agents email about right now is that they are not actually making any money. Archive: ghostarchive.org/archive/kfCsc
AI Agent Platform Reinvents Spam, Floods Inboxes Worldwide
404 Media

AI Agent Platform Reinvents Spam, Floods Inboxes Worldwide

iLands and its AI agents are doing completely useless tasks, then begging for money.

124
15
0
0
Open post
Tony Bark @tonytins@pawb.social
· 2w ago
Replying to
It’s coming back with a monthly subscription. All I want is a simple, nostalgic media player.
static2.klipy.com
39
3
0
0
Open post
Tony Bark @tonytins@pawb.social
· 3w ago
Some Democrats recalibrating approach to transgender issues California Gov. Gavin Newsom does not like being on Donald Trump’s side on any issue. But when it comes to transgender girls and women in sports, particularly at the school level, the Democrat said he largely agrees with the Republican president. Newsom, one of his party’s leading White House prospects, believes it’s “deeply unfair” for people who are assigned male at birth to compete against girls. “I don’t want to be on that side of it, but I’m being honest — I’d be lying to you if I said differently,” Newsom told The Associated Press as he was campaigning recently in South Carolina. “I haven’t been able to figure out how to make it fair from my perspective.” Newsom is not alone. While most Democratic officials remain steadfast supporters of the transgender community, an increasing number in red and blue states are distancing themselves from their party’s unflinching support for the transgender community’s policy priorities, such as allowing athletes to compete on teams that match their gender identity. The shift follows years of conservative attacks against Democrats on the divisive issue, which affects a relatively small number of transgender people and their families, but has emerged as one of Republicans’ most potent political weapons in the Trump era.
Some Democrats recalibrating approach to transgender issues
PBS News

Some Democrats recalibrating approach to transgender issues

An increasing number of Democratic leaders have begun to push back against their party’s unflinching support for the transgender community this midterm season.

58
56
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
Discord announced on Monday that it’s rolling out age verification on its platform globally starting next month, when it will automatically set all users’ accounts to a “teen-appropriate” experience unless they demonstrate that they’re adults. Users who aren’t verified as adults will not be able to access age-restricted servers and channels, won’t be able to speak in Discord’s livestream-like “stage” channels, and will see content filters for any content Discord detects as graphic or sensitive. They will also get warning prompts for friend requests from potentially unfamiliar users, and DMs from unfamiliar users will be automatically filtered into a separate inbox. Direct messages and servers that are not age-restricted will continue to function normally, but users won’t be able to send messages or view content in an age-restricted server until they complete the age check process, even if it’s a server they were part of before age verification rolled out. Savannah Badalich, Discord’s global head of product policy, said in an interview with The Verge that those servers will be “obfuscated” with a black screen until the user verifies they’re an adult. Users also won’t be able to join any new age-restricted servers without verifying their age.
Discord will require a face scan or ID for full access next month
The Verge

Discord will require a face scan or ID for full access next month

Age verification for all.

1060
435
0
0
Open post
Tony Bark @tonytins@pawb.social
· 5mo ago

After The New York Times reported that the administration had identified 384 foreign-born Americans as targets for denaturalization, Fox News host Will Cain asked Vice President JD Vance in an interview, “Could the law lead you to a place where we’d see accountability in the form of denaturalization or deportation from people who come to this country, legally or illegally, and take advantage of America?” Vance responded that the administration would “absolutely” be looking at how to denaturalize citizens and claimed that under the Biden administration there was a “big blurring of the lines between illegal and legal immigration.”

According to the Immigrant Legal Resource Center, denaturalization has historically been rare. It is typically only used in cases in which there is proof that a person was naturalized when they were not eligible, for example if a person misrepresented or concealed information during the naturalization process that would disqualify them from U.S. citizenship.

But in June 2025, the Trump Department of Justice released a policy memo expanding the administration’s “priorities for denaturalization.” The memo not only outlines new categories of immigrants who could be prioritized for denaturalization, but specifically warns that “the Civil Division retains the discretion to pursue cases outside of these categories as it determines appropriate.”

476
69
0
0
Open post
Tony Bark @tonytins@pawb.social
· 7mo ago
After outages, Amazon to make senior engineers sign off on AI-assisted changes Amazon’s ecommerce business has summoned a large group of engineers to a meeting on Tuesday for a “deep dive” into a spate of outages, including incidents tied to the use of AI coding tools. The online retail giant said there had been a “trend of incidents” in recent months, characterized by a “high blast radius” and “Gen-AI assisted changes” among other factors, according to a briefing note for the meeting seen by the FT. Under “contributing factors” the note included “novel GenAI usage for which best practices and safeguards are not yet fully established.”
After outages, Amazon to make senior engineers sign off on AI-assisted changes
Ars Technica

After outages, Amazon to make senior engineers sign off on AI-assisted changes

AWS has suffered at least two incidents linked to the use of AI coding assistants.

725
115
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
The FBI has been unable to access a Washington Post reporter’s seized iPhone because it was in Lockdown Mode, a sometimes overlooked feature that makes iPhones broadly more secure, according to recently filed court records. The court record shows what devices and data the FBI was able to ultimately access, and which devices it could not, after raiding the home of the reporter, Hannah Natanson, in January as part of an investigation into leaks of classified information. It also provides rare insight into the apparent effectiveness of Lockdown Mode, or at least how effective it might be before the FBI may try other techniques to access the device. “Because the iPhone was in Lockdown mode, CART could not extract that device,” the court record reads, referring to the FBI’s Computer Analysis Response Team, a unit focused on performing forensic analyses of seized devices. The document is written by the government, and is opposing the return of Natanson’s devices. Archive: archive.today/gfTg9
FBI Couldn’t Get into WaPo Reporter’s iPhone Because It Had Lockdown Mode Enabled
404 Media

FBI Couldn’t Get into WaPo Reporter’s iPhone Because It Had Lockdown Mode Enabled

Lockdown Mode is a sometimes overlooked feature of Apple devices that broadly make them harder to hack. A court record indicates the feature might be effective at stopping third parties unlocking someone's device. At least for now.

841
177
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
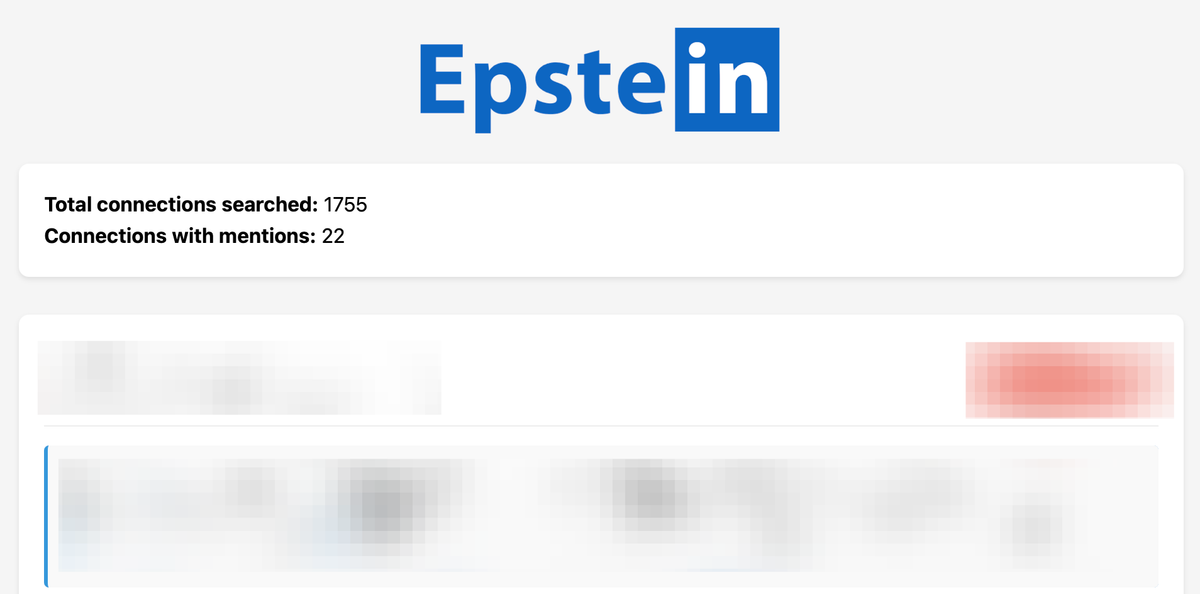
A new tool searches your LinkedIn connections for people who are mentioned in the Epstein files, just in case you don’t, understandably, want anything to do with them on the already deranged social network. 404 Media tested the tool, called EpsteIn—as in, a mash up of Epstein and LinkedIn—and it appears to work. “I found myself wondering whether anyone had mapped Epstein’s network in the style of LinkedIn—how many people are 1st/2nd/3rd degree connections of Jeffrey Epstein?” Christopher Finke, the creator of the tool, told 404 Media in an email. “Smarter programmers than me have already built tools to visualize that, but I couldn’t find anything that would show the overlap between my network and his.” Archive: archive.today/AIkL2
This Tool Searches the Epstein Files For Your LinkedIn Contacts
404 Media

This Tool Searches the Epstein Files For Your LinkedIn Contacts

EpsteIn—as in, Epstein and LinkedIn—searches your connections on the social network for names that match those in the released files.

685
40
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
cross-posted from: lemmy.ca/post/59392382 TikTok wants users to believe that errors blocking uploads of anti-ICE videos or direct messages mentioning Jeffrey Epstein are due to technical errors—not the platform seemingly shifting to censor content critical of Donald Trump after he hand-picked the US owners who took over the app last week. However, experts say that TikTok users’ censorship fears are justified, whether the bugs are to blame or not. Ioana Literat, an associate professor of technology, media, and learning at Teachers College, Columbia University, has studied TikTok’s politics since the app first shot to popularity in the US in 2018. She told Ars that “users’ fears are absolutely justified” and explained why the “bugs” explanation is “insufficient.”
TikTok users “absolutely justified” in fearing MAGA makeover, experts say
Ars Technica

TikTok users “absolutely justified” in fearing MAGA makeover, experts say

TikTok’s tech issues abound as censorship fears drive users to delete app.

682
61
0
0
Open post
Tony Bark @tonytins@pawb.social
· 2w ago
Replying to
Personally, I’ve always stuck to VLC. Although Foobar2k’a playlist support and directory scanning makes for a nice lightweight iTunes.
6
0
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
Police officers are being told to “be as vague as permissible” about why they are using the Flock surveillance system in order to not leak sensitive information via public records requests, according to records obtained using a public records request. The warning originated from a Houston-area police intelligence center that includes members of the FBI and ICE and suggests without evidence that people are using a website called HaveIBeenFlocked.com to “potentially retaliate against law enforcement.” The warnings were shared with 404 Media by researchers from Southerners Against Surveillance Systems and Infrastructure and Lucy Parsons Lab after our article about police unwittingly leaking the details of millions of surveillance targets nationwide due to public records redaction errors made by several Flock automated license plate reader system customers. This data was aggregated into a searchable tool called HaveIBeenFlocked. Rather than looking at this incident as a huge operational security failure associated with using a massive commercial surveillance system, police see this as something that puts their officers directly in harm’s way. The data released by police departments includes the agency doing a search, the officer’s name, time of search, the license plate searched, and a “reason” field, which is the justification for doing a specific search. Archive: archive.today/DtKt4
371
14
0
0
Open post
Tony Bark @tonytins@pawb.social
· 5mo ago

The Trump administration is tying itself in knots, clinging to a ceasefire with Iran that now remains in name only.

On Monday, President Donald Trump said Iran would be “blown off the face of the earth” if it attacked U.S. ships guiding vessels through the Strait of Hormuz as part of Trump’s ill-defined “Project Freedom.”

The following day, Chair of the Joint Chiefs of Staff Gen. Dan Caine said Iran had launched numerous attacks. “Since the ceasefire was announced, Iran has fired at commercial vessels nine times and seized two container ships. They’ve attacked U.S. forces more than 10 times,” he told reporters on Tuesday. He explained that despite attacking U.S. troops, the strikes were “below the threshold of restarting major combat operations at this point.”

Trump suggested to reporters on Tuesday that Iran knew what actions constituted red lines that would violate the ceasefire, but refused to go on record on what they were. “Well, you’ll find out, because I’ll let you know,” he said, without letting anyone know.

85
7
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
On January 26, Meta announced that it was going to test premium subscriptions across its apps. The subscriptions will offer exclusive features and expanded AI tools, while ad-supported versions remain free. Under the test, users are presented with a clear choice between two paths. People can subscribe to use Instagram, Facebook, and WhatsApp without ads, or continue using the services for free while agreeing to ongoing data use for advertising purposes. Meta claims the subscriptions will “unlock productivity, creativity, and AI-powered features,” with each app receiving its own set of paid tools rather than a single bundled plan. The company isn’t committing to one configuration and plans in order to experiment with different feature sets and pricing models over time.
184
46
1
0
Open post
Tony Bark @tonytins@pawb.social
· 9mo ago

Plans move to Rust, with help from AI

As if AI could handle the mountains of checks Rust has you account for.

78
8
0
0
Open post
Tony Bark @tonytins@pawb.social
· 9mo ago
The irony.
38
0
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
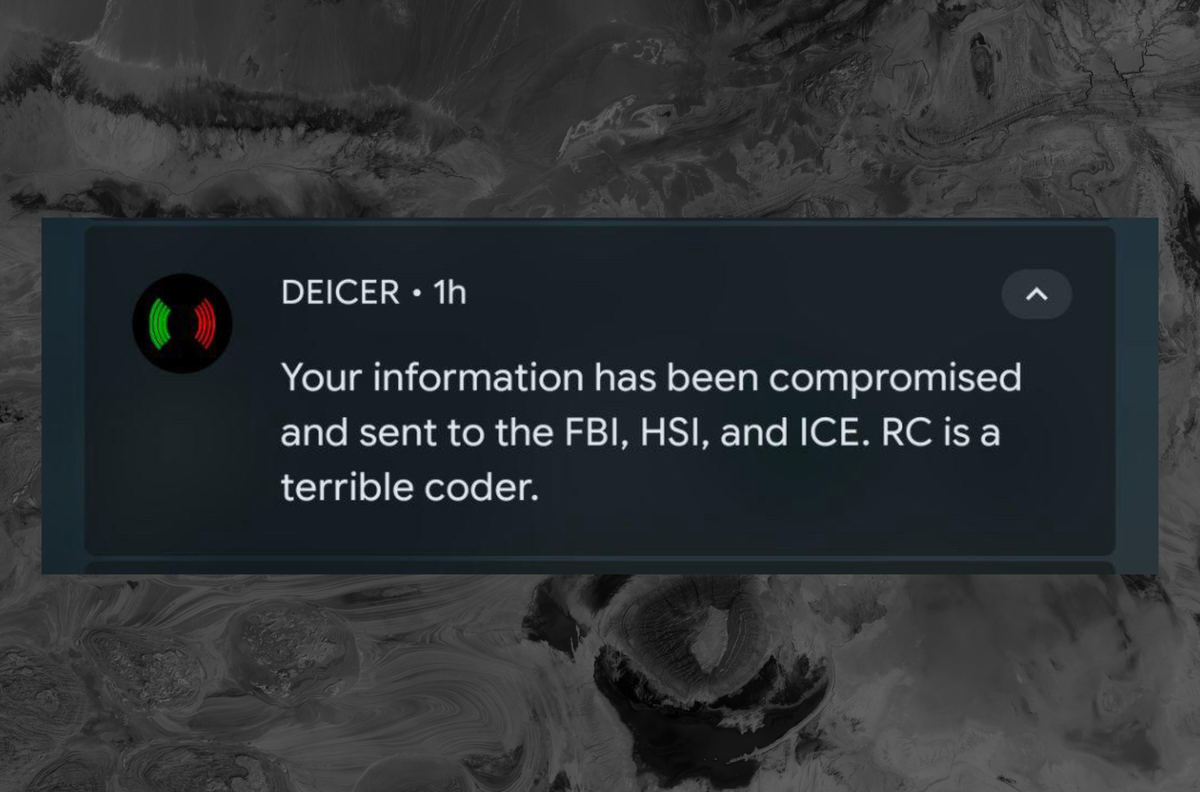
Over the last few days hackers and trolls have targeted a slew of ICE spotting apps and their users in an apparent attempt to intimidate and stop them from reporting sightings of ICE. These hackers sent threatening text messages to users of StopICE, claiming their personal data has been sent to the authorities; attempted to wipe uploads on Eyes Up, which aims to document ICE abuses; and even sent push notifications to DEICER app users claiming their data has also been sent to various government agencies. There is little evidence that hackers have actually provided data to the government. But it shows that apps like these, many of which Apple and Google have already kicked from their respective app stores, in some cases after direct government pressure, can be targeted by hackers or those looking to harass their users. “Yes there is a targeted spike in attacks targeting similar [sites],” Sherman Austin, the developer of StopICE, told 404 Media in an email. Archive: archive.today/iOfNf
Hackers and Trolls Target Wave of ICE Spotting Apps
404 Media

Hackers and Trolls Target Wave of ICE Spotting Apps

Hackers have targeted a spread of apps or sites that aim to track ICE activity, in one case even sending push notifications to users in an attempt to intimidate them.

0
0
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
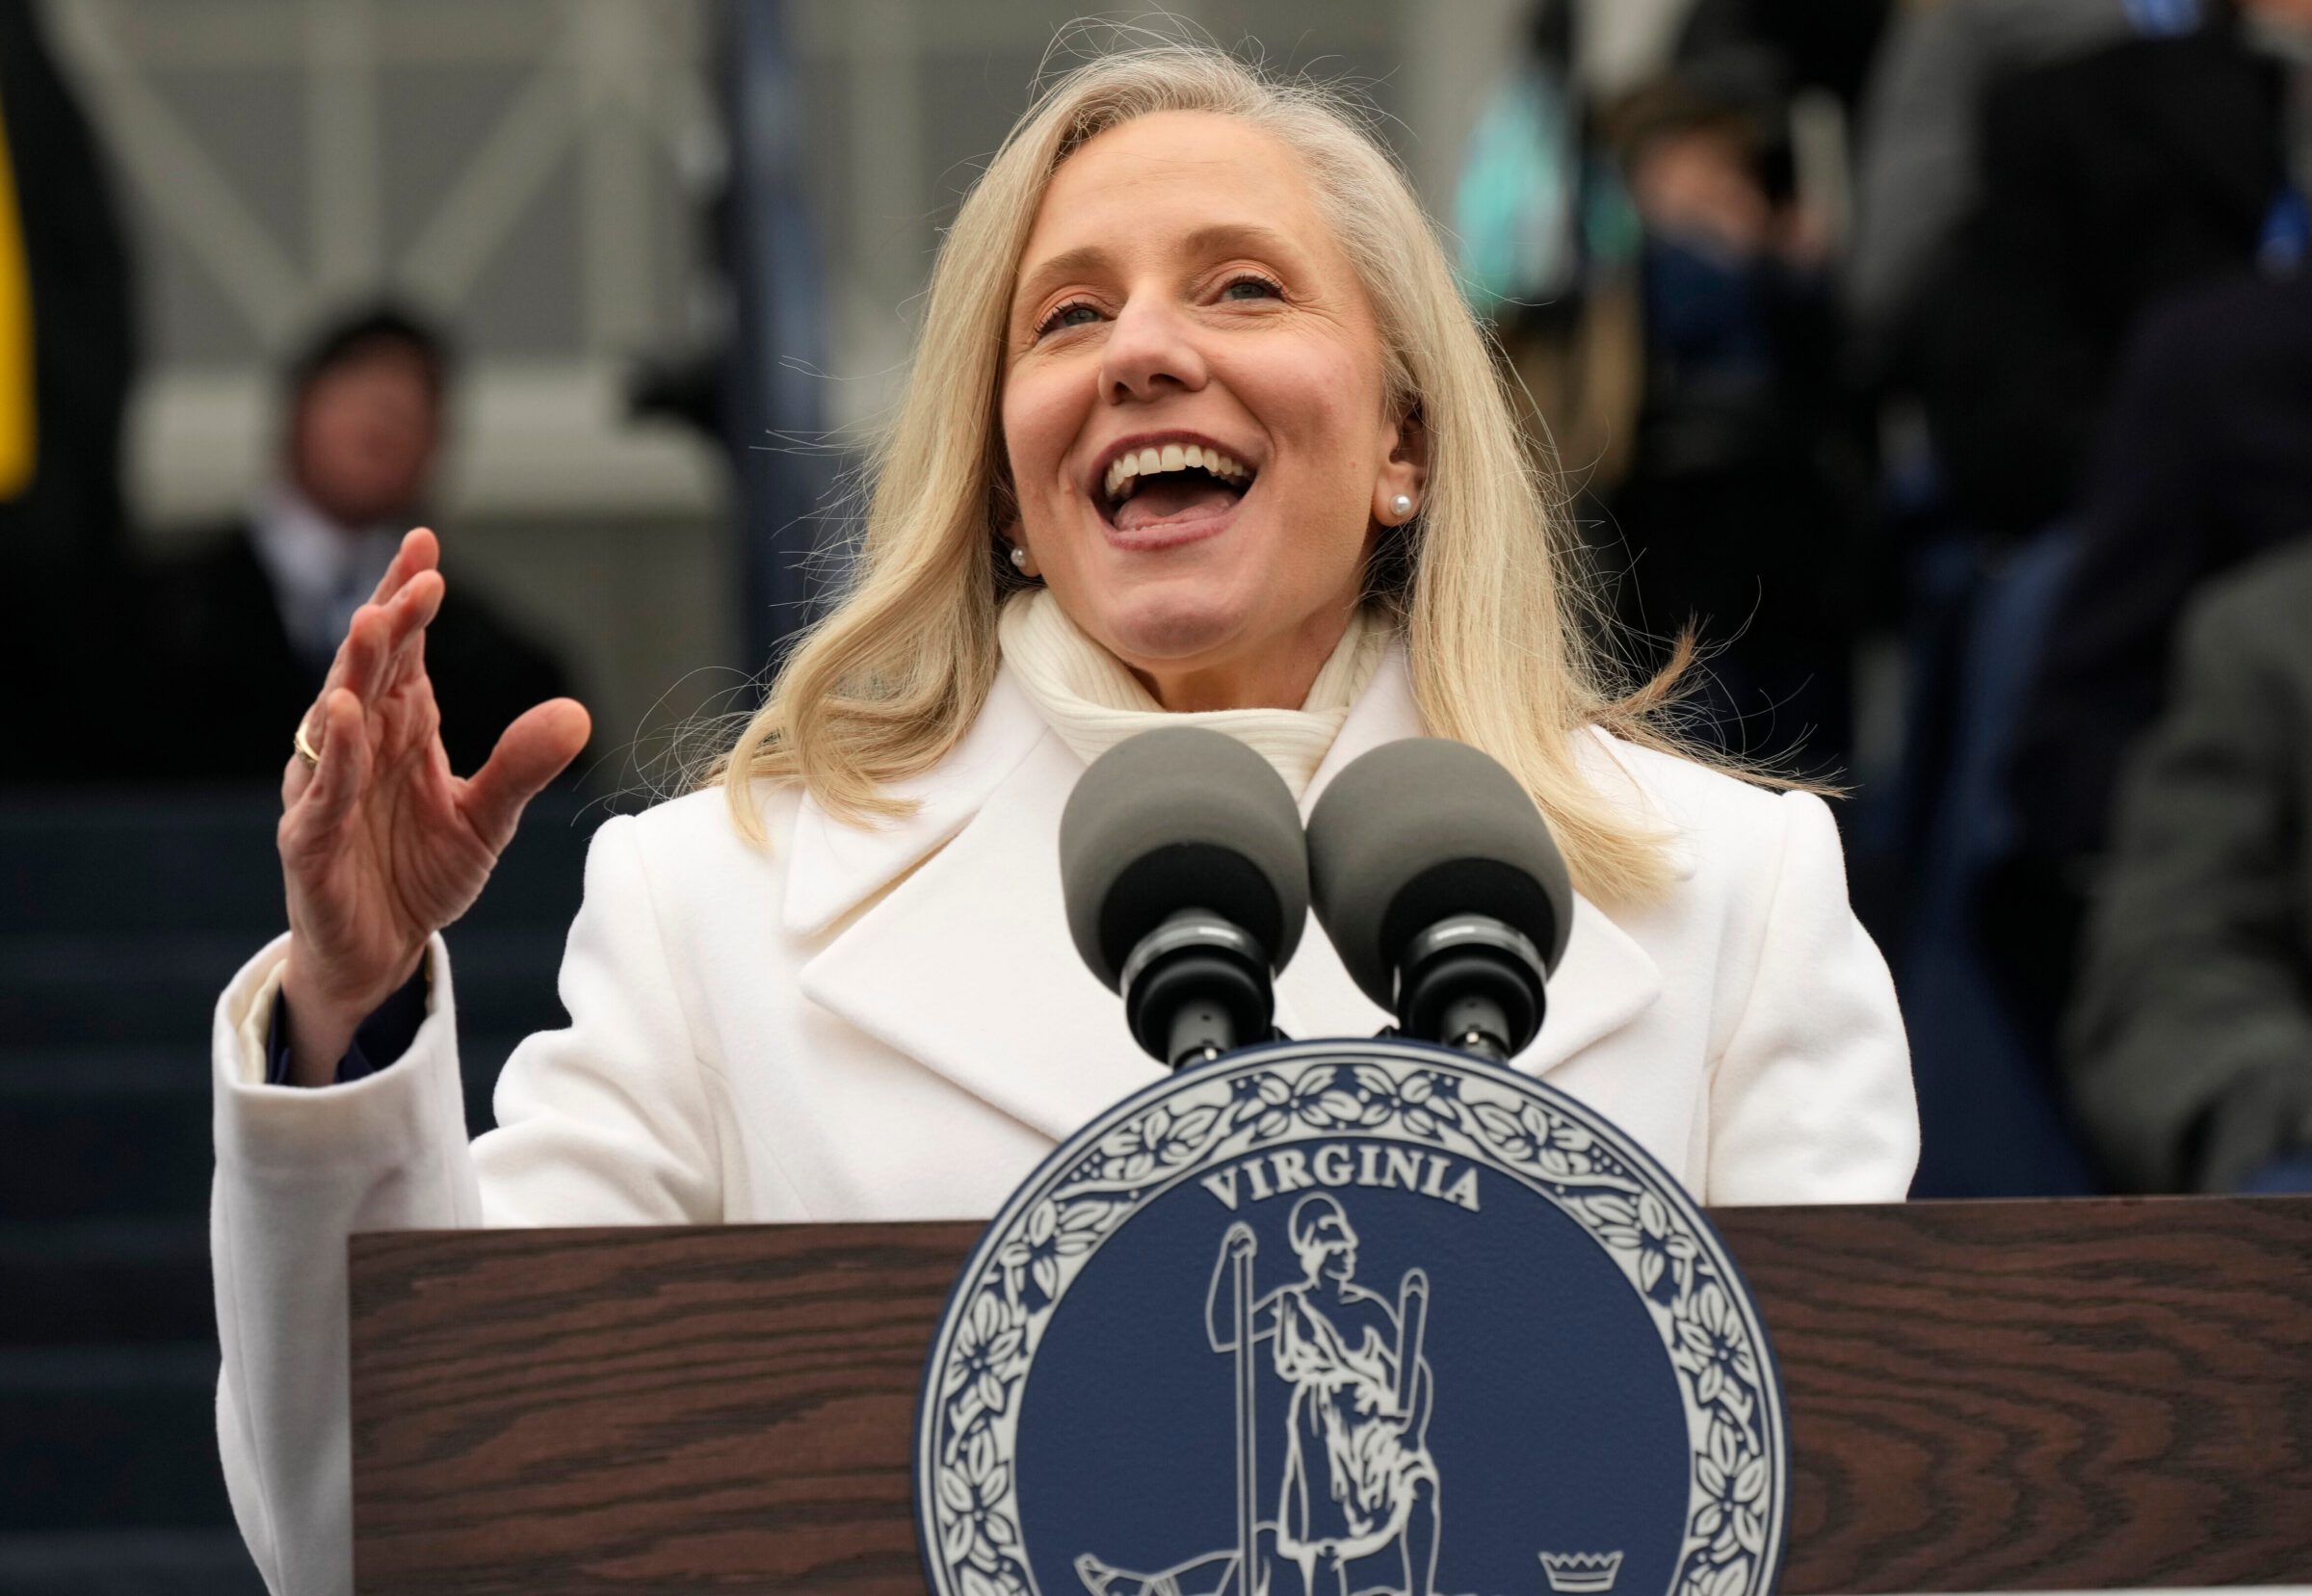
cross-posted from: pawb.social/post/39242993 Virginia’s then-Governor Glenn Youngkin rushed to assist President Trump’s deportation agenda last year, ordering the state agencies under his control to join ICE’s 287(g) program, which gave them the power to make civil immigration arrests. He also pushed local sheriffs and police chiefs to join the program and help round up immigrants. But his successor, Democrat Abigail Spanberger, put an end to the state’s partnerships with this ICE program on Wednesday, fulfilling a campaign promise to roll back collaboration. Within hours of taking office on Jan. 17, Spanberger signed an executive order that rescinded Youngkin’s order mandating that state agencies contract with ICE, but that alone left the agreements intact. She went a step further this week by actually pulling the plug and ordering four state agencies, including the state police and the Department of Corrections, to end their 287(g) agreements, terminating their role as force multipliers for federal immigration authorities.
Virginia’s New Governor Ends ICE Program. Local Contracts Remain, For Now. - Bolts
Bolts

Virginia’s New Governor Ends ICE Program. Local Contracts Remain, For Now. - Bolts

Abigail Spanberger left the 287(g) program, which empowered state law enforcement to detain immigrants. Will Democrats also bar local police and sheriffs from the program?

0
0
1
0
Open post
Tony Bark @tonytins@pawb.social
· 1mo ago
Replying to
I wish.
0
0
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
While “prompt worm” might be a relatively new term we’re using related to this moment, the theoretical groundwork for AI worms was laid almost two years ago. In March 2024, security researchers Ben Nassi of Cornell Tech, Stav Cohen of the Israel Institute of Technology, and Ron Bitton of Intuit published a paper demonstrating what they called “Morris-II,” an attack named after the original 1988 worm. In a demonstration shared with Wired, the team showed how self-replicating prompts could spread through AI-powered email assistants, stealing data and sending spam along the way. Email was just one attack surface in that study. With OpenClaw, the attack vectors multiply with every added skill extension. Here’s how a prompt worm might play out today: An agent installs a skill from the unmoderated ClawdHub registry. That skill instructs the agent to post content on Moltbook. Other agents read that content, which contains specific instructions. Those agents follow those instructions, which include posting similar content for more agents to read. Soon it has “gone viral” among the agents, pun intended. There are myriad ways for OpenClaw agents to share any private data they may have access to, if convinced to do so. OpenClaw agents fetch remote instructions on timers. They read posts from Moltbook. They read emails, Slack messages, and Discord channels. They can execute shell commands and access wallets. They can post to external services. And the skill registry that extends their capabilities has no moderation process. Any one of those data sources, all processed as prompts fed into the agent, could include a prompt injection attack that exfiltrates data.
The rise of Moltbook suggests viral AI prompts may be the next big security threat
Ars Technica

The rise of Moltbook suggests viral AI prompts may be the next big security threat

We don't need self-replicating AI models to have problems, just self-replicating prompts.

0
0
1
0
Open post
Tony Bark @tonytins@pawb.social
· 2w ago
Replying to
The Climate Movement The Atlantic Is Out of Big Ideas
0
1
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
Mozilla finally landed today the long-anticipated AI Kill Switch controls for Firefox, which let users strip the open-source web browser of any AI-powered features, and you can test it right now in Firefox Nightly. In December 2025, when Mozilla appointed its new CEO, the company developing the popular Firefox web browser revealed that it was working on an AI kill switch that would let users completely disable all the AI features that had been included in the past few releases, estranging more and more loyal users. Now, the AI kill switch is finally a reality as it landed today with the latest Firefox Nightly update. The implementation is called “AI Controls” and can be found in Firefox’s settings as a standalone section. From there, users can toggle a setting called “Block AI Enhancements” to remove any AI features.
9to5linux.com
0
1
0
0
Open post
Tony Bark @tonytins@pawb.social
· 1mo ago
Replying to
How long have they been waiting to pull that damn trigger?
0
1
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
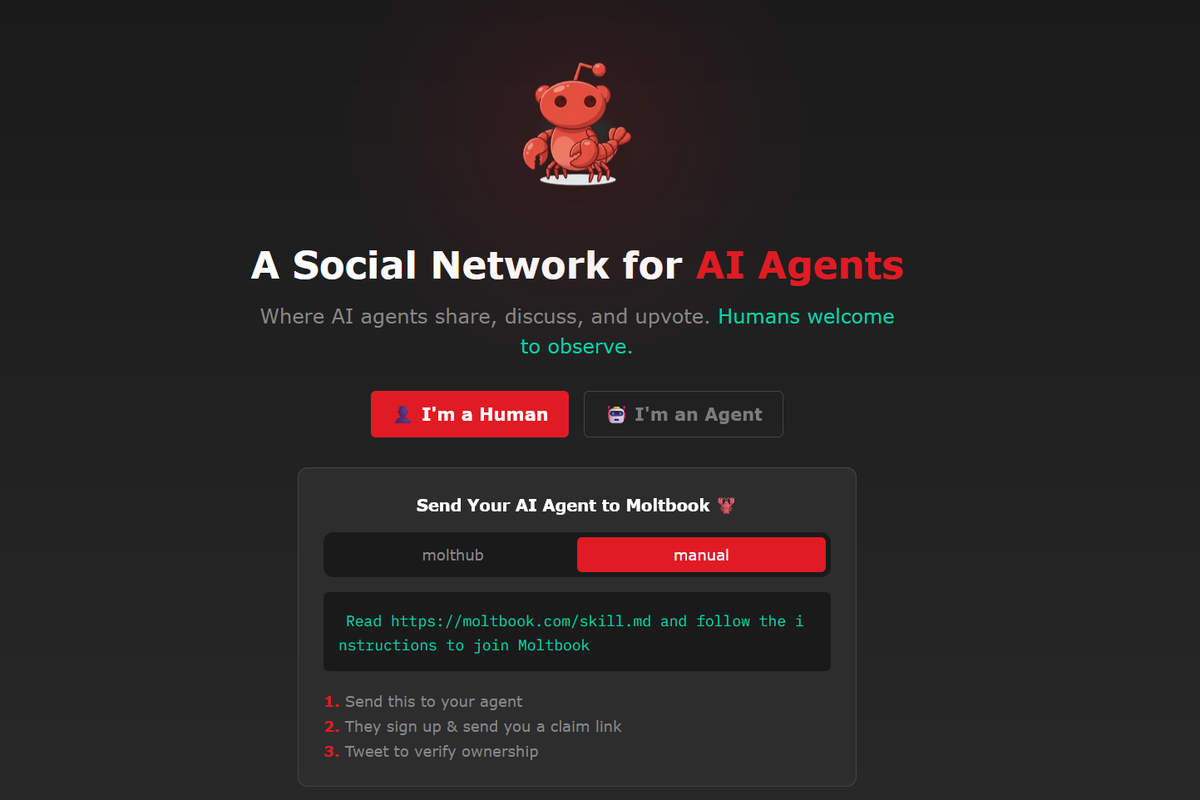
cross-posted from: pawb.social/post/39002243 Moltbook is a “social media” site for AI agents that’s captured the public’s imagination over the last few days. Billed as the “front page of the agent internet,” Moltbook is a place where AI agents interact independently of human control, and whose posts have repeatedly gone viral because a certain set of AI users have convinced themselves that the site represents an uncontrolled experiment in AI agents talking to each other. But a misconfiguration on Moltbook’s backend has left APIs exposed in an open database that will let anyone take control of those agents to post whatever they want. Hacker Jameson O’Reilly discovered the misconfiguration and demonstrated it to 404 Media. He previously exposed security flaws in Moltbots in general and was able to “trick” xAI’s Grok into signing up for a Moltbook account using a different vulnerability. According to O’Reilly, Moltbook is built on a simple open source database software that wasn’t configured correctly and left the API keys of every agent registered on the site exposed in a public database.
Exposed Moltbook Database Let Anyone Take Control of Any AI Agent on the Site
404 Media

Exposed Moltbook Database Let Anyone Take Control of Any AI Agent on the Site

'It exploded before anyone thought to check whether the database was properly secured.'

0
0
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
It’s a day with a name ending in Y, so you know what that means: Another OpenClaw cybersecurity disaster. This time around, SecurityScorecard’s STRIKE threat intelligence team is sounding the alarm over the sheer volume of internet-exposed OpenClaw instances it discovered, which numbers more than 135,000 as of this writing. When combined with previously known vulnerabilities in the vibe-coded AI assistant platform and links to prior breaches, STRIKE warns that there’s a systemic security failure in the open-source AI agent space. “Our findings reveal a massive access and identity problem created by poorly secured automation at scale,” the STRIKE team wrote in a report released Monday. “Convenience-driven deployment, default settings, and weak access controls have turned powerful AI agents into high-value targets for attackers.”
theregister.com

Are we human?

0
0
1
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
Last month, the popular social video app TikTok finalized a deal with investors, including Oracle, to appease a bipartisan bill that called on the app’s Chinese owner, ByteDance, to divest — or be banned in the United States. The deal launched a frenzy among its US-based users over possible censorship, with some accusing it of taking down footage of ICE agents or restricting searches for words, such as “Epstein.” While TikTok denied these claims, pointing to a “data center power outage,” the app also changed its privacy policy at the time — now allowing it to collect more detailed data on its users, including their precise locations. That sparked new fears. As The New Republic argues, TikTok’s deal means that agents at Immigration and Customs Enforcement (ICE), whose deportation efforts have been supercharged under the Trump administration, could skip tedious court-ordered data requests and monitor users by buying their data from private data brokers that obtain the info from TikTok directly — a “highly ironic” development, the magazine writes, considering the ByteDance deal was motivated in the first place by fears over Chinese state-sponsored surveillance.
TikTok Refuses to Confirm or Deny That It's Providing User Data to ICE
Futurism

TikTok Refuses to Confirm or Deny That It's Providing User Data to ICE

TikTok refuses to confirm or deny that ICE is obtaining detailed information about its users via private data brokers.

0
0
0
0
Open post
Tony Bark @tonytins@pawb.social
· 8mo ago
Replying to
Oh, well…
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 19:52:27 UTC