Mathias Payer
Securitatis inquisitor and professor at EPFL leading the HexHive 🐝 group, focusing on system/software security (he/him).
🎉 I'm excited to share that I've been appointed to Full Professor, effective today: https://ethrat.ch/en/appointments-march-26/
Looking back, this milestone would not have been possible without the incredible group of students, collaborators, and colleagues I had the pleasure of working with over the past 20 years of research. I'm also grateful for all the collaborators, letter writers, mentors, supporters, and whoever helped and supported us on the way.
The HexHive group has grown into a vibrant group focusing on software and systems security 🔐. Together we have secured over CHF 12M in funding 💰 for the group (including the prestigious ERC Starting Grant and ERC Advanced Grant), published close to 200 papers 📄, with 26 papers at USENIX Security, 13 at Oakland, 12 at NDSS, and 11 at CCS.
But the achievements I value most are not the distinguished paper awards, open source prototypes, or grants. I'm most proud of the people who spent time in my lab. Out of those, I especially cherish the 16 PhD students who have graduated and are now carrying forward the spirit of the HexHive lab: inclusive, collaborative research in software and system security, working together on security challenges that matter.
What's the state of digital sovereignty for our academic landscape?
Inspired by a similar post looking at digital sovereignty of municipalities, I explored what messaging infrastructure universities rely on. Sadly, many have switched to hyper scalars but few large universities keep running their own email infrastructure. Germany, Austria, France does not look too bad and lead by example.
[Note that the assessment is based on a simple MX records comparison against a list of known scalars, I don't yet check SPF records or guesstimate the SMTP software/version, this may be done in a future version.]
Check out the interactive map: https://nebelwelt.net/gannimo/unimx/
RE: https://infosec.exchange/@aristot73/116463759957379327
LLM bug finding vs fuzzing: LLMs explore a different part of the bug space, my guess is that we'll see a similar curve as with fuzzing where new bugs get more expensive to find with the key difference that we can hit new capabilities to find different types of bug patterns resulting in a saw function than just a sigmoid. Fun times ahead, especially for researchers looking into defense!
From "What the Fuzz?" to "All The Fuzz!" (Keynote fuzzing workshop @ NDSS'26)
Reflections on the three phases of fuzzing: from origins of fuzzing to the greybox fuzzing, ending with how fuzzing will continue evolving in the future.
Comments welcome!
NDSS 2026 - FUZZING 2026, Welcome and Opening Remarks, and Keynote by Mathias Payer
Have you ever wondered what is running on your Android phone? As it turns out, it's not just the apps that you install but there are also so called "trusted applications" that handle your sensitive data like passwords, fingerprints, or keys.
We have developed a high-level rehosting approach that enables security researchers to thoroughly test these applications and found 17 0-days that were responsibly disclosed and are now fixed. This work was presented at this week's IEEE Symposium on Security and Privacy, one of the top-4 security conferences.
https://nebelwelt.net/blog/2026/0521-taemu.html
LLMs are automating not just coding, but vulnerability discovery and exploitation. At scale, this shifts the economics of offensive security: lower skill barriers, faster iteration, and massively increased attack surface coverage.
As exploitation becomes cheap and ubiquitous, how can we leverage this for defense?
For ACM CCS we are organizing a doctoral symposium. The goal is to enable PhD students to discuss their research agenda and get feedback from mentors across varying sub areas.
The submission deadline is July 30 and accepted students will receive a generous travel grant. So please apply and share with your colleagues!
https://www.sigsac.org/ccs/CCS2026/call-for/call-for-doctoral-symposium.html
It was my honor to give a keynote at the FUZZING workshop at #NDSSSymposium today. Under the title From "What The Fuzz?" to "All The Fuzz!", I discussed how fuzzing evolved over time from its origins as random mutation testing over the greybox revolution to fuzzing niches. The key takeaways are that fuzzing matured as a field, coverage-guided feedback was key to its success, and the future is customizing fuzzing to niches where the next breakthroughs will be contextual and semantic.
The slides are available at https://nebelwelt.net/files/26FUZZING-presentation.pdf
Happy to hear any feedback!
It was a pleasure to present Sysphuzz at #NDSSSymposium this year. Our key intuition is that focusing in under-fuzzed areas allows us to discover new bugs even in extensively fuzzed code. We applied this intuition to the Linux kernel by boosting basic blocks that were rarely hit even after years of fuzzing.
The blog post is at: https://nebelwelt.net/blog/2026/0226-sysyphuzz.html
Good bye San Francisco, it was a pleasure!
The last few days I spent at the IEEE Symposium on Security and Privacy (Oakland) to catch up with friends, learn about the latest research in security and to support Philipp in presenting our latest research work TÄMU --- high-level rehosting of trusted applications on the Android platform. Check out the short blog for a few more details:
https://nebelwelt.net/blog/2026/0521-oakland.html
On my way ✈️ to San Diego for @ndsssymposium@bird.makeup to catch up on the latest security trends. I'm excited to present our paper Sysyphuzz on focusing energy on under explored areas in the kernel and to give a keynote at the fuzzing workshop on Friday. Let me know if you're around for a chat or, ideally, for a morning run! 🌅🏄🏃
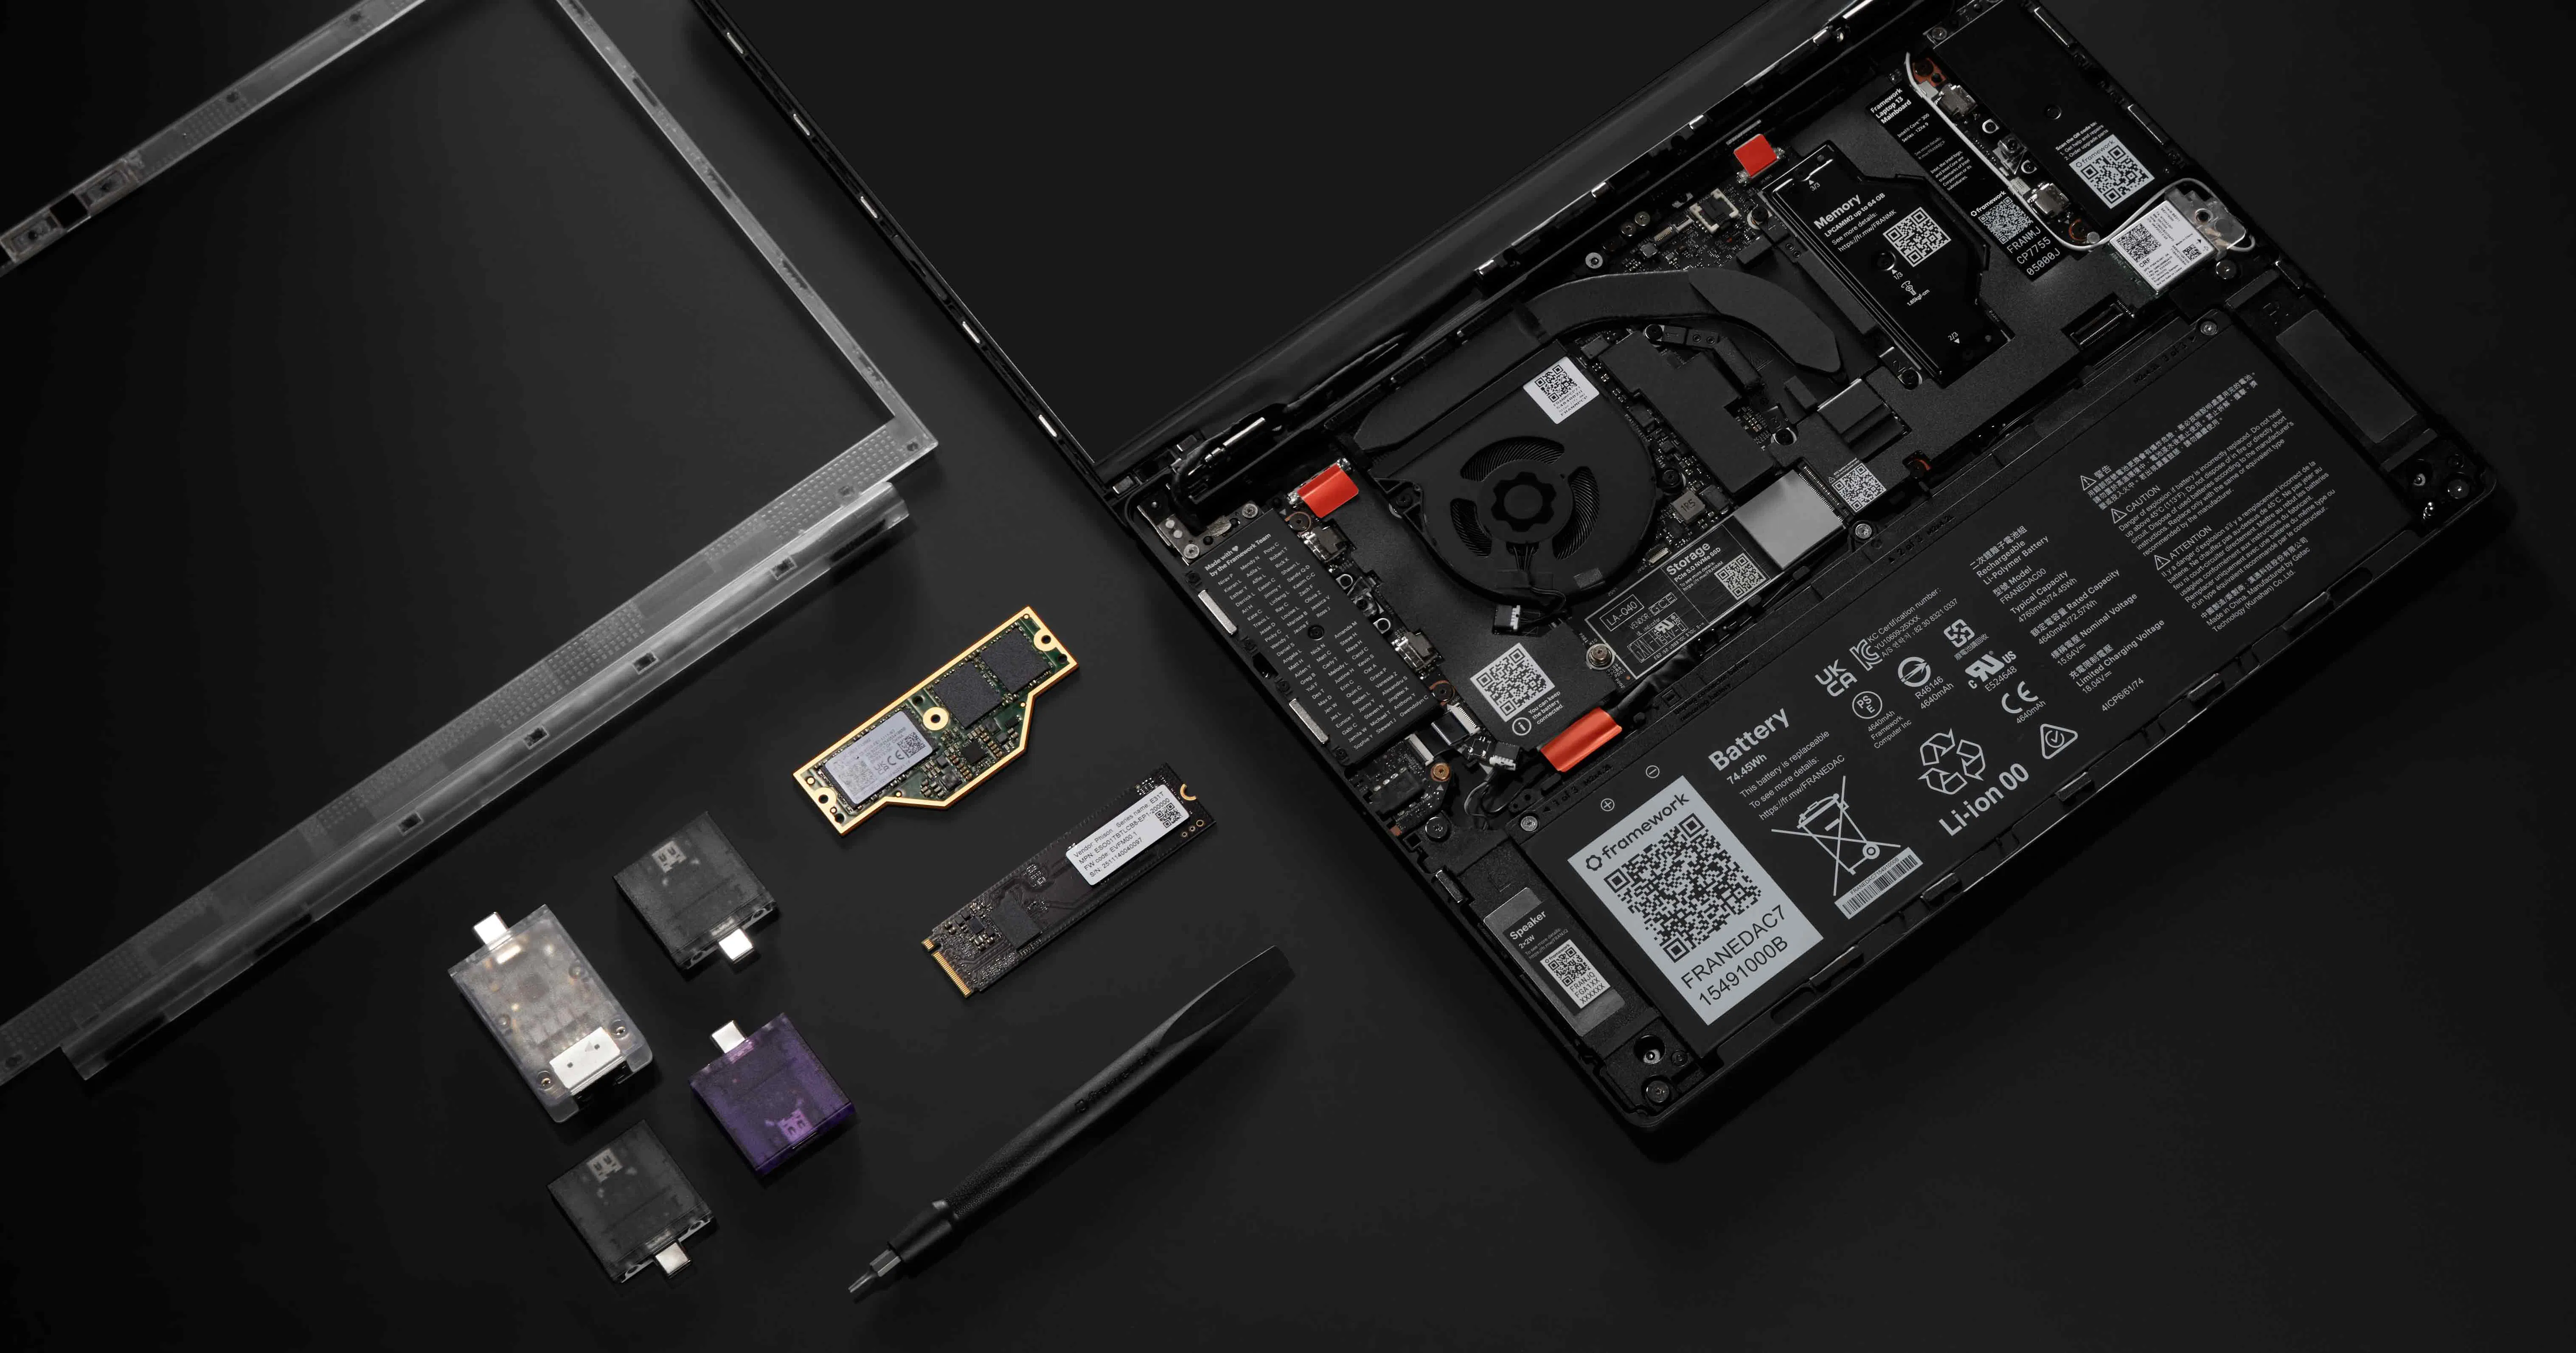
Has anyone checked out the new Frame.Work Laptop 13 Pro? I'm especially interested in power management given that I hate the most recent Lenovo X1 as the keyboard is annoying, it no longer has the trackpoint, it only support s2idle, and in general battery runtime is abysmal. [I.e., would not recommend Lenovo anymore]
Subscription bombing is a (re-)emerging threat vector where attackers flood your inbox with thousands of unwanted messages. This is not just nuisance but attackers often leverage subscription bombing to hide their true goals such as support scams or account takeovers. Even worse, subscription bombing has become a service. We analyzed 24 subscription bombing attack campaigns to reflect and provide insights.
Check out our CACM article for details: https://cacm.acm.org/practice/subscription-bombing-email-under-attack/
While I'm a bug fan of second factor authentication for high risk environments, it also comes at a cost due to additional friction.
Can someone explain to me while the EU for the Horizon portal had to create a new dedicated 2FA app that maximises friction? I log into this portal once every 1.5 years. This means I'll likely have to go through the 2FA recovery process every single time.
Getting to MPI is quite a challenge. Bus - Train - Flight - Skytrain - S Bahn - Bus (Schienenersatzverkehrsautobus) - Train - Underground. I spent over 2hrs for the final 40km. If I were just named Kipchoge 🏃😅