Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

daniel:// stenberg://

@bagder__dup_3144@mastodon.social
mastodon 4.8.0-alpha.3+pr-41085-a68fedb
  • Open on mastodon.social

I write curl. I don't know anything.

52437 Followers
284 Following
47 Posts
Joined April 03, 2017
website:
https://daniel.haxx.se/
github:
https://github.com/bagder
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

a detail you probably didn't know: nowhere in any #curl documentation do we use the word "very". It is a banned word enforced by a CI check. This rule encourages us to rewrite and instead use more appropriate words. Makes us write better English.

408
65
138
1
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

I keep getting offers from randos offering to setup various crypto currency things to sponsor me or curl.

I will NEVER agree to have my name associated with any crypto currency efforts/scams. There's no room for debate. A hard no.

335
15
95
1
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago
The #curl project is soon going to move away from GitHub again for its security reporting. It simply doesn't work the way we need it to. Proper announcement will follow in the near future.
285
4
131
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

"Our proprietary AI robots independently recreate any open source project from scratch"

https://malus.sh/

Mastodon

daniel:// stenberg:// (@bagder@mastodon.social)

"Our proprietary AI robots independently recreate any open source project from scratch" https://malus.sh/

209
0
200
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago
The button has been pressed.
260
7
53
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago

The end of the #curl bug-bounty

https://daniel.haxx.se/blog/2026/01/26/the-end-of-the-curl-bug-bounty/
The end of the curl bug-bounty
daniel.haxx.se

The end of the curl bug-bounty

tldr: an attempt to reduce the terror reporting. There is no longer a curl bug-bounty program. It officially stops on January 31, 2026. After having had a few half-baked previous takes, in April 2019 we kicked off the first real curl bug-bounty with the help of Hackerone, and while it stumbled a bit at first … Continue reading The end of the curl bug-bounty →

240
14
210
1
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago
Boosted by @kaia@pleroma.soykaf.com
Getting ready for #EOSAwards26
207
8
29
1
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

I found this Veratasium documentary on the xz Jia Tan backdoor adventure quite good and surprisingly detailed:

https://www.youtube.com/watch?v=aoag03mSuXQ

The Internet Was Weeks Away From Disaster And No One Knew

164
24
122
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago

the public consultation on "European Open Digital Ecosystems" apparently received 1,658 submissions. One of the biggest public consultations ever apparently.

Well done fellow Open Sourcers!

193
0
126
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago
Boosted by @ferrix@mastodon.online

Three years ago I blogged about #nuget serving outdated #curl packages.

They then removed the packages I found.

I checked nuget again today and immediately found a nine year old curl package that is downloaded at the rate of 1,000 times/week from there... with 64 known vulnerabilities.

The blog post from back then: https://daniel.haxx.se/blog/2023/03/02/the-curl-nuget-story/
The curl nuget story
daniel.haxx.se

The curl nuget story

Recently there has been an interesting debate in the Open Source world where people have objected to being called "Suppliers" as in Supply Chain Security when you are but an Open Source developer offering your code to the world for free and at no cost but also without any warranties. That is not a supplier, … Continue reading The curl nuget story →

152
10
122
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago
IRC made me do #curl https://youtu.be/ohzzGy5K9Dk

How an IRC bot spawned the world’s most prolific software

134
12
74
1
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago
A big and warm thank you hug to all the friends I met and talked to in Brussels this time. Two packed days of events before #FOSDEM including an awesome prize ceremony, then two intense days at ULB where I must have talked to more than a hundred persons. All the positivity, the appreciation, the smiles, the ideas, the energy. I got to end-keynote the thing and then top it off with more drinks and countless friends - again. I'm drained now, but in a good way. I'll be back next year.
153
1
51
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago
Some of you will be glad to know that the #curl dashboard now features the "graphs in the dashboard" graph https://curl.se/dashboard1.html#graphs-on-the-dashboard
curl.se

curl - Project status dashboard

109
23
52
1
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

just noticed I'm mentioned on the AI slop wikipedia page: https://en.wikipedia.org/wiki/AI_slop

AI slop - Wikipedia
en.wikipedia.org

AI slop - Wikipedia

119
3
47
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

10K #curl downloads per year

https://daniel.haxx.se/blog/2026/03/09/10k-curl-downloads-per-year/
10K curl downloads per year
daniel.haxx.se

10K curl downloads per year

The Linux Foundation, the organization that we want to love but that so often makes that a hard bargain, has created something they call "Insights" where they gather lots of metrics on Open Source projects. I held back so I never blogged and taunted OpenSSF for their scorecard attempts that were always lame and misguided. … Continue reading 10K curl downloads per year →

106
17
74
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago
#FOSDEM
138
9
39
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 10mo ago
Boosted by @ferrix@mastodon.online
This is not working. The number of #hackerone report submissions for #curl in 2025 is going through the roof, while the quality is going through the floor. And the year isn't over yet.
158
16
105
1
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

commit time zone distribution in #curl

https://github.com/curl/stats/pull/24

GitHub

timezones: add by bagder · Pull Request #24 · curl/stats

Scripts for generating project statistics and for plotting them as graphs. - timezones: add by bagder · Pull Request #24 · curl/stats

79
5
42
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 9mo ago
Boosted by @ferrix@mastodon.online
the AI slop in security reports have developed slightly over time. Less mind-numbingly stupid reports now, but instead almost *everyone* writes their reports with AI so they still get overly long and complicated to plow through. And every follow-up question is another minor essay discussing pros and cons with bullet points and references to multiple specifications. Exhausting nonetheless.
127
0
59
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago
This year counts as #curl 30 years, counting from the first httpget 0.1 release in November 1996. I'm thinking we could fly a special logo for the occasion on the #curl front page throughout the year. Maybe *you* can make one that looks festive and still confident and trustworthy? To trigger some thoughts, here's my take:
73
16
57
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago
At the first event of the day. EU Open Source Policy Summit
86
2
12
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago

I'm a little amazed by the amount of CVEs released by OpenSSL today: https://openssl-library.org/news/vulnerabilities/

12(!) of them were reported by people at Aisle.

Aisle makes an AI-powered code analyzer. That's what they use to find these flaws.

I mean if you are curious what AI can do in Open Source security when used for good.

openssl-library.org

Vulnerabilities | OpenSSL Library

75
5
38
1
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

Like every sane person, I've now added a "medals" section to my personal website. 😎
https://daniel.haxx.se/

Daniel Stenberg
daniel.haxx.se

Daniel Stenberg

Documentation and ramblings of Daniel Stenberg, founder and lead developer of curl.

60
0
6
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

"I'm concerned about LLM code in #curl and would like to suggest a code ban"

https://github.com/curl/curl/discussions/20972

GitHub

I'm concerned about LLM code in curl and would like to suggest a code ban · curl curl · Discussion #20972

I'm concerned about generative AI LLM code in curl, including AI auto completion use in editors, and I'm wondering whether the project should adopt a policy to ban it. Please note this doesn't invo...

45
7
57
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

Wget had its initial release (under a different name) in January 1996, so it has now already surpassed its 30th birthday.

curl is way behind, as it did not start its journey (under a different name) until November 11 1996

52
3
11
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

"the game is lagging"

From my #inbox

https://daniel.haxx.se/email/2026-02-26.html

Daniel Stenberg -- Email
daniel.haxx.se

Daniel Stenberg -- Email

The Daniel email collection

52
0
18
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 6mo ago

noq is a new QUIC library in town, written in rust: https://www.iroh.computer/blog/noq-announcement

iroh.computer

noq, noq, who's there?

Introducing noq: n0's QUIC implementation

39
4
19
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago
One year ago, searching for "CURLOPT_SSL_VERIFYPEER, 0” gave me 153k hits on GitHub and I blogged about the sorry state of TLS certificate verification in code. (as every hit indicates code that probably disables verification) Now? 181k hits. 20% more one year later. The blog post from last year: https://daniel.haxx.se/blog/2025/02/11/disabling-cert-checks-we-have-not-learned-much/
disabling cert checks: we have not learned much
daniel.haxx.se

disabling cert checks: we have not learned much

And by that I mean the global "we" as in the world of developers. In the beginning there was SSL When I first learned about SSL and how to use it in the mid to late 1990s, it took me a while to realize and understand the critical importance of having the client verifying the … Continue reading disabling cert checks: we have not learned much →

49
8
27
1
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

my week: https://lists.haxx.se/pipermail/daniel/2026-March/000148.html

Bug-Bounty: False, zip bombs, "just", badwords, release, new record, NTLM, SMB, 10K downloads, dependencies, nuget

lists.haxx.se

[Daniel's week] March 13, 2026

38
1
14
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

curl.se over the last 30 days:

Served 77.12 TB of data at 3.81k requests/second.

95.91% of the object sizes were <1KB.
0.01% of the downloaded object sizes were 1-10MB (a tarball download)

99.69% of the content delivered was cached by the CDN.

Thanks #Fastly!
42
0
12
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago

More of the same: https://redmonk.com/kholterhoff/2026/02/03/ai-slopageddon-and-the-oss-maintainers/

AI Slopageddon and the OSS Maintainers
console.log()

AI Slopageddon and the OSS Maintainers

AI slop is ripping up the social contract between maintainers and contributors essential to open source development. Practitioners have been repeatedly assured that AI would supercharge their communities, but so far that hasn’t been the case. Just look at what happened last month. Mitchell Hashimoto’s Ghostty implemented a zero-tolerance policy where submitting bad AI-generated code

50
0
54
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

Today is two years since #curl passed its HTTP/3 security audit with flying colors:
"no major discoveries or security problems"

https://daniel.haxx.se/blog/2024/02/23/curl-http-3-security-audit/
curl HTTP/3 security audit
daniel.haxx.se

curl HTTP/3 security audit

An external security audit focused especially on curl's HTTP/3 components and associated source code was recently concluded by Trail of Bits. In particular on the HTTP/3 related curl code that uses and interfaces the ngtcp2 and nghttp3 libraries, as that is so far the only HTTP/3 backend in curl that is not labeled as experimental. … Continue reading curl HTTP/3 security audit →

43
0
17
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

I'm one of the early "members" of the Open Source Endowment. Eager to see where this is going:

"Truly sustainable funding for critical OSS through a community‑driven endowment"
https://endowment.dev/

Open Source Endowment — World
Open Source Endowment

Open Source Endowment — World

The Open Source Endowment provides truly sustainable funding for critical open source software through a community-driven endowment model.

35
1
23
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

If you need a #curl version with support for OpenSSL v1 for a few more years, we got you covered: https://rock-solid.curl.dev/

rock-solid.curl.dev

Rock-solid curl - long term support

35
0
20
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 9mo ago

We know what a Friday needs to get good and I'm happy I can deliver it: a new graph.

#if density in curl source code over time. Fascinatingly static through the years counted per 1000 lines of code.

37
0
9
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago
I return back home from #FOSDEM with only a few hundred curl stickers left. I say we did a good job.
32
0
4
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 8mo ago

If you're bored and are open for helping out documenting #curl, we have a list of outstanding tasks to work on in the "everything curl" book:

https://github.com/curl/everything-curl/issues

GitHub

Issues · curl/everything-curl

The book documenting the curl project, the curl tool, libcurl and more. Simply put: everything curl. - Issues · curl/everything-curl

27
0
24
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

Why #Curl Shut Down Its Bug Bounty Program w/ Daniel Stenberg

https://youtu.be/9CTwcMcvJ_o

The Creator of Curl on Why AI Is Breaking Bug Bounties w/ Daniel Stenberg

18
0
13
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

One hundred #curl graphs

https://daniel.haxx.se/blog/2026/03/15/one-hundred-curl-graphs/
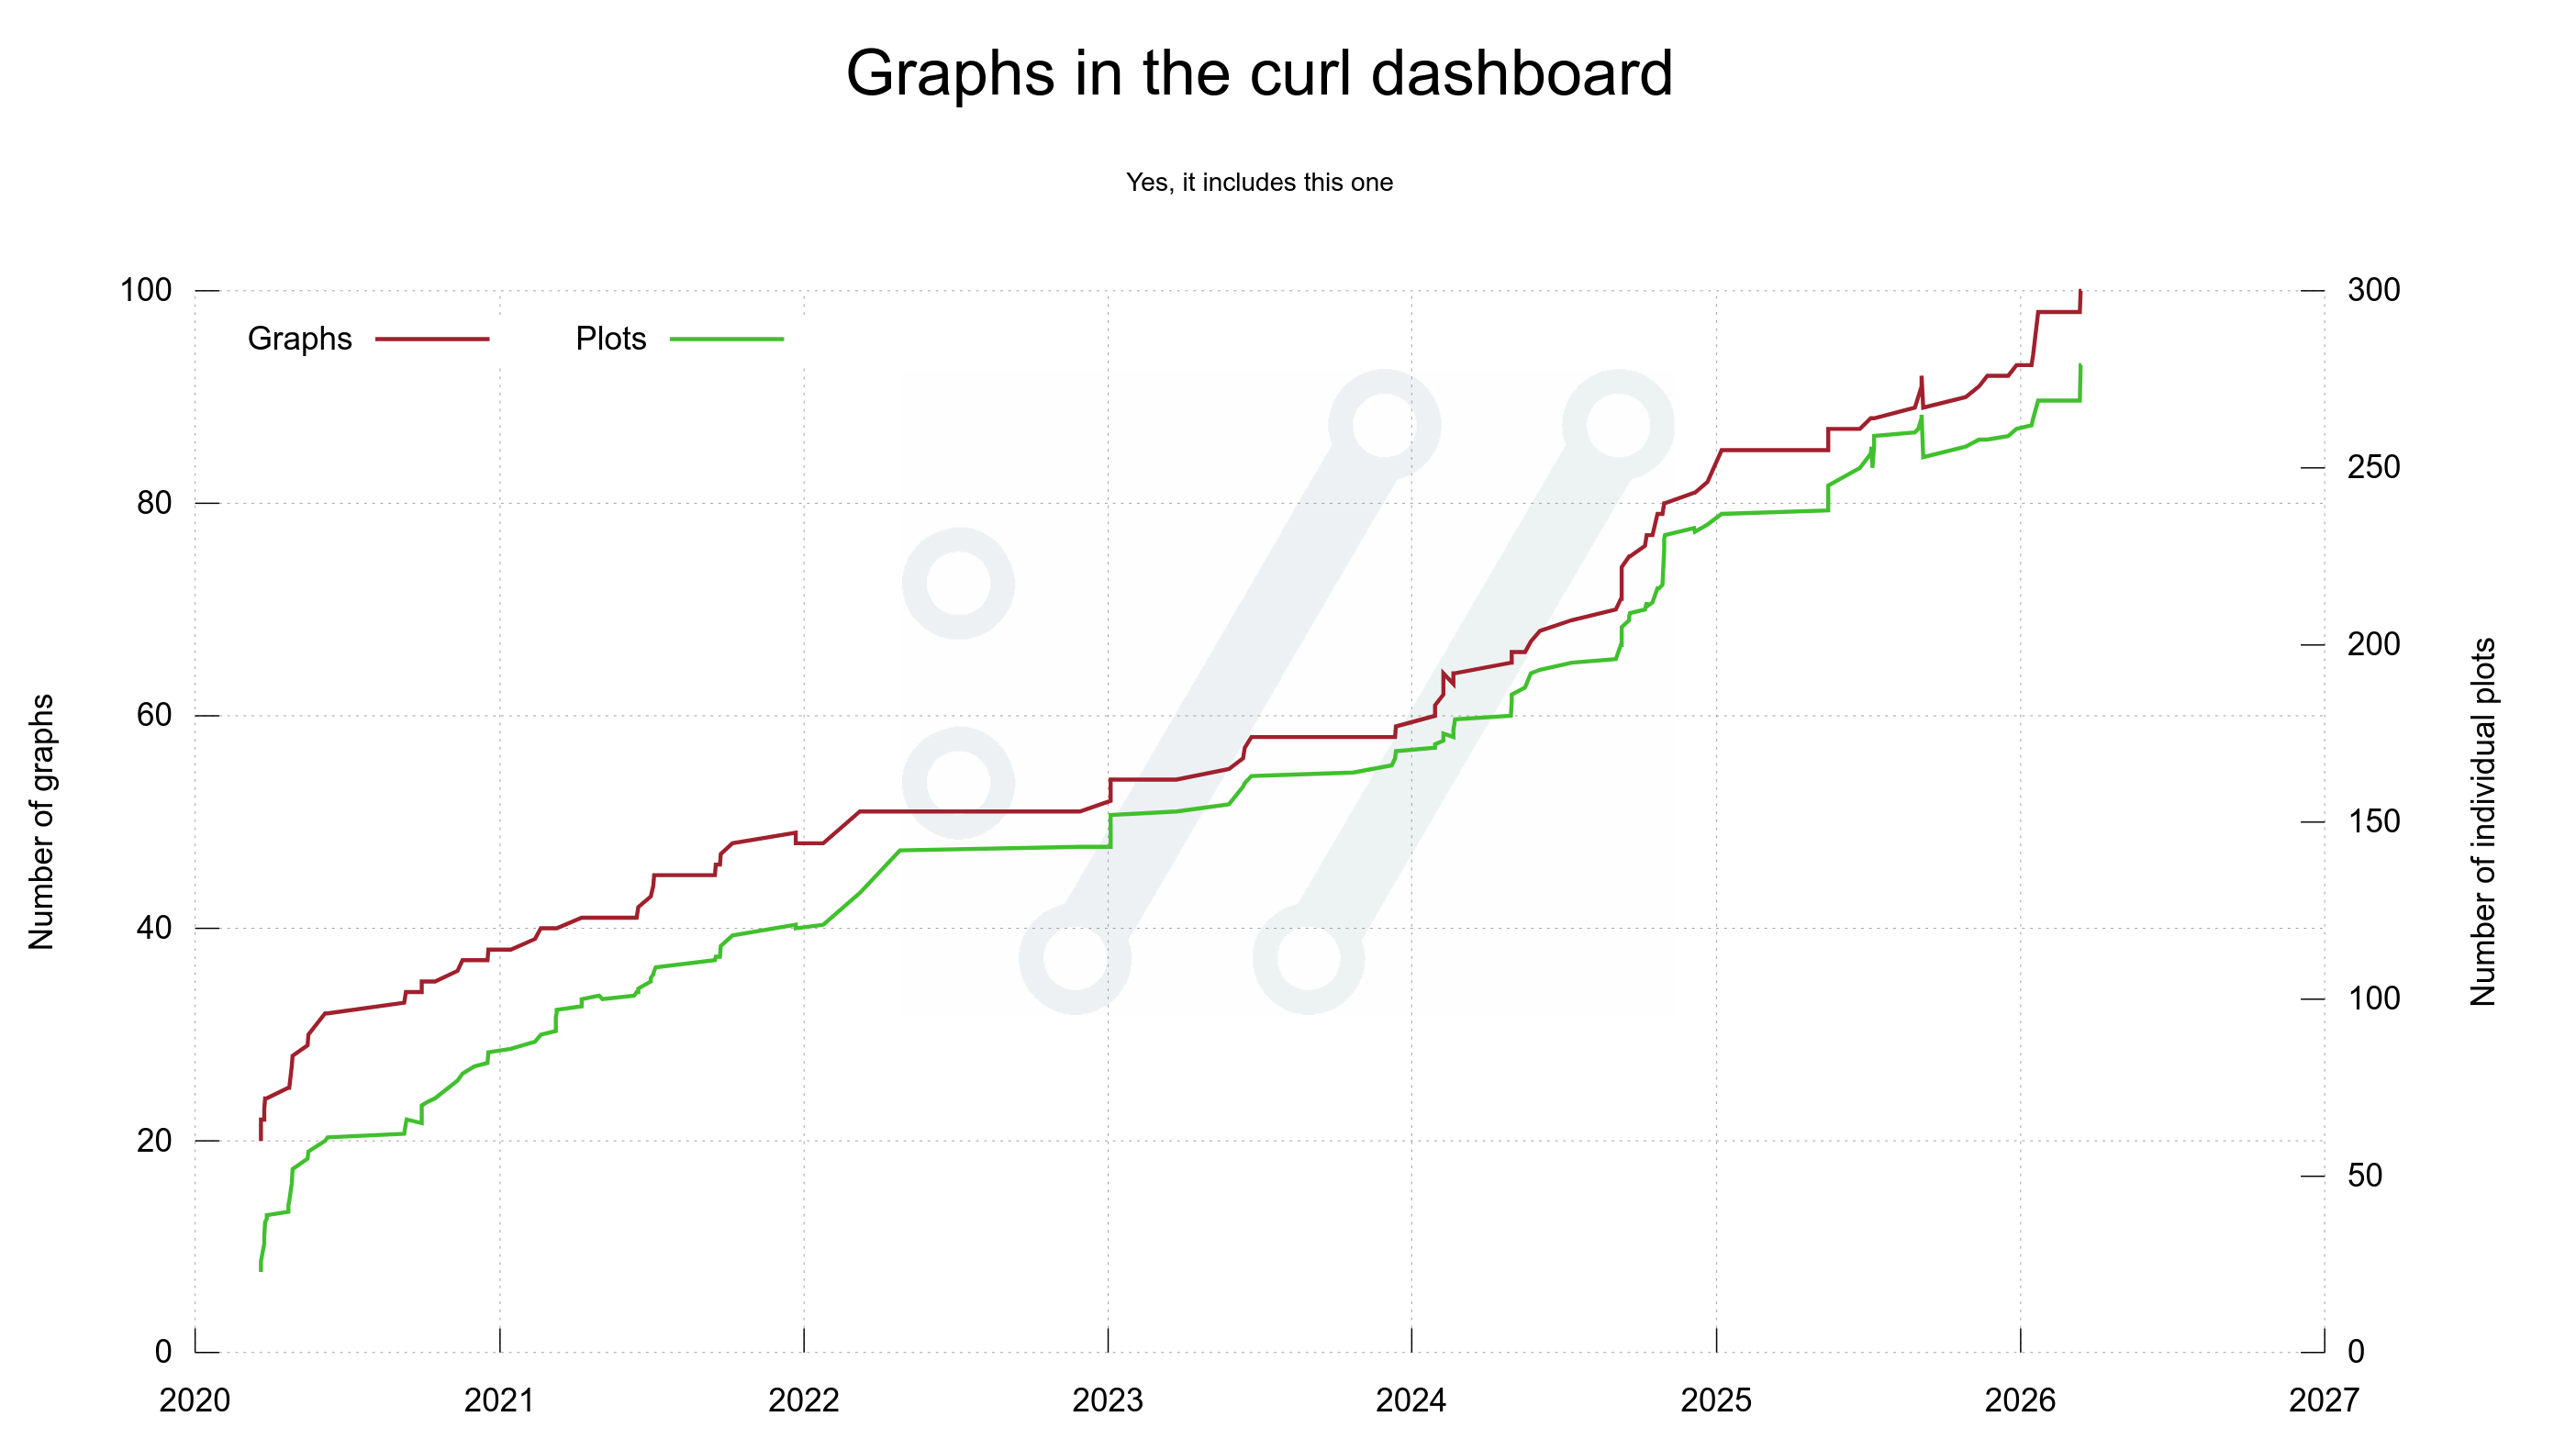
One hundred curl graphs
daniel.haxx.se

One hundred curl graphs

In the spring of 2020 I decided to finally do something about the lack of visualizations for how the curl project is performing, development wise. How does the line of code growth look like? How many command line options have we had over time and how many people have done more than 10 commits per … Continue reading One hundred curl graphs →

18
5
10
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

The GitHub Secure Open Source Fund helped #curl and others to beef up security https://github.blog/open-source/maintainers/securing-the-ai-software-supply-chain-security-results-across-67-open-source-projects/
Securing the AI software supply chain: Security results across 67 open source projects
The GitHub Blog

Securing the AI software supply chain: Security results across 67 open source projects

The GitHub Secure Open Source Fund helped 67 critical AI‑stack projects accelerate fixes, strengthen ecosystems, and advance open source resilience.

21
3
7
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 21mo ago

Remember: it is a calmer more chill life without copyright years. https://daniel.haxx.se/blog/2023/01/08/copyright-without-years/
Copyright without years
daniel.haxx.se

Copyright without years

Like so many other software projects the curl project has copyright mentions at the top of almost every file in the source code repository. Like Copyright (C) 1998 - 2022, Daniel Stenberg ... Over the years we have used a combination of scripts and manual edits to update the ending year in that copyright line … Continue reading Copyright without years →

84
0
41
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago
C'mon, the protocol Gemini brought the name conflict problem on themselves long before Google made it worse by also doing a product with that name. It's not a very creative name. Just look at the list just Wikipedia has for what the name might possibly refer to: https://en.wikipedia.org/wiki/Gemini
en.wikipedia.org

Gemini - Wikipedia

12
0
3
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

Welcome Florian Imdahl as #curl commit author 1447: https://github.com/curl/curl/pull/20748

GitHub

docs: Some nitpicks by ffflorian · Pull Request #20748 · curl/curl

Hi, I did the following: replaced double spaces with single space where applicable replaced "favourite" with "favorite" added language identifiers to code blocks in markdown fi...

10
0
3
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

See you in Oslo on Thursday? https://ndcsecurity.com/agenda/three-decades-of-curl-0ugm/0m55j1o34kp

ndcsecurity.com
10
0
3
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

The third and final release candidate for #curl 8.19.0 is now available at
https://curl.se/rc/

curl.se

curl release candidates

9
0
1
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 7mo ago

My week: https://lists.haxx.se/pipermail/daniel/2026-February/000147.html

vacation, security, distro meeting, curl up, NDC Security, rc, lagging, rock-solid, decomplexification, netstack, user survey, foss-north

lists.haxx.se

[Daniel's week] February 27, 2026

8
0
3
0
Open post
bagder__dup_3144 @bagder__dup_3144@mastodon.social
· 11mo ago
@ivolimmen@toot.community no.
9
0
1
0
Back
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p
313k7r1n3

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 13:26:52 UTC