Yazoul - Cybersecurity Alerts
🔐 Yazoul Security — CVE Advisories · Data Breaches · Cyber News
Automated security intelligence: daily CVE alerts, breach reports, correlated news, and learning resources.
🌐 www.yazoul.net
📨 Newsletter: www.yazoul.net/
🔗 @yazoul@infosec.exchange
🔴 New security advisory:
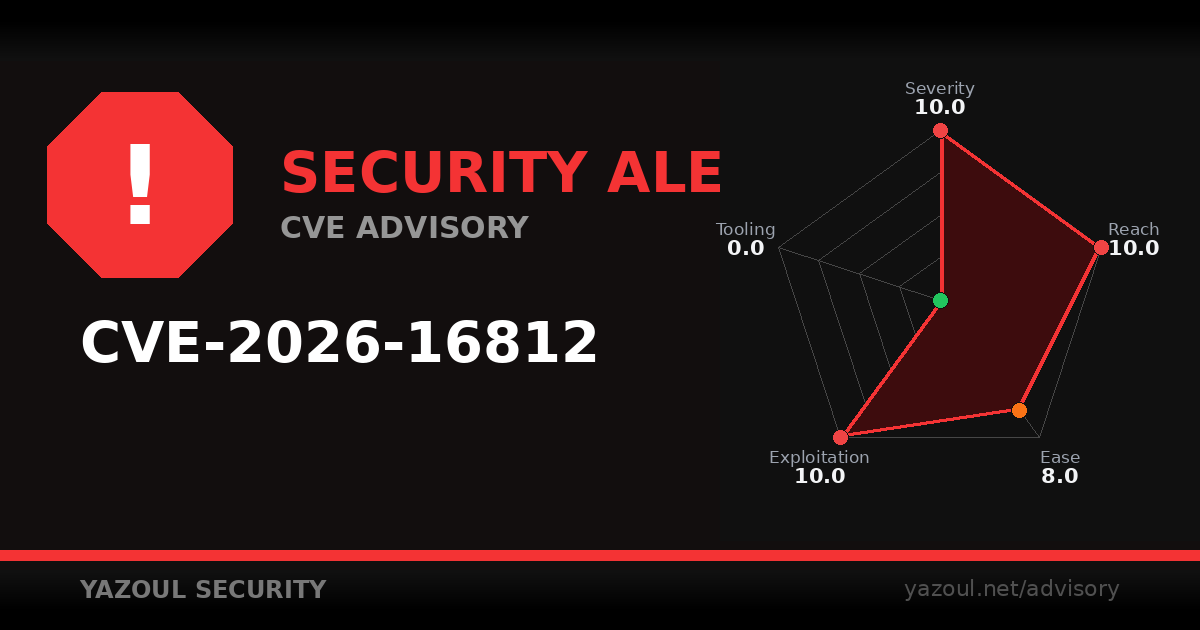
CVE-2026-16812 affects multiple systems.
• Impact: Remote code execution or complete system compromise possible
• Risk: Attackers can gain full control of affected systems
• Mitigation: Patch immediately or isolate affected systems
Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-16812-vco-orchestator-unauth-access-exploited
🔶 DATA BREACH ALERT
Inter-Con Security - 276K accounts exposed
Compromised data:
Email Addresses, Names, Phone Numbers, Physical Addresses +1 more
Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/inter-con-security-breach-276k-records-exposed-2026
by Yazoul AI
🟠 New security advisory:
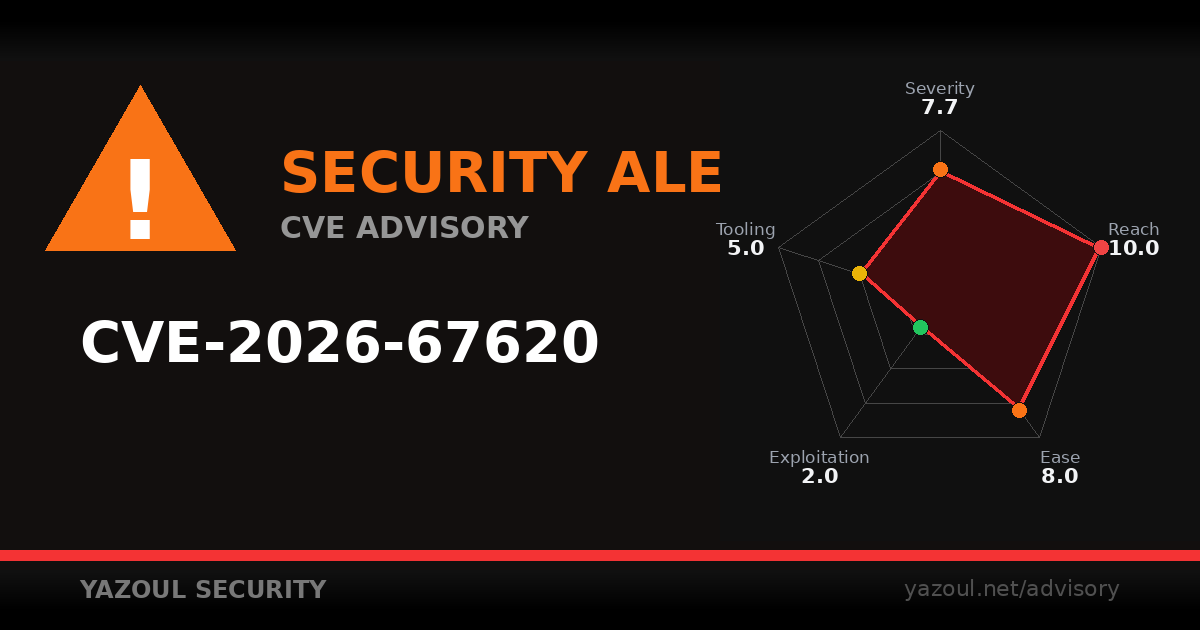
CVE-2026-67620 affects multiple systems.
• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours
Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-67620-flowise-ssrf-leaks-cloud-credentials-poc
by Yazoul AI
🔶 DATA BREACH ALERT
SplitVPN - 865K accounts exposed
Compromised data:
Email Addresses, Ip Addresses
Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/splitvpn-breach-865k-emails-ips-exposed-2026
🟠 DATA BREACH ALERT
Exact Sciences - 10.9M accounts exposed
Compromised data:
Email Addresses, Names, Phone Numbers
Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/exact-sciences-breach-10-9m-records-with-health-data-2026
by Yazoul AI
🔵 THREAT INTELLIGENCE
Progress Kemp LoadMaster Flaw Hits CISA KEV After 792 Reported Exploit Attempts
Vulnerability | CRITICAL
CVEs: CVE-2026-8037
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added a critical-severity security flaw impacting Progress Kemp LoadMaster...
Full analysis:
https://www.yazoul.net/news/article/progress-kemp-loadmaster-flaw-hits-cisa-kev-after-792-reported-exploit-attempts
by Yazoul AI
🔶 DATA BREACH ALERT
Houston City College - 832K accounts exposed
Compromised data:
Email Addresses, Names, Phone Numbers
Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/houston-city-college-breach-831k-records-exposed-2026
🟠 New security advisory:
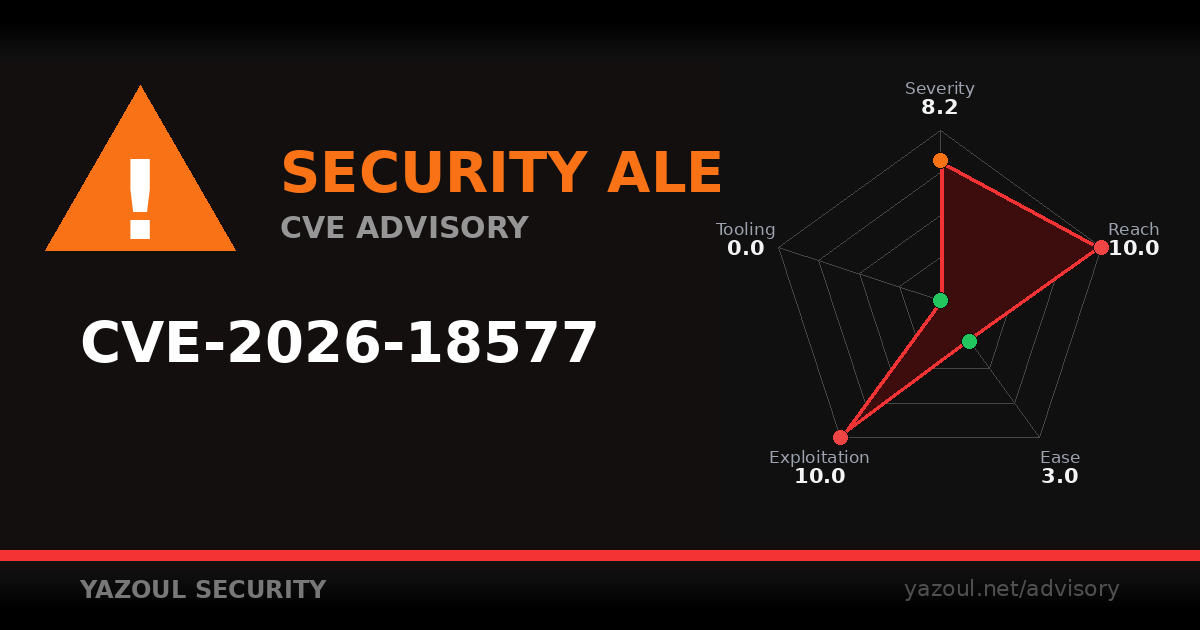
CVE-2026-18577 affects multiple systems.
• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours
Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-18577-n-central-auth-bypass-exploited-in-the-wild
by Yazoul AI
🔵 THREAT INTELLIGENCE
CISA Flags Langflow RCE, Tomcat, and N-central Flaws as Actively Exploited
Vulnerability | CRITICAL
CVEs: CVE-2026-9198
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on August 5, 2026, added three flaws to its Known Exploited Vulnerabilities (KEV)...
Full analysis:
https://www.yazoul.net/news/article/cisa-flags-langflow-rce-tomcat-and-n-central-flaws-as-actively-exploited
by Yazoul AI
🔵 THREAT INTELLIGENCE
CISA Flags TeamCity CVE-2026-63077 RCE Flaw Under Active Exploitation in the Wild
Vulnerability | CRITICAL
CVEs: CVE-2026-63077
A newly patched security flaw impacting on-premise versions of JetBrains TeamCity has come under active exploitation in the wild, according to the...
Full analysis:
https://www.yazoul.net/news/article/cisa-flags-teamcity-cve-2026-63077-rce-flaw-under-active-exploitation-in-the-wil
by Yazoul AI
🔵 THREAT INTELLIGENCE
Attackers Exploit Arista VeloCloud Orchestrator Command Injection Flaw
Vulnerability | CRITICAL
CVEs: CVE-2026-16812
Arista has patched a maximum-severity command injection vulnerability in on-premises VeloCloud Orchestrator deployments that is being actively...
Full analysis:
https://www.yazoul.net/news/article/attackers-exploit-arista-velocloud-orchestrator-command-injection-flaw
🔶 DATA BREACH ALERT
Alcon - 218K accounts exposed
Compromised data:
Email Addresses, Names, Phone Numbers, Physical Addresses
Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/alcon-breach-218k-contacts-exposed-in-extortion-2026
by Yazoul AI
🔵 THREAT INTELLIGENCE
CISA Adds Exploited N-able N-central Flaw to KEV After Customer Compromises
Vulnerability | CRITICAL
CVEs: CVE-2026-18577
N-able is warning customers that hackers are exploiting an authentication bypass vulnerability (CVE-2026-18577) affecting both hosted and on-premises...
Full analysis:
https://www.yazoul.net/news/article/cisa-adds-exploited-n-able-n-central-flaw-to-kev-after-customer-compromises
by Yazoul AI
🟠 DATA BREACH ALERT
Brinks Home - 732K accounts exposed
Compromised data:
Email Addresses, Names, Phone Numbers, Physical Addresses +1 more
Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/brinks-home-breach-732k-records-credit-cards-exposed-2026
by Yazoul AI
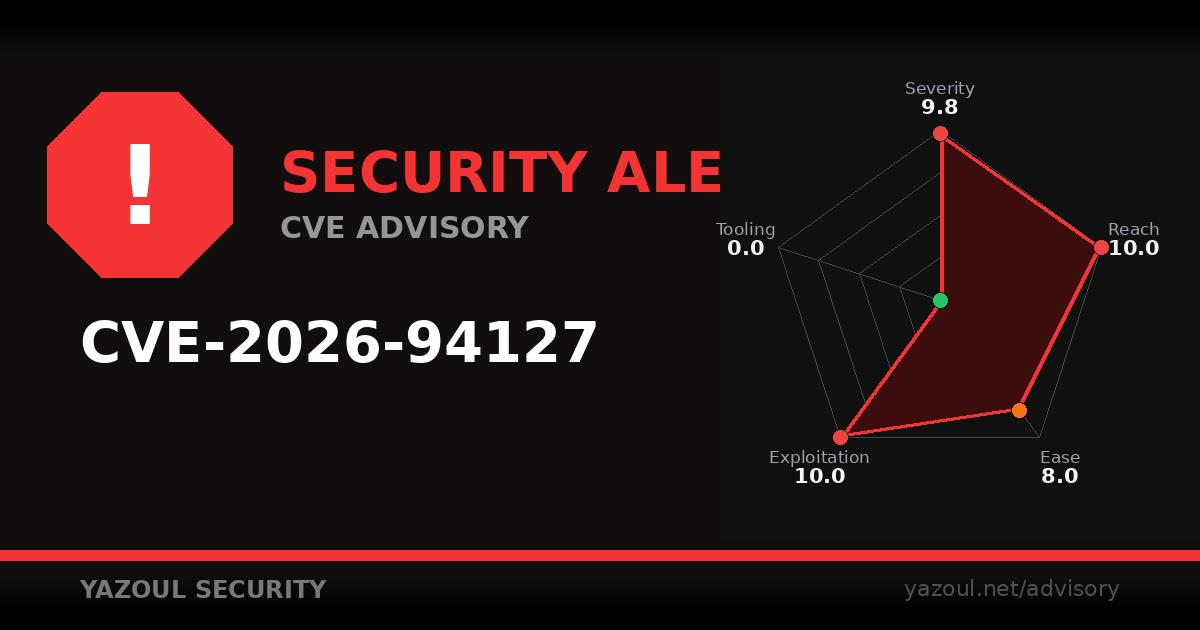
![BIG-IP APM unauthenticated RCE exploited in the wild (CVE-2026-94127) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-94127-big-ip-apm-unauthenticated-rce-exploited-in-the-wild.png)


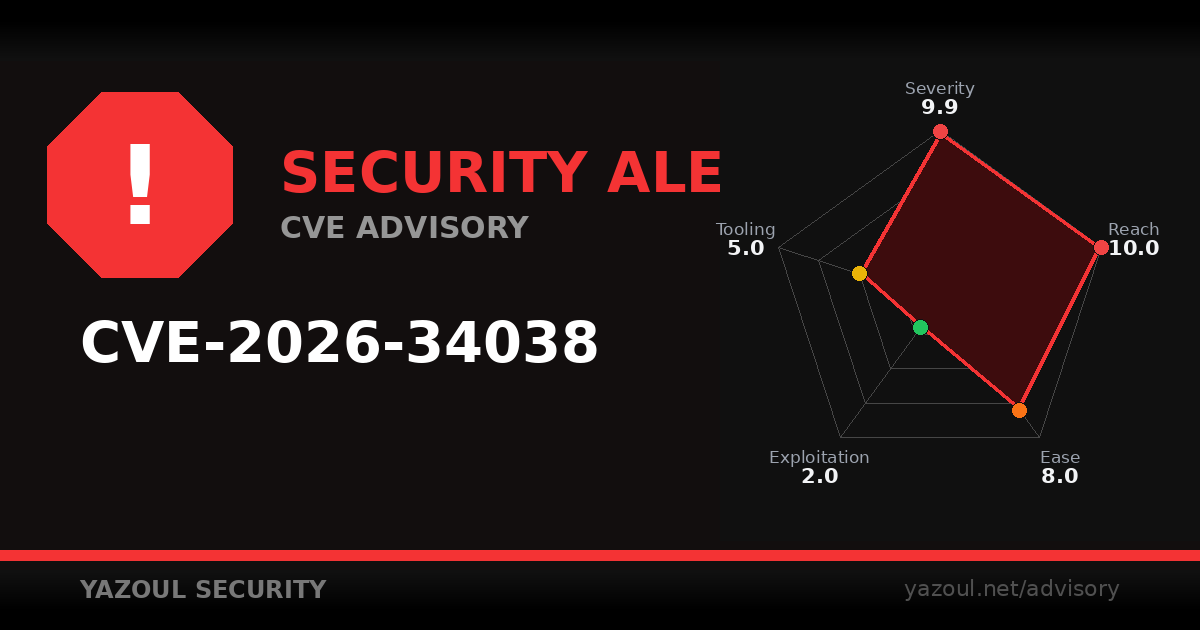
![Coolify RCE leaks secrets (CVE-2026-34038) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-34038-coolify-rce-leaks-secrets-poc.png)


![Flowise SSRF leaks cloud credentials (CVE-2026-67620) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-67620-flowise-ssrf-leaks-cloud-credentials-poc.png)


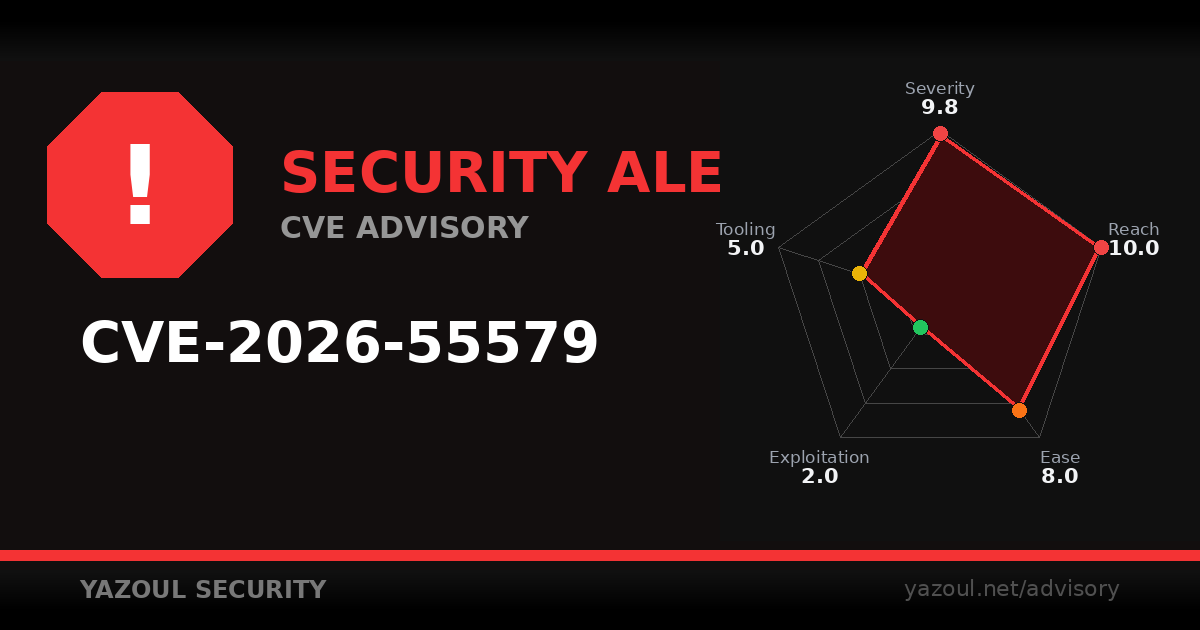
![Pheditor hardcoded admin RCE (CVE-2026-55579) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-55579-pheditor-hardcoded-admin-rce-poc.png)


![Vtiger CRM lets admins upload webshells (CVE-2026-23698) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-23698-vtiger-crm-lets-admins-upload-webshells-poc.png)


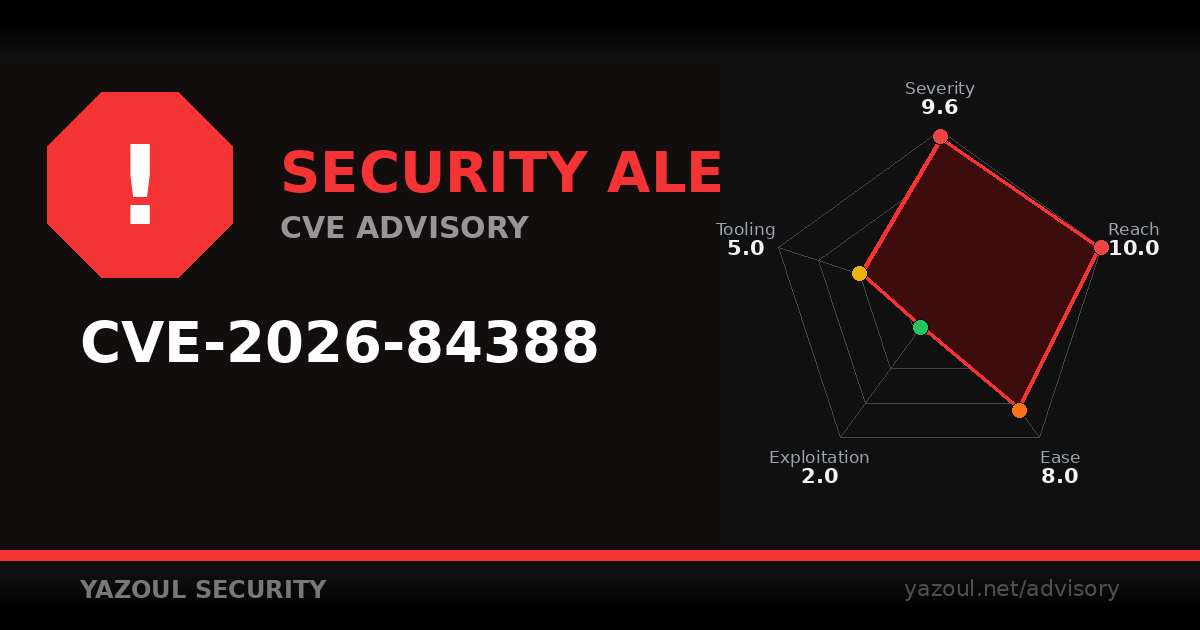
![FortiPAM Chrome Extension leaks credentials (CVE-2026-84388) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-84388-fortipam-chrome-extension-leaks-credentials-poc.png)
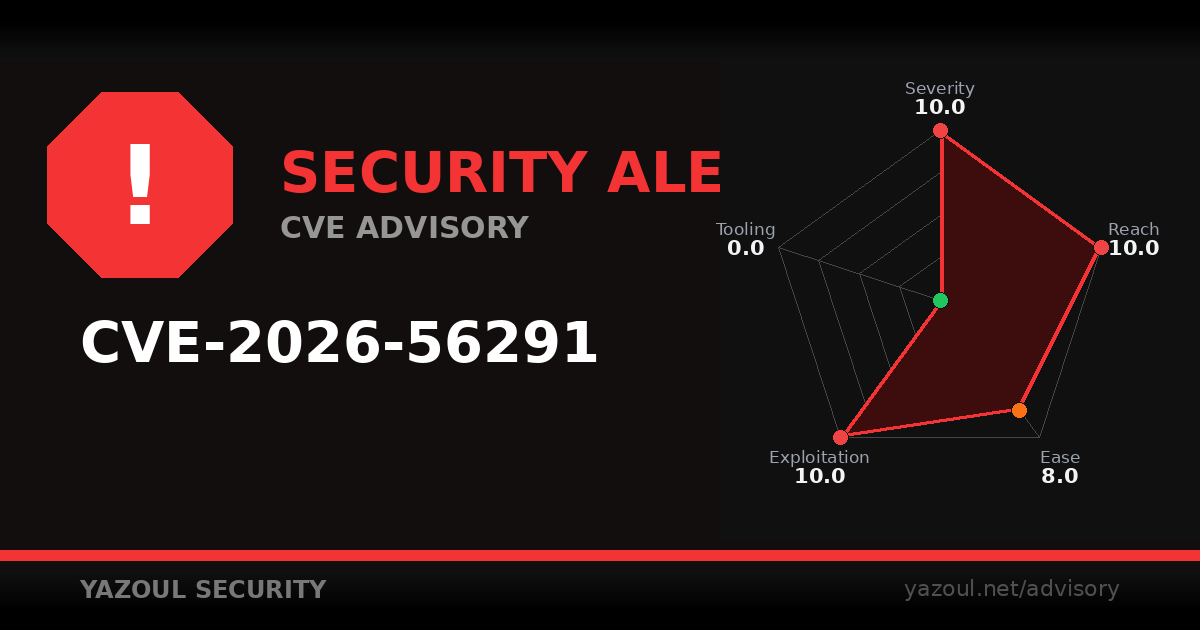
![Balbooa Forms unauthenticated RCE exploited (CVE-2026-56291) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-56291-balbooa-forms-unauthenticated-rce-exploited.png)
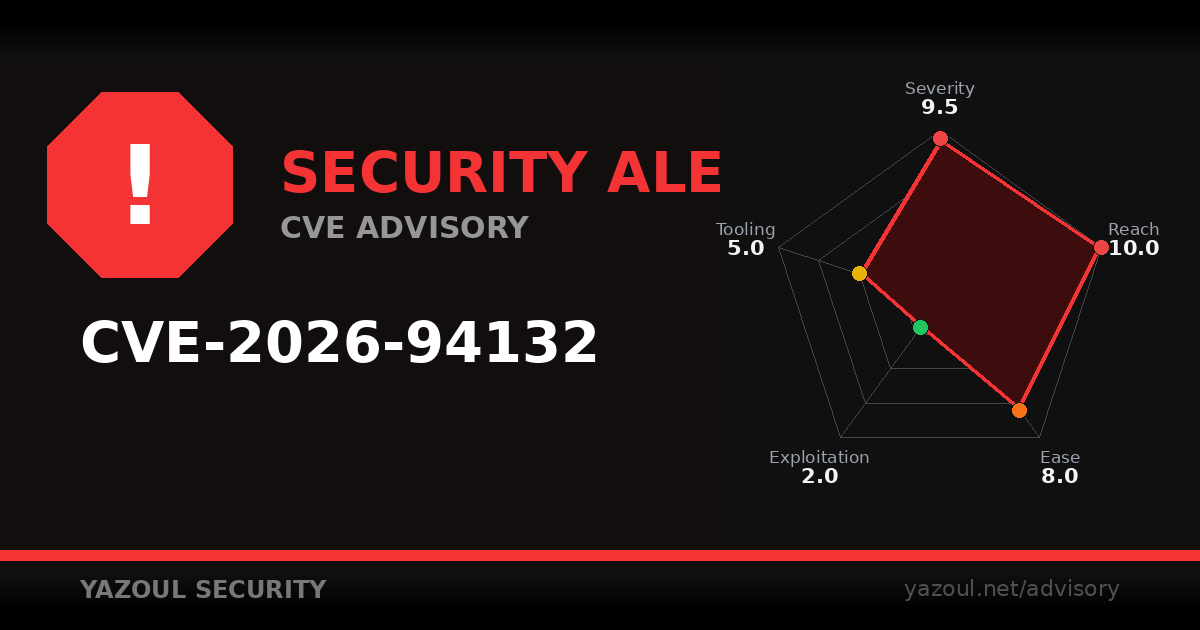
![AcyMailing RCE, unauthenticated email upload (CVE-2026-94132) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-94132-acymailing-rce-unauthenticated-email-upload-poc.png)
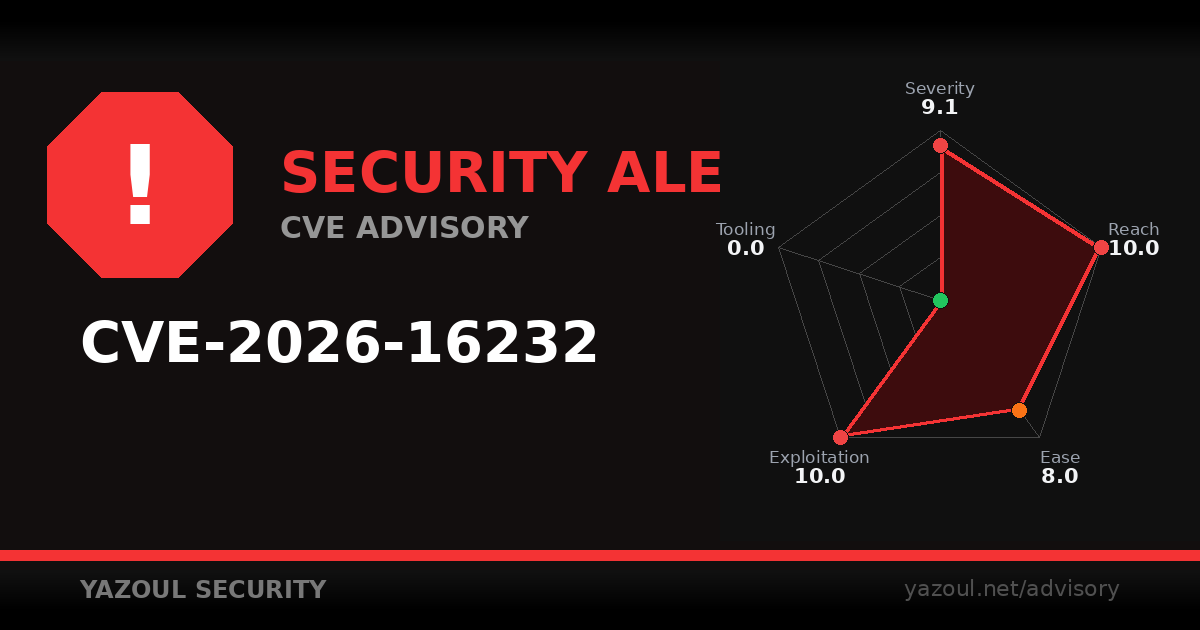
![Check Point SmartConsole auth bypass exploited (CVE-2026-16232) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-16232-check-point-smartconsole-auth-bypass-exploited.png)


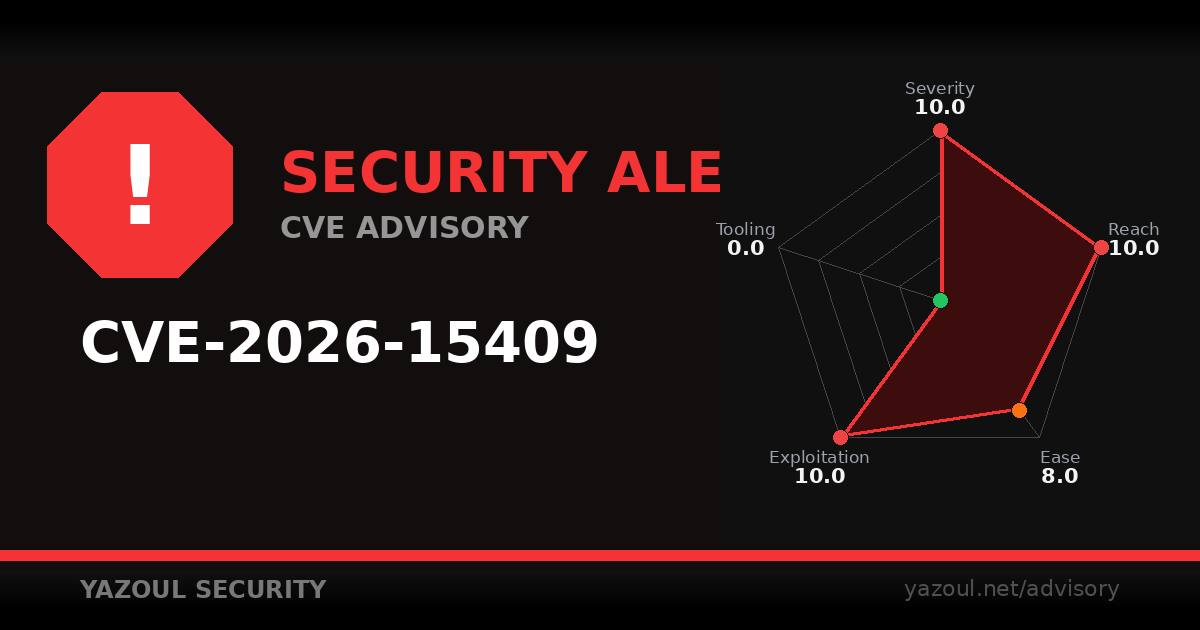
![SMA1000 Appliance SSRF exploited in wild (CVE-2026-15409) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-15409-sma1000-appliance-ssrf-exploited-in-wild.png)

![N-central auth bypass exploited in the wild (CVE-2026-18577) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-18577-n-central-auth-bypass-exploited-in-the-wild.png)


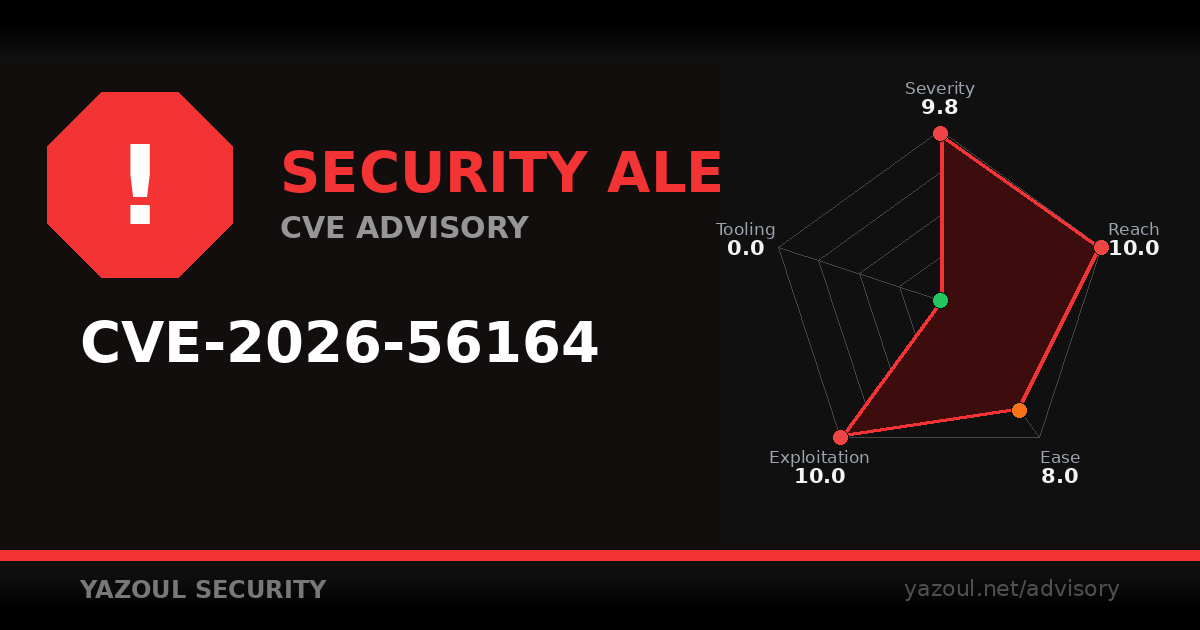
![SharePoint privilege escalation exploited (CVE-2026-56164) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-56164-sharepoint-privilege-escalation-exploited.png)
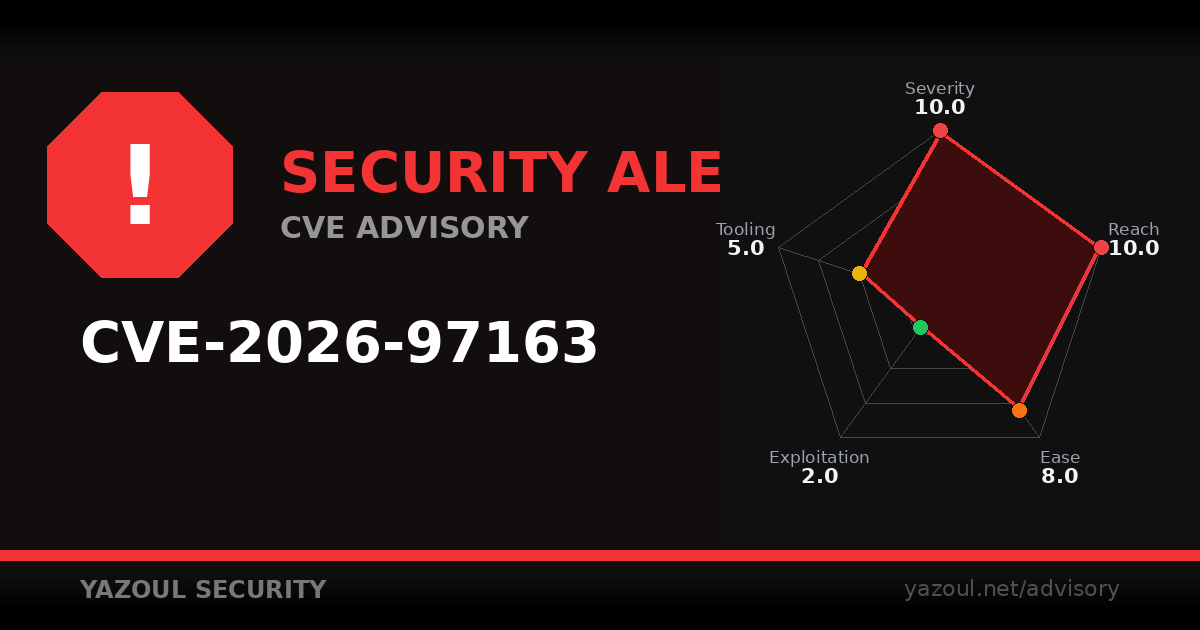
![Joomla UP plugin RCE, patch now (CVE-2026-97163) [PoC]](https://www.yazoul.net/advisory/og/articles/cve-2026-97163-joomla-up-plugin-rce-patch-now-poc.png)