Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

DevaOnBreaches

@DevaOnBreaches@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Sharing insights on data breach investigations, information security, & password best practices • @XposedOrNot@infosec.exchange

1455 Followers
4935 Following
50 Posts
Joined November 24, 2022
Website:
https://XposedOrNot.com
Blog:
https://blog.xposedornot.com/
GitHub:
https://github.com/DevaOnBreaches
Website:
https://plus.xposedornot.com/
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2w ago
The FBI is investigating claims by hacker group ShinyHunters that it exploited a zero-day bug in software used by FBIJobs and stole 2–3 TB of data, potentially including personal information on current/former employees and applicants. #databreachhttps://arstechnica.com/tech-policy/2026/09/fbi-rushes-to-investigate-if-shinyhunters-hack-of-thousands-of-employees-is-real/
FBI rushes to investigate if ShinyHunters hack of thousands of employees is real
Ars Technica

FBI rushes to investigate if ShinyHunters hack of thousands of employees is real

It's unclear what will happen if FBI misses ShinyHunters' deadline.

2
2
6
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
The best sysadmin work leaves no trace. Certs renewed. Backups that actually restore. Maintenance windows you slept through. Tools, tech, the thinking. All learned on the job. Happy SysAdmin Day. If you work with one, say it out loud today.
3
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
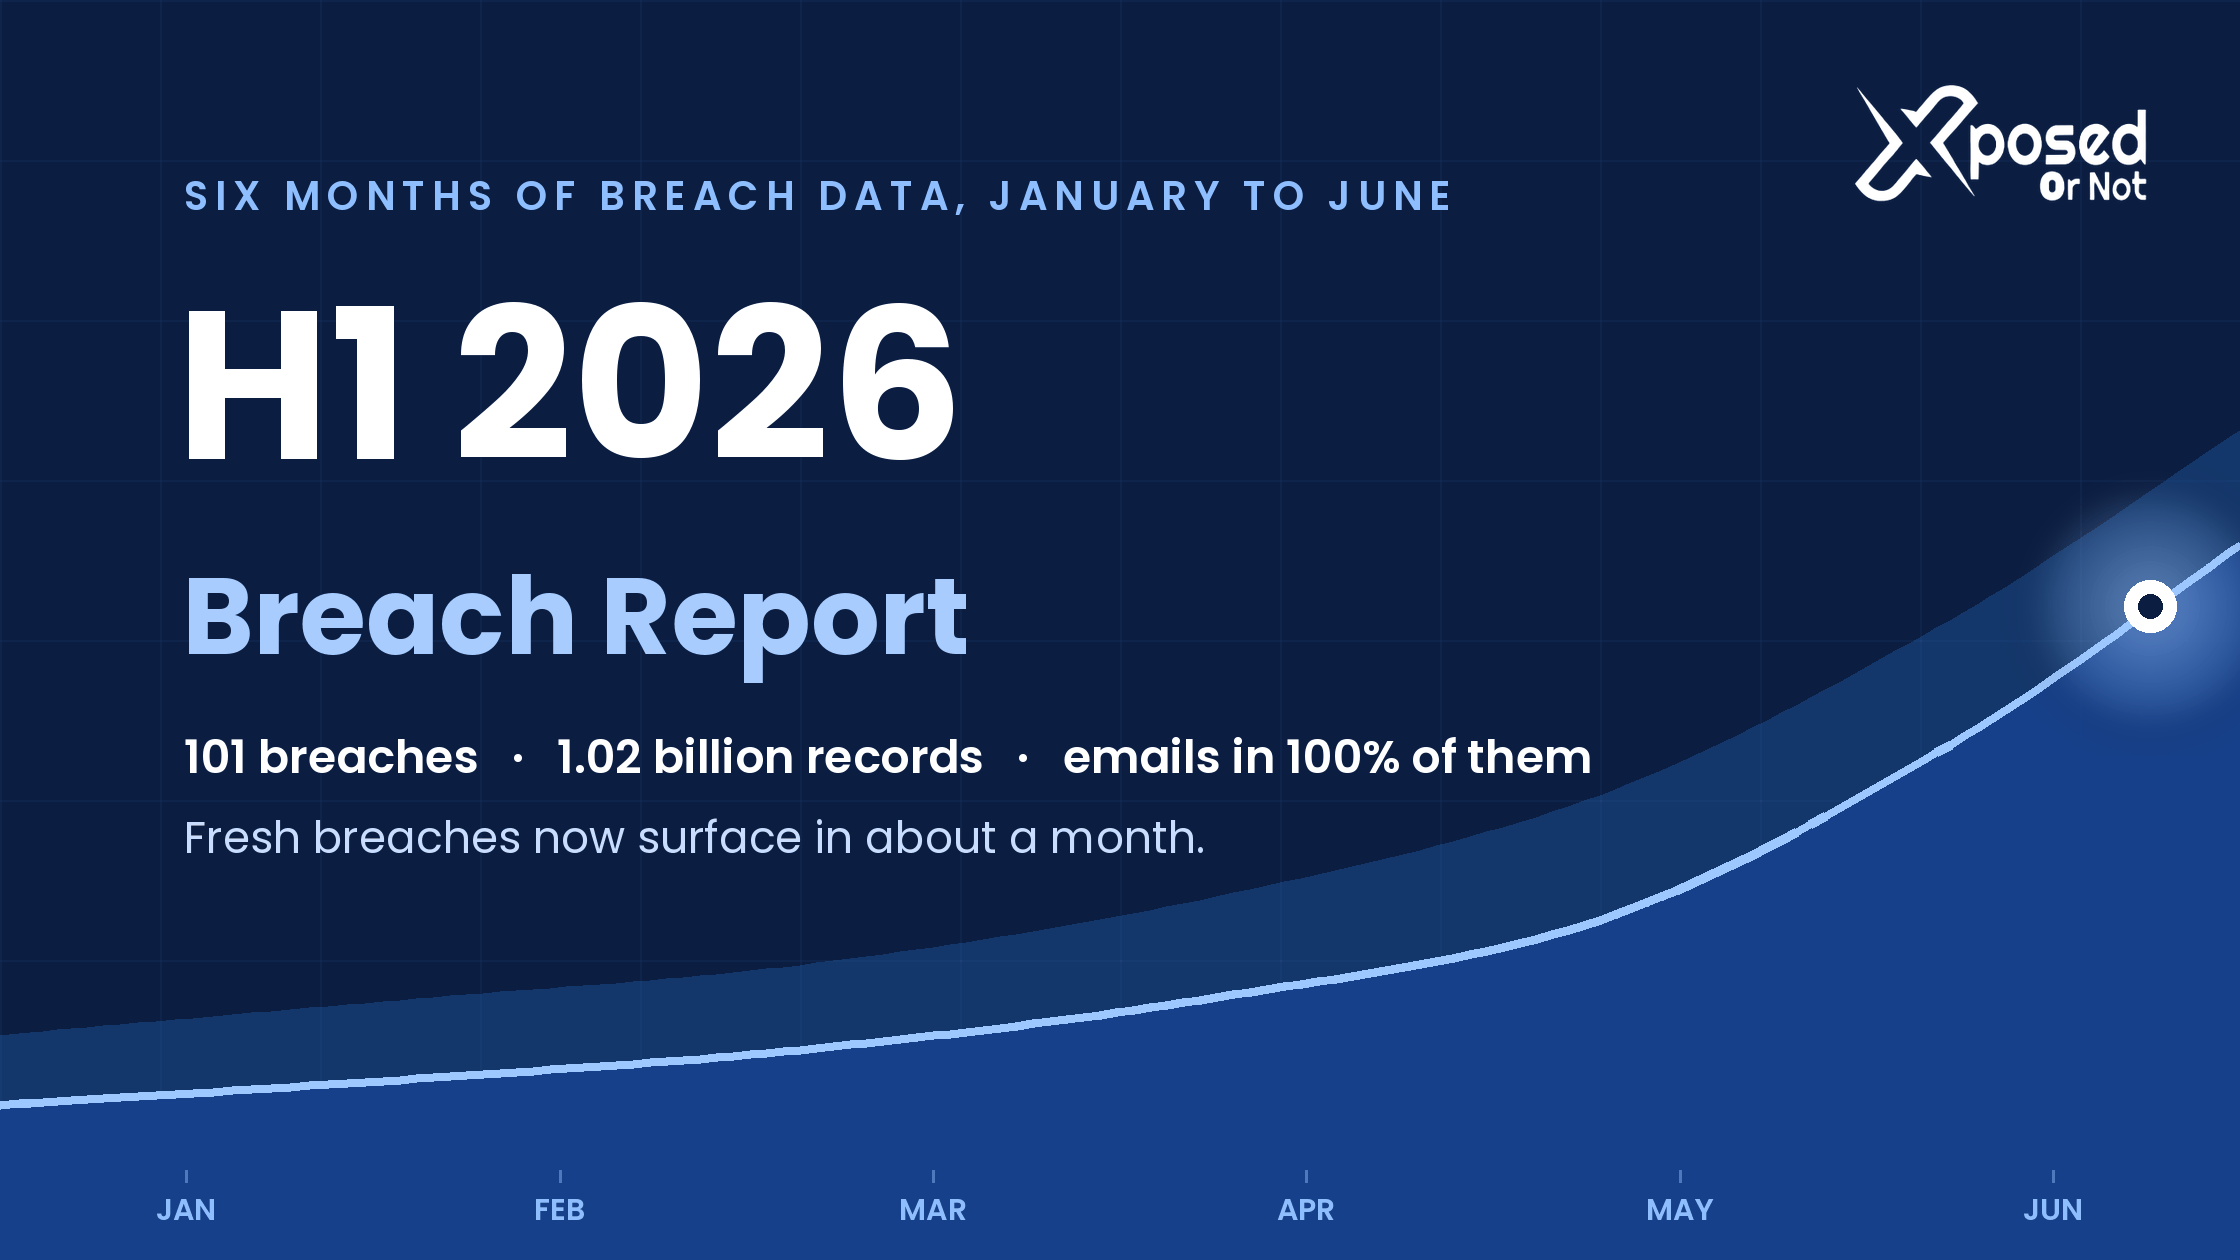
101 breaches. 1,024,063,499 records. That was H1 2026 in my breach index. Fresh breaches now surface in a median of 34 days. Identity data has overtaken passwords. Full report, free, no email gate, every number reproducible: 👇 https://blog.xposedornot.com/h1-2026-breach-report/#databreach @XposedOrNot@infosec.exchange
H1 2026 Data Breach Report: 101 Breaches, 1 Billion Records - Data Breach Insights
Data Breach Insights - Be Aware & Stay Secure

H1 2026 Data Breach Report: 101 Breaches, 1 Billion Records - Data Breach Insights

A billion records in six months. Our first half-yearly breach coverage report: what entered the index, what happened out there, and the two findings that change how often you should check.

3
0
5
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 3mo ago
Nextcloud exposed an unsecured database with 367,000 records, including invoices, contracts, employee and client details, and setup scripts. The company fixed the issue after it was reported. #dataleak https://cybernews.com/security/nextcloud-cloud-provider-data-leak/
Nextcloud leaks 367K records, exposing staff and clients
Cybernews

Nextcloud leaks 367K records, exposing staff and clients

Nextcloud exposed 367K records including employee data, client contracts, and infrastructure scripts through a misconfigured database, raising phishing risks.

2
0
3
1
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Framework says a third-party #databreach impacted all of its customers after hackers exploited a zero-day vulnerability at business intelligence provider Metabase. Exposed data includes names, emails, phone numbers, and physical addresses. Payment information was not compromised. https://techcrunch.com/2026/08/07/computer-maker-framework-notifies-all-customers-of-a-data-breach/
Computer maker Framework notifies 'all customers' of a data breach | TechCrunch
TechCrunch

Computer maker Framework notifies 'all customers' of a data breach | TechCrunch

Framework told "all" of its customers that hackers accessed their names, email addresses, phone numbers, and physical addresses in a data breach.

1
1
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago

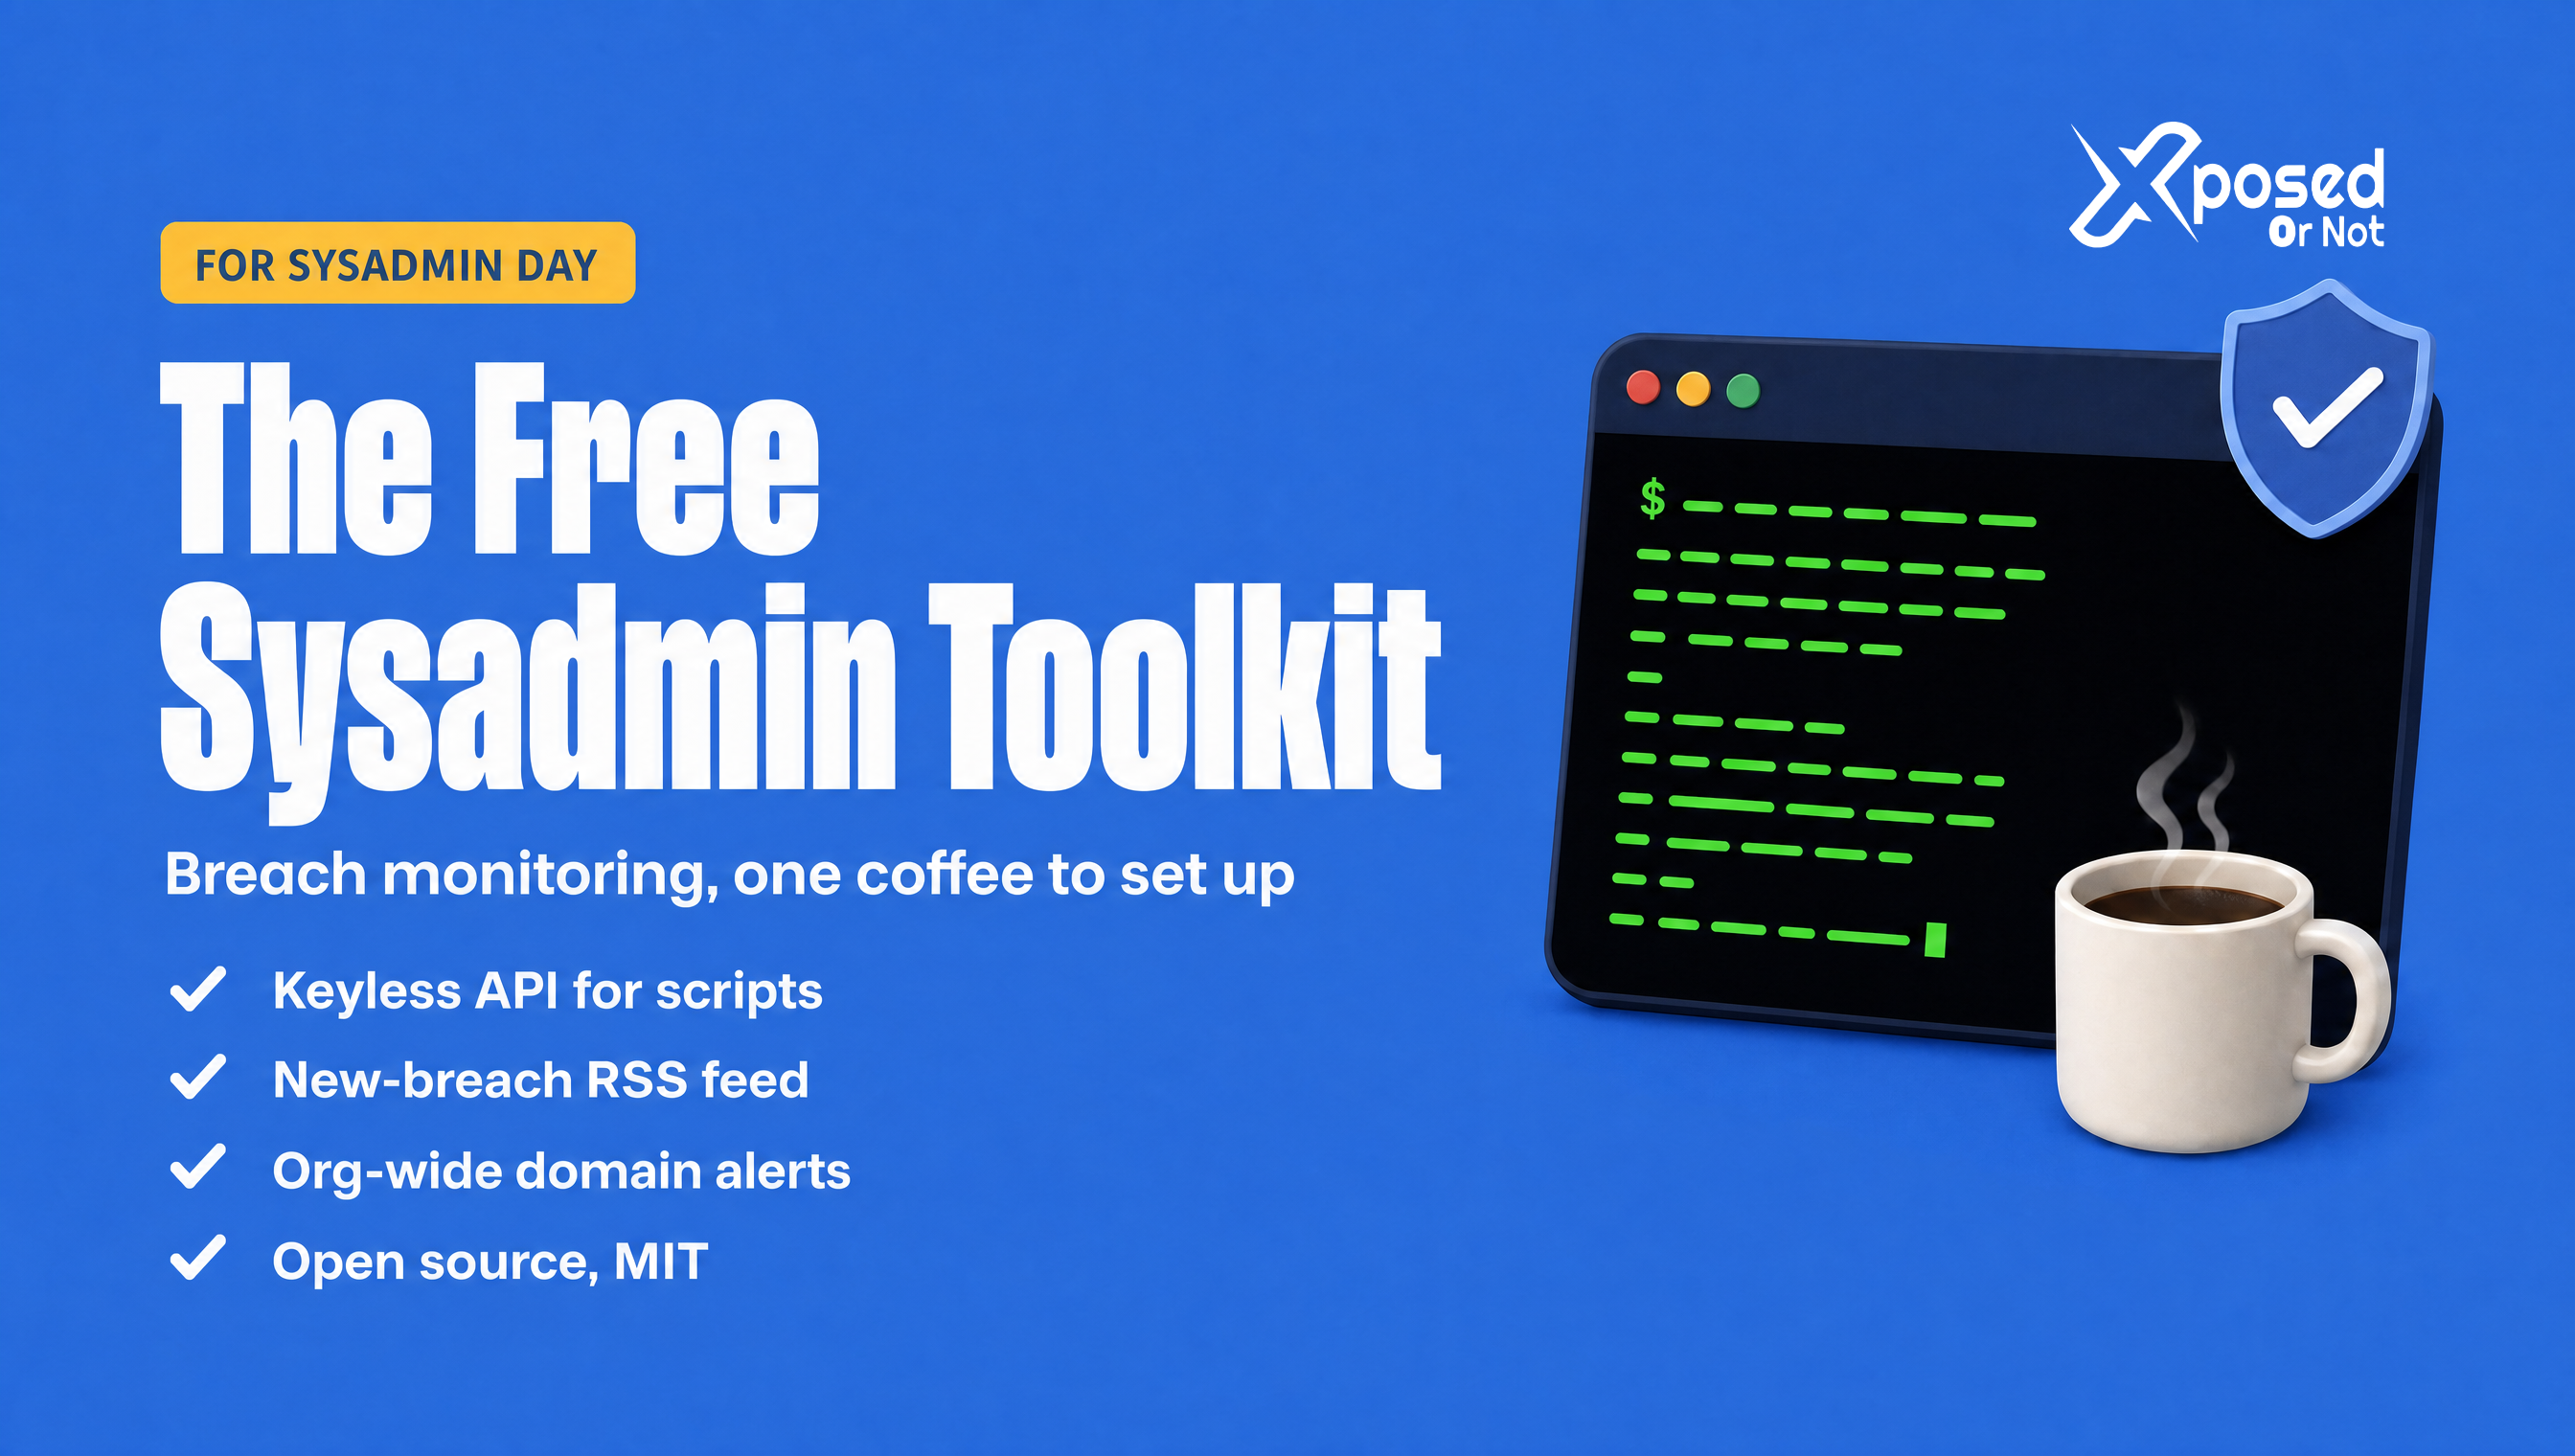
SysAdmin Day gift from XposedOrNot: a breach-monitoring toolkit that is free and open source (MIT), end-to-end.

  • check an address for breach exposure from a script, no API key
  • RSS feed of newly indexed breaches
  • verify your domain once, get alerts for every address on it
  • Microsoft Sentinel connector if you live in a SIEM

Built by someone who did the job. Setup fits in a coffee break:

https://blog.xposedornot.com/free-breach-monitoring-toolkit-sysadmins

Free Breach Monitoring Toolkit for Sysadmins: Scripts, API, Alerts - Data Breach Insights
Data Breach Insights - Be Aware & Stay Secure

Free Breach Monitoring Toolkit for Sysadmins: Scripts, API, Alerts - Data Breach Insights

Monitor every domain and employee inbox for breach exposure with free scripts, a keyless API, and Slack or Teams alerts. Built for sysadmins with no budget line.

1
0
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Healthcare billing company MCBS has disclosed a #databreach affecting 1.26M+ individuals after attackers accessed its network in 2025. Exposed data may include names, SSNs, dates of birth, insurance details, and medical records. https://www.bleepingcomputer.com/news/security/data-breach-at-medical-billing-firm-mcbs-affects-126-million-people/
Data breach at medical billing firm MCBS affects 1.26 million people
BleepingComputer

Data breach at medical billing firm MCBS affects 1.26 million people

Healthcare billing company Medical Computer Business Services (MCBS) has disclosed that a 2025 network breach exposed the sensitive information of more than 1.2 million people.

1
0
5
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Click To Pray, the Pope-backed prayer app, reportedly exposed users' names and email addresses due to a basic security flaw. A hacker says she reported it 6 months ago, but it’s still unfixed. With over 719K accounts at risk, experts warn the leaked data could be used for phishing scams. #dataleakhttps://www.theregister.com/security/2026/07/24/popes-official-prayer-app-commits-cardinal-sin-leaks-700k-users-info/5278603
theregister.com

Are we human?

1
0
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago
Replying to
@nihkeys@mastodontti.fi Actual use cases are large and beneficial. However in this case and based on the style, it maybe attributed as such. Unless and until a full forensic report is published with verifiable evidences , I do not think anything else matters.
1
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

Duc App (by Duales) exposed 360K+ sensitive files (passports, licenses, selfies, transactions) via a public, unencrypted Amazon storage bucket. #dataleak

https://techcrunch.com/2026/04/02/canadian-money-transfer-app-duc-expose-drivers-licenses-passports-amazon-server/

techcrunch.com
1
0
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

Mercor confirms #databreach tied to compromised LiteLLM supply chain attack (malicious PyPI versions live ~40 mins). TeamPCP linked to initial access; Lapsus$ claims 4TB stolen (PII, code, APIs).

https://hackread.com/ai-firm-mercor-breach-hackers-4tb-data/

AI Firm Mercor Confirms Breach as Hackers Claim 4TB of Stolen Data
Hackread - Cybersecurity News, Data Breaches, AI and More

AI Firm Mercor Confirms Breach as Hackers Claim 4TB of Stolen Data

AI firm Mercor confirms a breach linked to a LiteLLM supply chain attack, as hackers claim to have stolen 4TB of sensitive data and internal systems.

1
0
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

Drift Protocol hacked for ~$280M after attacker seized Security Council admin control via pre-signed txs + multisig manipulation (no smart contract flaw). DPRK-linked tactics suspected.

https://www.bleepingcomputer.com/news/security/drift-loses-280-million-north-korean-hackers-seize-security-council-powers/

Drift loses $280 million as North Korean hackers seize Security Council powers
BleepingComputer

Drift loses $280 million as North Korean hackers seize Security Council powers

The Drift Protocol lost at least $280 million after a threat actor took control of its Security Council administrative powers in a planned, sophisticated operation.

1
2
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

ShinyHunters (UNC6040) issues “final warning” to Cisco ahead of Apr 3, 2026, threatening to leak 3M+ stolen Salesforce records + PII, AWS & internal data. Claims tied to vishing + cloud access. #databreach

https://hackread.com/shinyhunters-hackers-cisco-records-data-leak/

hackread.com
1
0
3
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

CareCloud disclosed a March 16 cyberattack that disrupted one EHR system for ~8 hours and exposed limited patient data. Systems are now restored, attackers removed, and an investigation is ongoing with external cybersecurity experts. #databreach

https://www.bleepingcomputer.com/news/security/healthcare-tech-firm-carecloud-says-hackers-stole-patient-data/

Healthcare tech firm CareCloud says hackers stole patient data
BleepingComputer

Healthcare tech firm CareCloud says hackers stole patient data

Healthcare IT firm CareCloud has disclosed a data breach incident that exposed sensitive data and caused a network disruption lasting approximately eight hours.

1
0
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

Dutch National Police says a phishing attack briefly breached internal systems but was quickly contained.

Impact appears limited; no citizen or investigative data exposed. Probe and criminal investigation ongoing.
#databreach

https://www.bleepingcomputer.com/news/security/dutch-police-discloses-security-breach-after-phishing-attack/

Dutch Police discloses security breach after phishing attack
BleepingComputer

Dutch Police discloses security breach after phishing attack

The Dutch National Police (Politie) says a security breach resulting from a successful phishing attack has had a limited impact and hasn't affected citizens' data.

1
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

European Commission probes #databreach of an Amazon Web Services account after a hacker claimed to steal 350GB of data.

Attack was quickly contained; investigation ongoing.

https://www.bleepingcomputer.com/news/security/european-commission-investigating-breach-after-amazon-cloud-account-hack/

European Commission investigating breach after Amazon cloud account hack
BleepingComputer

European Commission investigating breach after Amazon cloud account hack

The European Commission, the European Union's main executive body, is investigating a security breach after a threat actor gained access to the Commission's Amazon cloud environment.

1
0
1
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
From our H1 breach report: 10 entries held 81.9% of the half-billion records. But the median breach? 922,685 records. Mid-sized, no headlines, same per-person damage. Mega breaches get the coverage. Median breaches get the victims. Check yours: xposedornot.com
0
0
1
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 3mo ago
Accenture has confirmed a #data breach after a hacker claimed to have stolen 35 GB of company data, including source code and security keys. https://www.bleepingcomputer.com/news/security/accenture-confirms-breach-after-hacker-offers-stolen-data-for-sale/
Accenture confirms breach after hacker offers stolen data for sale
BleepingComputer

Accenture confirms breach after hacker offers stolen data for sale

IT services giant Accenture has confirmed it suffered a security breach after a threat actor claimed to have stolen 35 GB of source code and other data from the company.

0
0
1
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
ShinyHunters has claimed responsibility for Ernst & Young's recent data breach, alleging it used a supply-chain attack to steal credentials and access EY's Jira, GitHub, and Azure environments. EY has not confirmed the claims, but says attackers stole tax-related support ticket data and is offering affected clients 24 months of identity monitoring. #databreach https://www.bleepingcomputer.com/news/security/ernst-and-young-data-breach-claimed-by-shinyhunters-extortion-gang/
Ernst & Young data breach claimed by ShinyHunters extortion gang
BleepingComputer

Ernst & Young data breach claimed by ShinyHunters extortion gang

The ShinyHunters extortion gang has claimed responsibility for a recently disclosed Ernst & Young data breach, saying it obtained credentials for some of the company's systems via a supply-chain attack.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
NYC Health + Hospitals faces new claims from extortion group LeakNet, which alleges it stole an 11TB archive affecting 12M people. So far, only 1.8M victims have been officially confirmed. The leaked samples appear sensitive, but the 12M claim remains unverified pending independent review and an official response. #databreachhttps://hackread.com/leaknet-11tb-stolen-nyc-health-hospitals-data-breach/
LeakNet Claims 11TB of Data Stolen in NYC Health + Hospitals Breach
Hackread - Cybersecurity News, Data Breaches, AI and More

LeakNet Claims 11TB of Data Stolen in NYC Health + Hospitals Breach

LeakNet claims it stole 11TB of NYC Health + Hospitals data containing sensitive medical, financial and biometric records linked to more than 12 million people.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
"Free breach monitoring" usually means "we eat the cost until we can't." Here is how @XposedOrNot@infosec.exchange stays free: Google Cloud with Datastore for the breach index, Cloudflare in front for caching and abuse handling, and a codebase you can read end to end. The expensive part of this problem is curation, not serving. Serving your slice of already-compiled breach data costs close to nothing at the edge. The code is public. If it earns it, a star helps others find it: https://github.com/XposedOrNot/XposedOrNot-API
GitHub

GitHub - XposedOrNot/XposedOrNot-API: Open-source API to check if an email has been exposed in a data breach and monitor breaches across your verified domains. Real-time alerts and breach analytics protect your online identity.

Open-source API to check if an email has been exposed in a data breach and monitor breaches across your verified domains. Real-time alerts and breach analytics protect your online identity. - Xpose...

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
OnTrac disclosed a cyberattack after hackers accessed its corporate network between Mar. 20–22, with the breach detected on Mar. 23. Customer names were exposed, while other affected data remains undisclosed. #databreachhttps://www.bleepingcomputer.com/news/security/ontrac-notifies-customers-of-data-breach-after-network-hack/
OnTrac notifies customers of data breach after network hack
BleepingComputer

OnTrac notifies customers of data breach after network hack

OnTrac parcel delivery company is informing that hackers breached its corporate network and may have accessed personal details belonging to its customers.

0
0
1
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 3mo ago
NAIC, the U.S. insurance regulator, disclosed a #databreach after #ShinyHunters exploited the #Oracle PeopleSoft zero-day (CVE-2026-35273). NAIC said the attackers accessed only public reports, outdated logs, and configuration files, https://www.bleepingcomputer.com/news/security/naic-says-public-data-stolen-in-shinyhunters-peoplesoft-breach/
NAIC says public data stolen in ShinyHunters' PeopleSoft breach
BleepingComputer

NAIC says public data stolen in ShinyHunters' PeopleSoft breach

The National Association of Insurance Commissioners (NAIC) says the ShinyHunters extortion group stole only publicly available data, outdated logs, and configuration files after breaching its systems by exploiting a zero-day vulnerability in an Oracle PeopleSoft server.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
CareCloud says a March cyberattack exposed sensitive medical, financial, and personal data of at least 345,000 people after hackers accessed an AWS-hosted health records database for six days. #databreachhttps://techcrunch.com/2026/07/30/carecloud-begins-to-notify-hundreds-of-thousands-after-hackers-stole-medical-records/
CareCloud begins to notify hundreds of thousands after hackers stole medical records | TechCrunch
TechCrunch

CareCloud begins to notify hundreds of thousands after hackers stole medical records | TechCrunch

The health tech data giant, which handles vast amounts of patients' medical data, said hackers struck one of its protected health data stores.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
I maintain @XposedOrNot@infosec.exchange , a catalog of 770 data breaches. 84 stored passwords in plaintext. Not hashed. Not encrypted. Just text. 1 in 9. Newest: this year. Reused a password anywhere? Assume it's readable. Here, it literally is. Free check, no signup:
0
1
1
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
South Korea disclosed a #databreach of its National Diplomatic Academy after hackers exploited a server flaw, maintaining access for 10 months (Apr 2025–Feb 2026). At least 6,000 MFA employees and diplomats had personal data (IDs, names, emails, encrypted passwords) exposed. https://www.bleepingcomputer.com/news/security/south-korea-discloses-data-breach-impacting-diplomats-worldwide/
South Korea discloses data breach impacting diplomats worldwide
BleepingComputer

South Korea discloses data breach impacting diplomats worldwide

South Korea disclosed that hackers breached the National Diplomatic Academy's online education system for ten months and stole personal information belonging to current and former employees of the Ministry of Foreign Affairs (MFA), including overseas diplomats.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Estée Lauder says hackers broke into its HR system using an Oracle software flaw and stole personal data like names, emails, SSNs, bank details, and health info. #databreachhttps://www.bleepingcomputer.com/news/security/est-e-lauder-discloses-data-breach-via-oracle-e-business-flaw/
Estée Lauder discloses data breach via Oracle E-Business flaw
BleepingComputer

Estée Lauder discloses data breach via Oracle E-Business flaw

Cosmetics giant Estée Lauder is notifying employees of a data breach after hackers exploited a flaw in Oracle E-Business Suite that the company used for human resources (HR) operations.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
A misconfigured database exposed 102,215 records (79GB) from Brazil’s Health Surveillance Information System (SISVISA), including IDs, tax numbers, addresses, inspection reports, and medical credentials. The database was secured after disclosure, but it's unclear how long it was exposed or if the data was accessed. #DataBreach https://hackread.com/brazil-health-surveillance-database-exposed-records/
Brazil Health Surveillance Database Exposed 79GB of Sensitive Records
Hackread - Cybersecurity News, Data Breaches, AI and More

Brazil Health Surveillance Database Exposed 79GB of Sensitive Records

Brazil's SISVISA health surveillance system left 102,215 files totaling 79GB open online, including tax IDs and identity documents, without password protection.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

Here’s your weekly #databreach news roundup:

Dutch National Police, European Commission, AFC Ajax, Crunchyroll, and Infinite Campus.

https://blog.xposedornot.com/weekly-databreaches-roundup-week-13-2026/

Weekly Databreaches Roundup Week 13-2026 - Data Breach Insights
Data Breach Insights - Be Aware & Stay Secure

Weekly Databreaches Roundup Week 13-2026 - Data Breach Insights

Dutch National Police, European Commission, AFC Ajax, Crunchyroll, and Infinite Campus.

0
0
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Lidl says hackers stole some customer data through one of its service providers. The online shop wasn't hacked, and passwords, payment details, and addresses are safe. #databreachhttps://www.bleepingcomputer.com/news/security/lidl-discloses-online-shop-breach-after-service-provider-hack/
Lidl discloses online shop breach after service provider hack
BleepingComputer

Lidl discloses online shop breach after service provider hack

German discount supermarket chain Lidl notified customers in Germany, Belgium, and the Netherlands that attackers stole their personal information in a breach at a service provider.

0
0
1
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Bank of Baroda confirmed that an employee email account was compromised, exposing some customer data, though core banking systems remain unaffected. #databreachhttps://www.indiatoday.in/business/companies/story/bank-of-baroda-data-leak-1tb-breach-rbi-cert-in-face-penalties-rbi-customer-safety-2957745-2026-07-28
Bank of Baroda confirms data breach. Can the lender now face penalties?
India Today

Bank of Baroda confirms data breach. Can the lender now face penalties?

Bank of Baroda has confirmed a customer data breach after an employee email account was compromised. The case now turns on regulatory scrutiny, possible penalties and the steps customers must take against phishing and misuse.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Breach check with no API key, no signup, one line: curl "https://api.xposedornot.com/v1/check-email/you@example.com" Returns every breach from the @XposedOrNot@infosec.exchange index the email appears in, as JSON. Free.
api.xposedornot.com
0
0
1
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

Hims & Hers confirms #databreach of third-party support system (Feb 4–7) via social engineering. Hackers stole customer tickets incl. names, emails + other personal data (medical records not affected).

https://techcrunch.com/2026/04/02/telehealth-giant-hims-hers-says-its-customer-support-system-was-hacked/

Telehealth giant Hims & Hers says its customer support system was hacked | TechCrunch
TechCrunch

Telehealth giant Hims & Hers says its customer support system was hacked | TechCrunch

The U.S. telehealth giant says hackers stole customer support ticket data over the course of several days in February.

0
0
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 1mo ago
Four of the files I read for the catalog aren't breaches at all. They're combolists. Someone else's homework: old email and password pairs from dozens of leaks, stacked into one file so the lot can be tried at once. 1,433,283,890 rows. Dull as a phone book. Still works, because a password from a 2016 forum is somebody's email password tonight. That's why I stopped remembering mine. Free alerts when yours turns up, on @XposedOrNot@infosec.exchangehttps://blog.xposedornot.com/password-manager-honest-case
Password Managers, From Someone Who Reads Breach Dumps - Data Breach Insights
Data Breach Insights - Be Aware & Stay Secure

Password Managers, From Someone Who Reads Breach Dumps - Data Breach Insights

Four field notes from reading 516 password-leaking breaches, an honest argument with the sceptic about single points of failure, and a 30-minute start. No product picks, no affiliate links.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
One thing I did not expect in our @XposedOrNot@infosec.exchange H1 data: months have personalities. March was a museum. Median lag 1,328 days, mostly old breaches finally making it into the catalog. April was a newsroom. Median lag 34 days, and 17 of its 22 additions were brand new. That is the healthy version, by the way. An index should breathe in both directions: surfacing the new, deepening the old. We just never let the two mix in the stats. Full report: https://blog.xposedornot.com/h1-2026-breach-report/
H1 2026 Data Breach Report: 101 Breaches, 1 Billion Records - Data Breach Insights
Data Breach Insights - Be Aware & Stay Secure

H1 2026 Data Breach Report: 101 Breaches, 1 Billion Records - Data Breach Insights

A billion records in six months. Our first half-yearly breach coverage report: what entered the index, what happened out there, and the two findings that change how often you should check.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

Silent Ransom Group hacked Orrick (after its 2023 #databreach), stole sensitive data via phishing/social engineering, and leaked it after rejecting a $1M offer as too low.

https://databreaches.net/2026/04/10/silent-ransom-group-leaked-another-big-law-firm-orrick-herrington-sutcliffe/

Silent Ransom Group leaked another big law firm: Orrick, Herrington & Sutcliffe - DataBreaches.Net
DataBreaches.Net

Silent Ransom Group leaked another big law firm: Orrick, Herrington & Sutcliffe - DataBreaches.Net

Jones Day wasn't the only big law firm to recently fall prey to threat actors variously known as Silent Ransom Group, Luna Moth, Chatty Spider, or UNC3753. Data

0
0
3
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Small update from my side. @XposedOrNot@infosec.exchange now works in Turkish and Polish too. Alongside English, that is 14 other languages you can now use, so more people can check for data breaches in the language they think in. More coming soon.
0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
The oldest breach in @XposedOrNot@infosec.exchange: gPotato 2007, exposing 2.1 million records. Nineteen years old. The people in it changed jobs, emails, and countries. The data went nowhere. Breach data doesn't expire. What's the oldest breach your email is in? Free, 10 seconds: xposedornot.com
0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Chick-fil-A disclosed a credential stuffing attack that compromised an undisclosed number of customer accounts between June 17–19, 2026. Exposed data may include names, emails, membership details, payment info, and more. Impacted users were logged out, payment methods removed, and urged to change passwords. #databreachhttps://www.bleepingcomputer.com/news/security/chick-fil-a-discloses-data-breach-after-credential-stuffing-attacks/
Chick-fil-A discloses data breach after credential stuffing attacks
BleepingComputer

Chick-fil-A discloses data breach after credential stuffing attacks

American fast food restaurant chain Chick-fil-A is notifying customers of a data breach after their accounts were hacked in a wave of recent credential stuffing attacks.

0
0
4
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Replying to
@XposedOrNot@infosec.exchange Entertainment. 220 of 770 breaches. Not even close. Retail: 107. Finance: 49. Everyone guards the bank. But everyday accounts, gaming, media, forums, are where reused passwords live. Full breakdown by industry AND by record count (the ranking flips): https://xposedornot.com/our-repository
Data Breach Repository: Statistics, Trends & Insights | XposedOrNot
XposedOrNot

Data Breach Repository: Statistics, Trends & Insights | XposedOrNot

Real-time data breach statistics, yearly trends, industry breakdowns, password risk analysis, and identity theft risk insights across thousands of breaches.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 3mo ago
Mount Royal University says hackers stole data from its file storage system and deleted files to make recovery harder. The attack disrupted campus systems, and the stolen data may include student and employee information. #databreachhttps://www.bleepingcomputer.com/news/security/mount-royal-university-confirms-breach-as-hackers-claim-attack/
Mount Royal University confirms breach as hackers claim attack
BleepingComputer

Mount Royal University confirms breach as hackers claim attack

Mount Royal University in Calgary says hackers stole and then deleted data from its file storage systems after breaching the university's network.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
The UK's Department for Education (DfE) has confirmed a #databreach affecting around 607,000 records following a cyberattack. Exposed data includes phone numbers and email addresses of individuals and organizations. https://www.bbc.com/news/articles/cq6dmgrp21po?at_medium=RSS&at_campaign=rss
Education department says 607,000 records taken in cyber attack
bbc.com

Education department says 607,000 records taken in cyber attack

The DfE says it is working closely with the National Cyber Security Centre and the National Crime Agency.

0
0
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Healthcare billing software company Craneware confirmed a cyberattack where hackers stole a significant amount of customer, employee, and partner data. #databreachhttps://techcrunch.com/2026/07/20/hackers-stole-significant-amount-of-data-from-tech-firm-relied-on-by-thousands-of-us-hospitals-and-pharmacies/
Hackers stole 'significant' amount of data from tech firm relied on by thousands of US hospitals and pharmacies | TechCrunch
TechCrunch

Hackers stole 'significant' amount of data from tech firm relied on by thousands of US hospitals and pharmacies | TechCrunch

Edinburgh-based tech firm Craneware said customer data was stolen during a cyberattack. The company makes software that thousands of U.S. hospitals, pharmacies, and clinics rely on for billing patients, potentially exposing health data.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 6mo ago

Threatactor ShinyHunters quits BreachForums post-FBI seizure, calling it “a waste of time,” and leaks updated data of 300K+ users. Warns all current forums are fake and threatens more massive data dumps. #databreach

https://hackread.com/shinyhunters-breachforums-leak-300000-user-database/

ShinyHunters Walk Away from BreachForums, Leak 300,000-User Database
Hackread - Cybersecurity News, Data Breaches, AI and More

ShinyHunters Walk Away from BreachForums, Leak 300,000-User Database

ShinyHunters leaves BreachForums, leaks data of 300,000 users, warns all active domains are fake, and threatens more leaks from forum backups.

0
0
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 3mo ago
Fashion marketplace Miinto has confirmed a #databreach after hackers accessed its order management system. Exposed data may include customer names, email and home addresses, phone numbers, and payment method types (but not full card details). https://www.theregister.com/security/2026/07/10/miinto-fesses-up-to-breach-says-customers-open-to-phishing/5269891
theregister.com

Are we human?

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
A cyberattack on the U.K.'s Police National Legal Database (PNLD) exposed the names, organizations, and email addresses of 100,000+ police officers and criminal justice professionals. ExfilSquad claims to have stolen 135,000 records, while authorities investigate. #databreach https://www.bleepingcomputer.com/news/security/exfilsquad-hackers-leak-info-of-over-100-000-uk-police-officers-staff/
ExfilSquad hackers leak info of over 100,000 UK police officers, staff
BleepingComputer

ExfilSquad hackers leak info of over 100,000 UK police officers, staff

A cyberattack on the U.K.'s Police National Legal Database (PNLD) has compromised contact data of more than 100,000 police officers and other criminal justice professionals.

0
0
2
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
You fix the family printer. You get the scary emails forwarded to you. My Circle on @XposedOrNot@infosec.exchange: invite up to 25 family and friends. Once they accept, you see their breaches, what data leaked, and which are sensitive. Open source, free, no card. https://blog.xposedornot.com/introducing-my-circle/
Introducing My Circle: Breach Monitoring for Your Family - Data Breach Insights
Data Breach Insights - Be Aware & Stay Secure

Introducing My Circle: Breach Monitoring for Your Family - Data Breach Insights

You are the family tech person. My Circle brings the people you look after into your breach dashboard, with their explicit permission, revocable by them at any time. Free, like everything else.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
My Circle is live on @XposedOrNot@infosec.exchange: free breach monitoring for the family you look after. They accept before you see anything. They can withdraw at any time; up to 25 people, free, open source. You are the family tech person. This is for you. https://blog.xposedornot.com/introducing-my-circle
Introducing My Circle: Breach Monitoring for Your Family - Data Breach Insights
Data Breach Insights - Be Aware & Stay Secure

Introducing My Circle: Breach Monitoring for Your Family - Data Breach Insights

You are the family tech person. My Circle brings the people you look after into your breach dashboard, with their explicit permission, revocable by them at any time. Free, like everything else.

0
0
0
0
Open post
DevaOnBreaches @DevaOnBreaches@infosec.exchange
· 2mo ago
Origin Energy is investigating a potential cyber incident involving unauthorized access to some customer data. The company says no credit card or bank details are believed to be affected, but has notified the ACSC and AFP as investigations continue. https://www.nine.com.au/australia-news/origin-energy-security-incident-20260722-p60hjj.html
‘A matter of urgency’: Major energy retailer hit by suspected hack
Nine.com.au

‘A matter of urgency’: Major energy retailer hit by suspected hack

According to their latest annual report the energy provider has about 4.7 million customers.

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 02:36:22 UTC