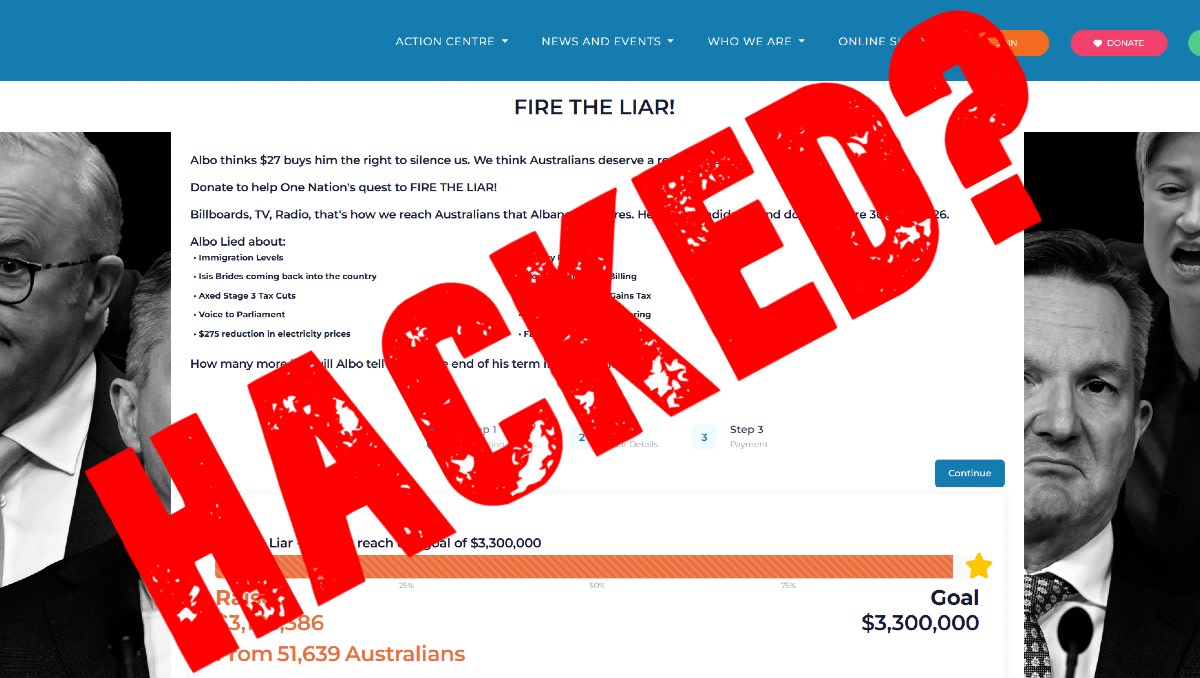
RE: https://mastodon.social/@jamesthomson/117349959097101939
Yeah - seems legit.
 mastodon 4.8.0-nightly.2026-10-06
Cyber security journalist, ex-game journo, Tolkien tragic, Twitter refugee, and traveler. All views my own.
Read my work stuff at www.cyberdaily.au. #cybersecurity #ransomware #cybercrime

RE: https://mastodon.social/@jamesthomson/117349959097101939
Yeah - seems legit.
Students and parents at another Australian school may soon have their data up for grabs on the darkweb if this threat actor follows through.
So far, St James Anglican School is doing everything it should, but schools across the board are often very poorly resourced when it comes to cyber security, despite holding such sensitive data.
Well this was a wild thing to wake up to this morning...
I'm sure these guys be feeling pretty tough after hacking a disability support charity and then bullying them into paying a ransom.
I really, REALLY hate ransomware actors. Absolutely opportunistic bastards.
It is one of those days that require I keep taking deep breaths to hold myself back from salesperson-based R A G E.
I think I'm getting closer to the source of all these Storm hacks targeting car dealerships.
Watch this space, but in the meantime, here's another one.
The Gentlemen ransomware group is anything but, and while they rarely share any details of their hacking activity in their leak posts, in this the victim has confirmed they experienced some disruption in the wake of its attack.
Welp, this is the first time I've seen a dataset like this one potentially compromised by a ransomware actor.
Family photography can be a pretty intimate affair, and probably NOT the kinda thing you want shared all over the darkweb.
But... Here we are, and with a whole lot more data besides.
I stand with my friends and colleagues at the ABC going on strike for better pay and a promise to not replace them with AI.
Without doing a proper forensic audit of the breach data it's hard to tell if this is a breach of Favelle Favco generally, or 'just' it's Australian office.
Regardless, there's a lot of Aussie data that's now circulating on the darkweb.
Has Instructure paid a ransom?
We will almost certainly never know, and I don't think any of is are in a position to judge if it has, but they've certainly come up with something to all that data safe.
The ACS is still looking into this, but the potential impact for a whole lot of IT professionals is pretty nasty.
I suspect this hack's going to be making the news for some time.
First, DragonForce came for our gelato when it hacked Gelatissimo last week, and now it's coming for our homes...
Ransomware groups seem to be multiplying fast this year, and while more than a couple of them may seem like con jobs rather than 'legitimate' data theft operations, the signs are clear.
The hacks are not going to stop any time soon. Australian organisation needs to stop focusing purely on defence, and start looking at recovery and maintaing minimum viable business processes.
I think we've got a long way to go...
No student data here, for a change, but it does look like data from a lot of mining and environmental projects from around the world have just been pretty handily compromised if what INC Ransom is saying is true.
And, so far, the data looks legit.
There are more than 500,000 public school students currently enrolled in Queensland, and there's a good chance they're all impacted by this in some way...
Can't say much about this due to an injunction (which I am sure the threat actor will ignore), but I can say this is yet *another* new ransomware operation.
#ransomware #databreach #cybersecurity
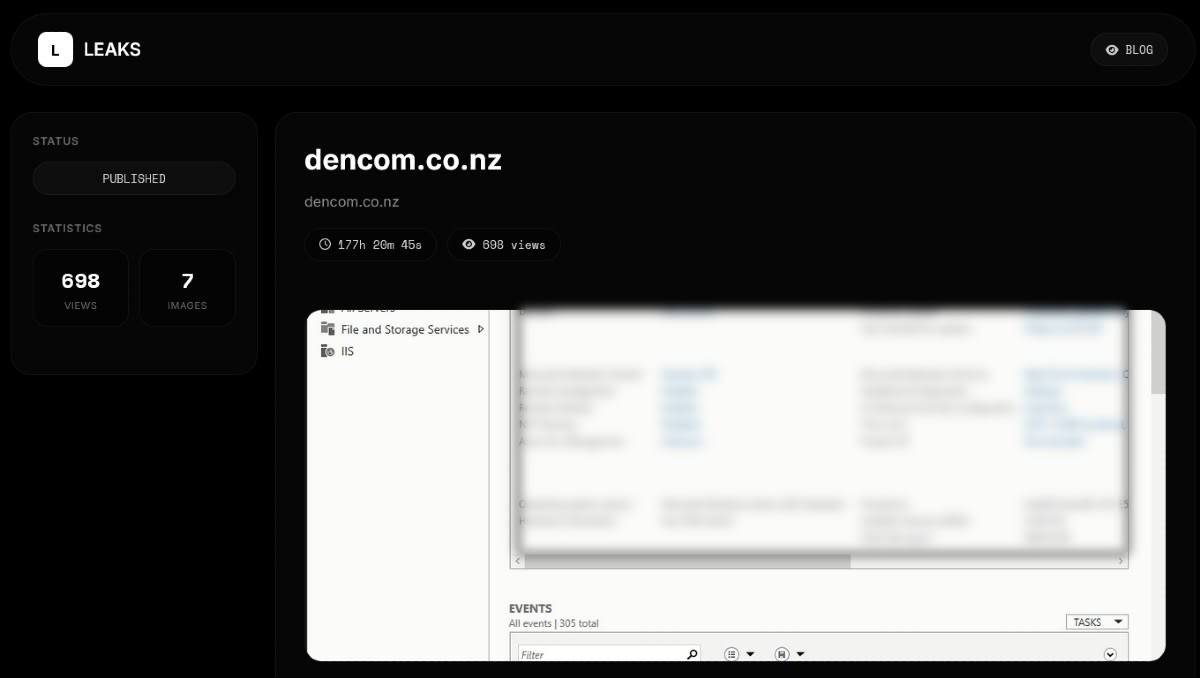
https://www.cyberdaily.au/security/13537-exclusive-kiwi-electrical-contractor-confirms-cyber-attack
If there's a lesson to be taken away from this possible data breach, it's that you should be really careful what photos you leave on work devices...
I've a suspicion the victim here runs their IT support business out of a residential address, and it occurs to that introduces a whole new layer of risk when it comes ransomware operators.
If they get into your network, and it's basically a *home* network, they're not just going to be getting your business data, but potentially your - and your family's - personal data as well.
It's taken a bit of digging but I've found the company that's the source of the recent spate of ransomware listings of Australian auto dealers and parts suppliers.
Auto IT, a maker of dealer management software, has said its a "small number of Auto-IT customers were named by an unauthorised external party on a dark web listing site".
Really glad to have gotten to the bottom of this one.
This has got to be a rough one for anyone whose payments have been impacted.
I mean, you're already struggling with debt, and then someone goes and hacks the customer management system of the charity trying to help manage your finances?
Ooft.