#fortibleed

8 posts · Last used Jul 03

🤖 FortiBleed actors now collaborating with Inc & Lynx ransomware gangs. Attackers exploit Fortinet firewall vulns + Nextcloud 0-day for initial access, monetizing thousands of compromised devices via RMM tools and supply chain credentials. 🔗 https://www.darkreading.com/threat-intelligence/fortibleed-actors-inc-lynx-ransomware-gangs #FortiBleed #Ransomware #0day #CyberSec
0
0
0
0
🚨 FortiGate admins: Stop and check 2 things TODAY RE: #FortiBleed: 1️⃣ Unexpected admin logins, config exports & config changes 2️⃣ Are ALL admin accounts using PBKDF2—not legacy SHA-256 hashes? Details 👇 https://www.linkedin.com/feed/update/urn:li:activity:7477414470378561537/
0
0
0
0
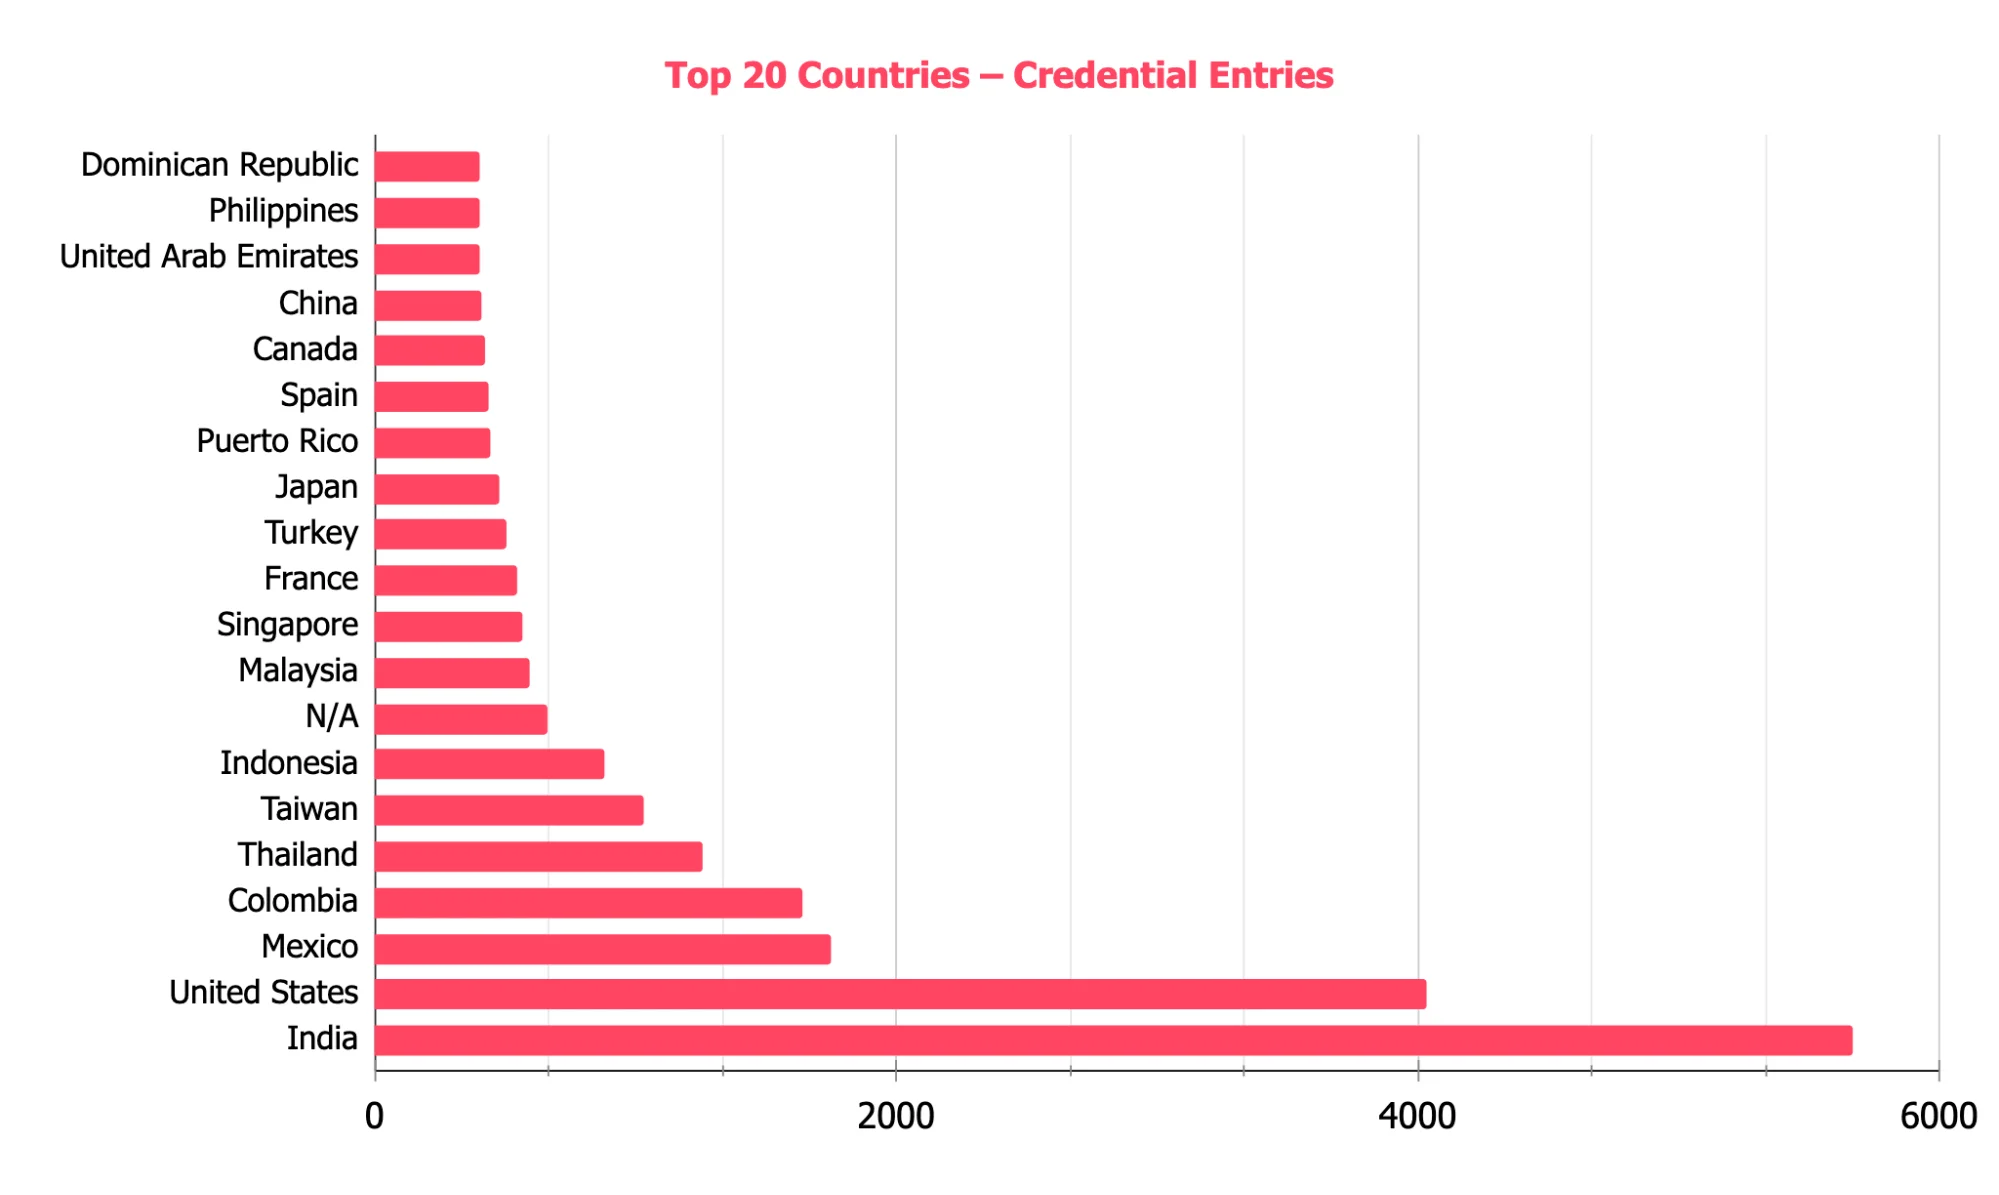
Kurzer Reminder, warum „wir nutzen das Produkt nicht" nicht dasselbe ist wie „uns betrifft das nicht": SpyCloud Labs hat bei FortiBleed nicht nur den Leak angesehen (gültige VPN-Zugänge für 74.000 FortiGate-Firewalls), sondern die Server der Täter selbst. Gescannt wurde quer durch: Fortinet, Synology-NAS, Sophos, MSSQL. Also der Mischbetrieb, der in jeder zweiten Verwaltung steht. Ablauf immer gleich: massenhaft Zugangsdaten durchprobieren, dann bei lohnenden Zielen rein – VPN, internes Netz, Active Directory, Hashes abgreifen, offline knacken. Aus „Firewall betroffen" wird „Domäne übernommen". 🧵 #ITSicherheit #Kommunen #FortiBleed
5
1
4
0
Yesterday we reported out an additional dataset found on the #Fortibleed threat actors systems in a one-off special report - https://www.shadowserver.org/what-we-do/network-reporting/fortibleed-additional-dataset-special-report/ The data was shared with us by SpyCloud (https://spycloud.com/) & covers 35000 new IPs not previously reported. The report also contains over 1000 IPs where the threat actor ran credential sniffing in June. Check out SpyCloud's analysis here: https://spycloud.com/blog/what-spycloud-found-inside-the-fortibleed-threat-actor-infrastructure/ Thank you to SpyCloud for the collaboration! Global Stats: Dashboard World Map view: https://dashboard.shadowserver.org/statistics/combined/map/?date_range=other_value&day=2026-06-26&map_type=std&source=special&data_set=count&scale=log&auto_update=on Dashboard Tree Map view: https://dashboard.shadowserver.org/statistics/combined/tree/?date_range=other_value&day=2026-06-26&source=special&data_set=count&scale=log&auto_update=on #CyberCivilDefense
8
0
7
0
Replying to
Wrote a blog about the #FortiBleed situation https://doublepulsar.com/fortibleed-75k-fortinet-firewalls-have-admin-passwords-cracked-60299faa65f8?postPublishedType=initial
43
27
48
1
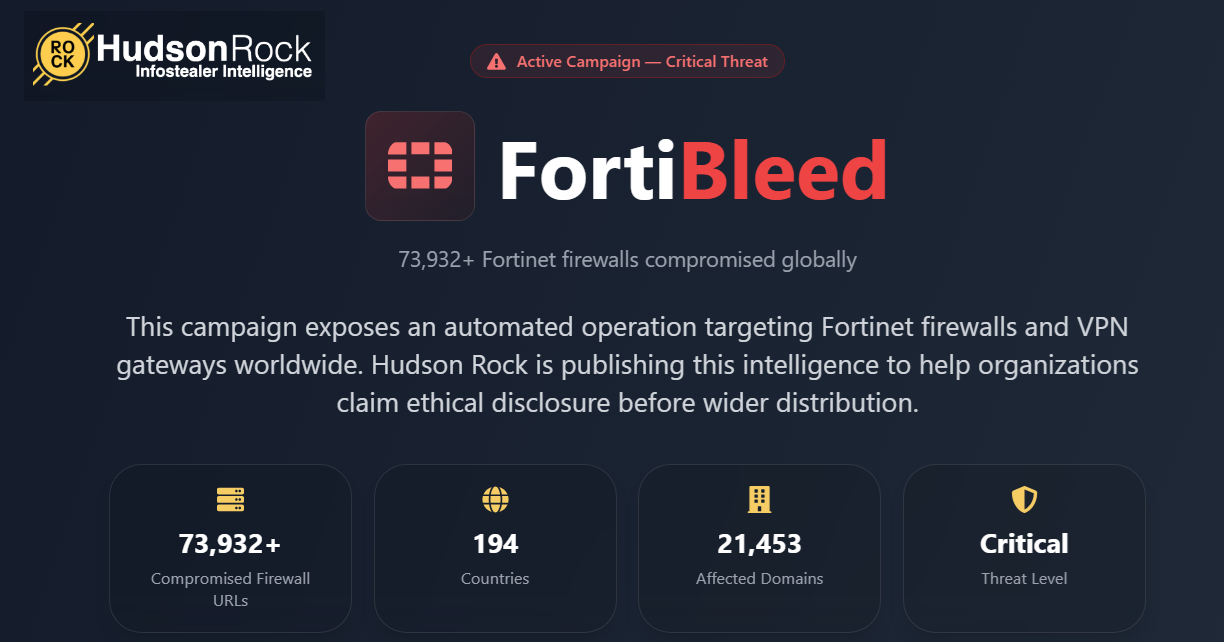
An ecrime group has somehow gained access to 75k Fortinet firewall devices - dubbed Fortibleed Blog https://www.infostealers.com/article/fortibleed-75000-fortinet-firewalls-compromised-global-enterprises-exposed-claim-your-ethical-disclosure/ Check if your domain is impacted: https://www.hudsonrock.com/fortinet I’ve verified the data is real. They’ve been dumping the Fortinet config - not sure how yet - and then cracking the passwords it appears. Data is being resold online. #fortibleed
122
47
178
2
You've seen all posts