Security advisory: Fastjson ≤ 1.2.83 RCE (CVSS 8.1 High)
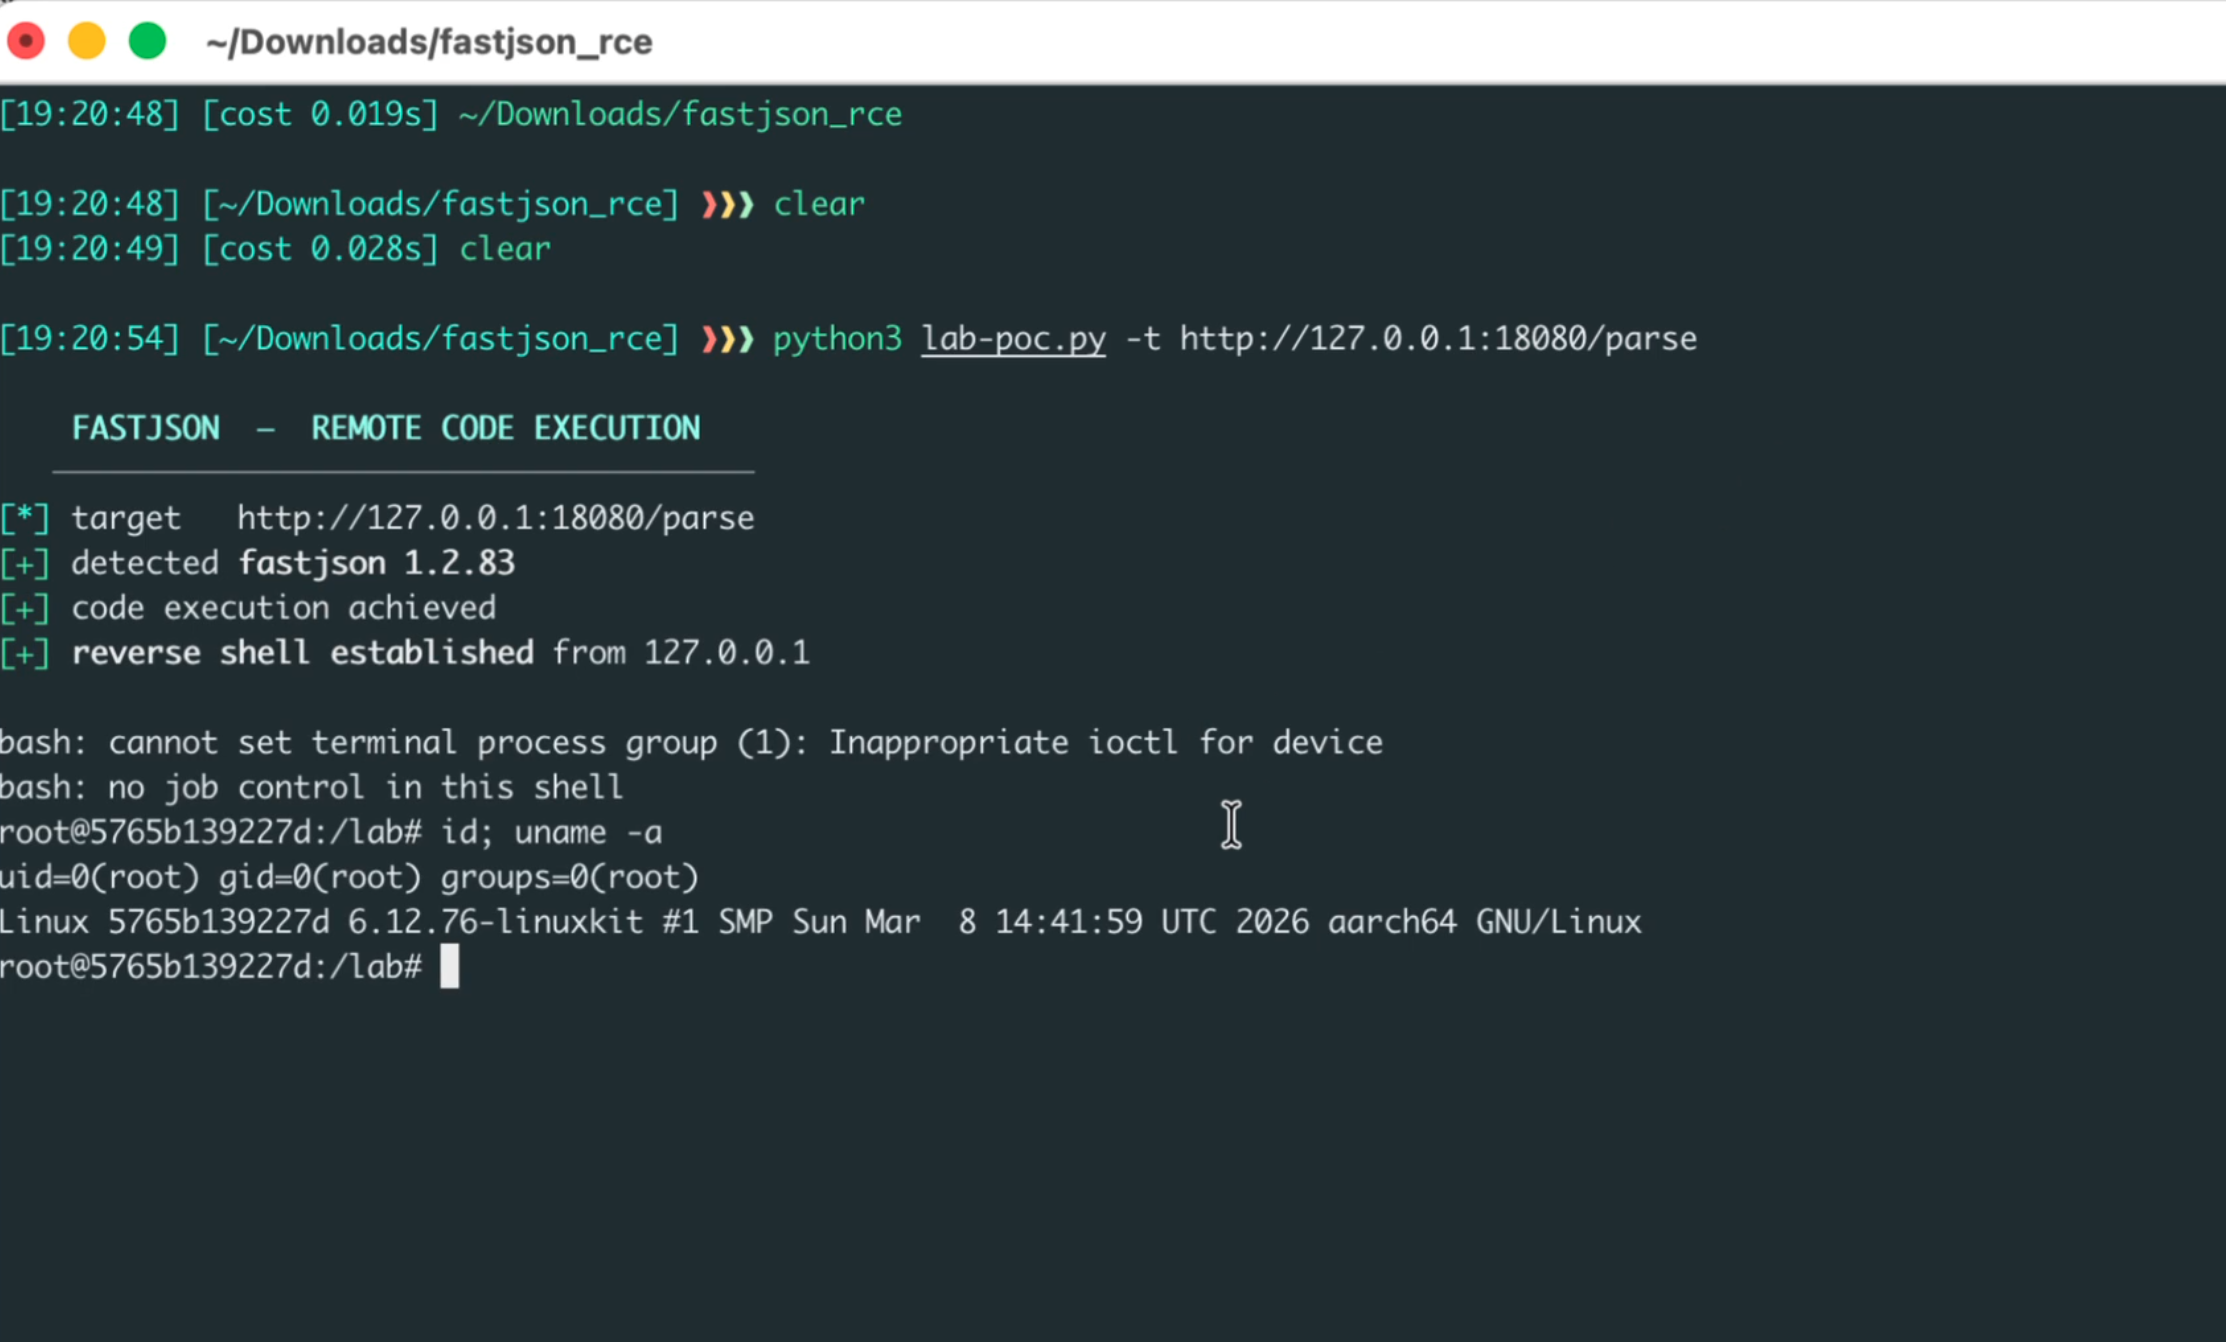
A critical remote code execution vulnerability in Alibaba Fastjson was disclosed on July 19 by Kirill Firsov (
@k_firsov), with a public PoC released on July 21 (github.com/midisec/fastjson-1.2.83-gadget-rce).
The vulnerability resides in ParserConfig.checkAutoType(). Even with AutoType disabled (default), the method performs a resource probe: the
@type class name has . replaced with / and is passed to ClassLoader.getResourceAsStream(). On Spring Boot FatJar deployments, the ClassLoader supports jar:http:// URL resolution, allowing an attacker to point the "resource path" to a remote server.
Exploit chain:
Attacker sends a JSON request with a crafted
@type value
checkAutoType() converts it to a resource path and fetches from the remote server
Fastjson's ASM reader checks the returned bytecode for
@JSONType
If found, the class is loaded and instantiated — executes arbitrary code
No classic deserialization gadgets are involved. The AutoType blacklist is irrelevant because the resource probe uses a separate code path.
ZAST.AI's semantic analysis engine can trace the complete data flow from the untrusted
@type input to the ClassLoader.getResourceAsStream() sink, identifying this resource-probe RCE pattern through static code analysis alone.
Affected: Fastjson 1.2.68 ~ 1.2.83 (1.x EOL) JDK impact: 8 (direct RCE), 17/21 (fd reuse, Linux), 25 (SSRF only)
Remediation: enable SafeMode (-Dfastjson.parser.safeMode=true) or migrate to fastjson2.
Full report:
https://blog.zast.ai/vulnerability%20research/application%20security/fastjson-checkautotype-rce-en/
ZAST.AI is currently offering free assessment during the anniversary period — upload a code package to verify Fastjson RCE and other deserialization vulnerabilities without setting up a runtime environment.
https://zast.ai/anniversary?utm_source=blog&utm_medium=organic_content&utm_campaign=zast_1st_anniversary_2026&utm_content=blog_post_en
#AppSec #Fastjson #RCE #JavaSecurity #Vulnerability #fastjsonrce #fastjson0day